

Baseline checks
Host-configuration baseline and OS end-of-life compliance patrol. A rule library, manual or daily runs, results and trends per host. Data from the CIM Endpoint and Change data models.
Baseline checks express the expected configuration of every host as rules, judge them against the endpoint data already in Splunk, and produce a score and failed items. Available in every edition.
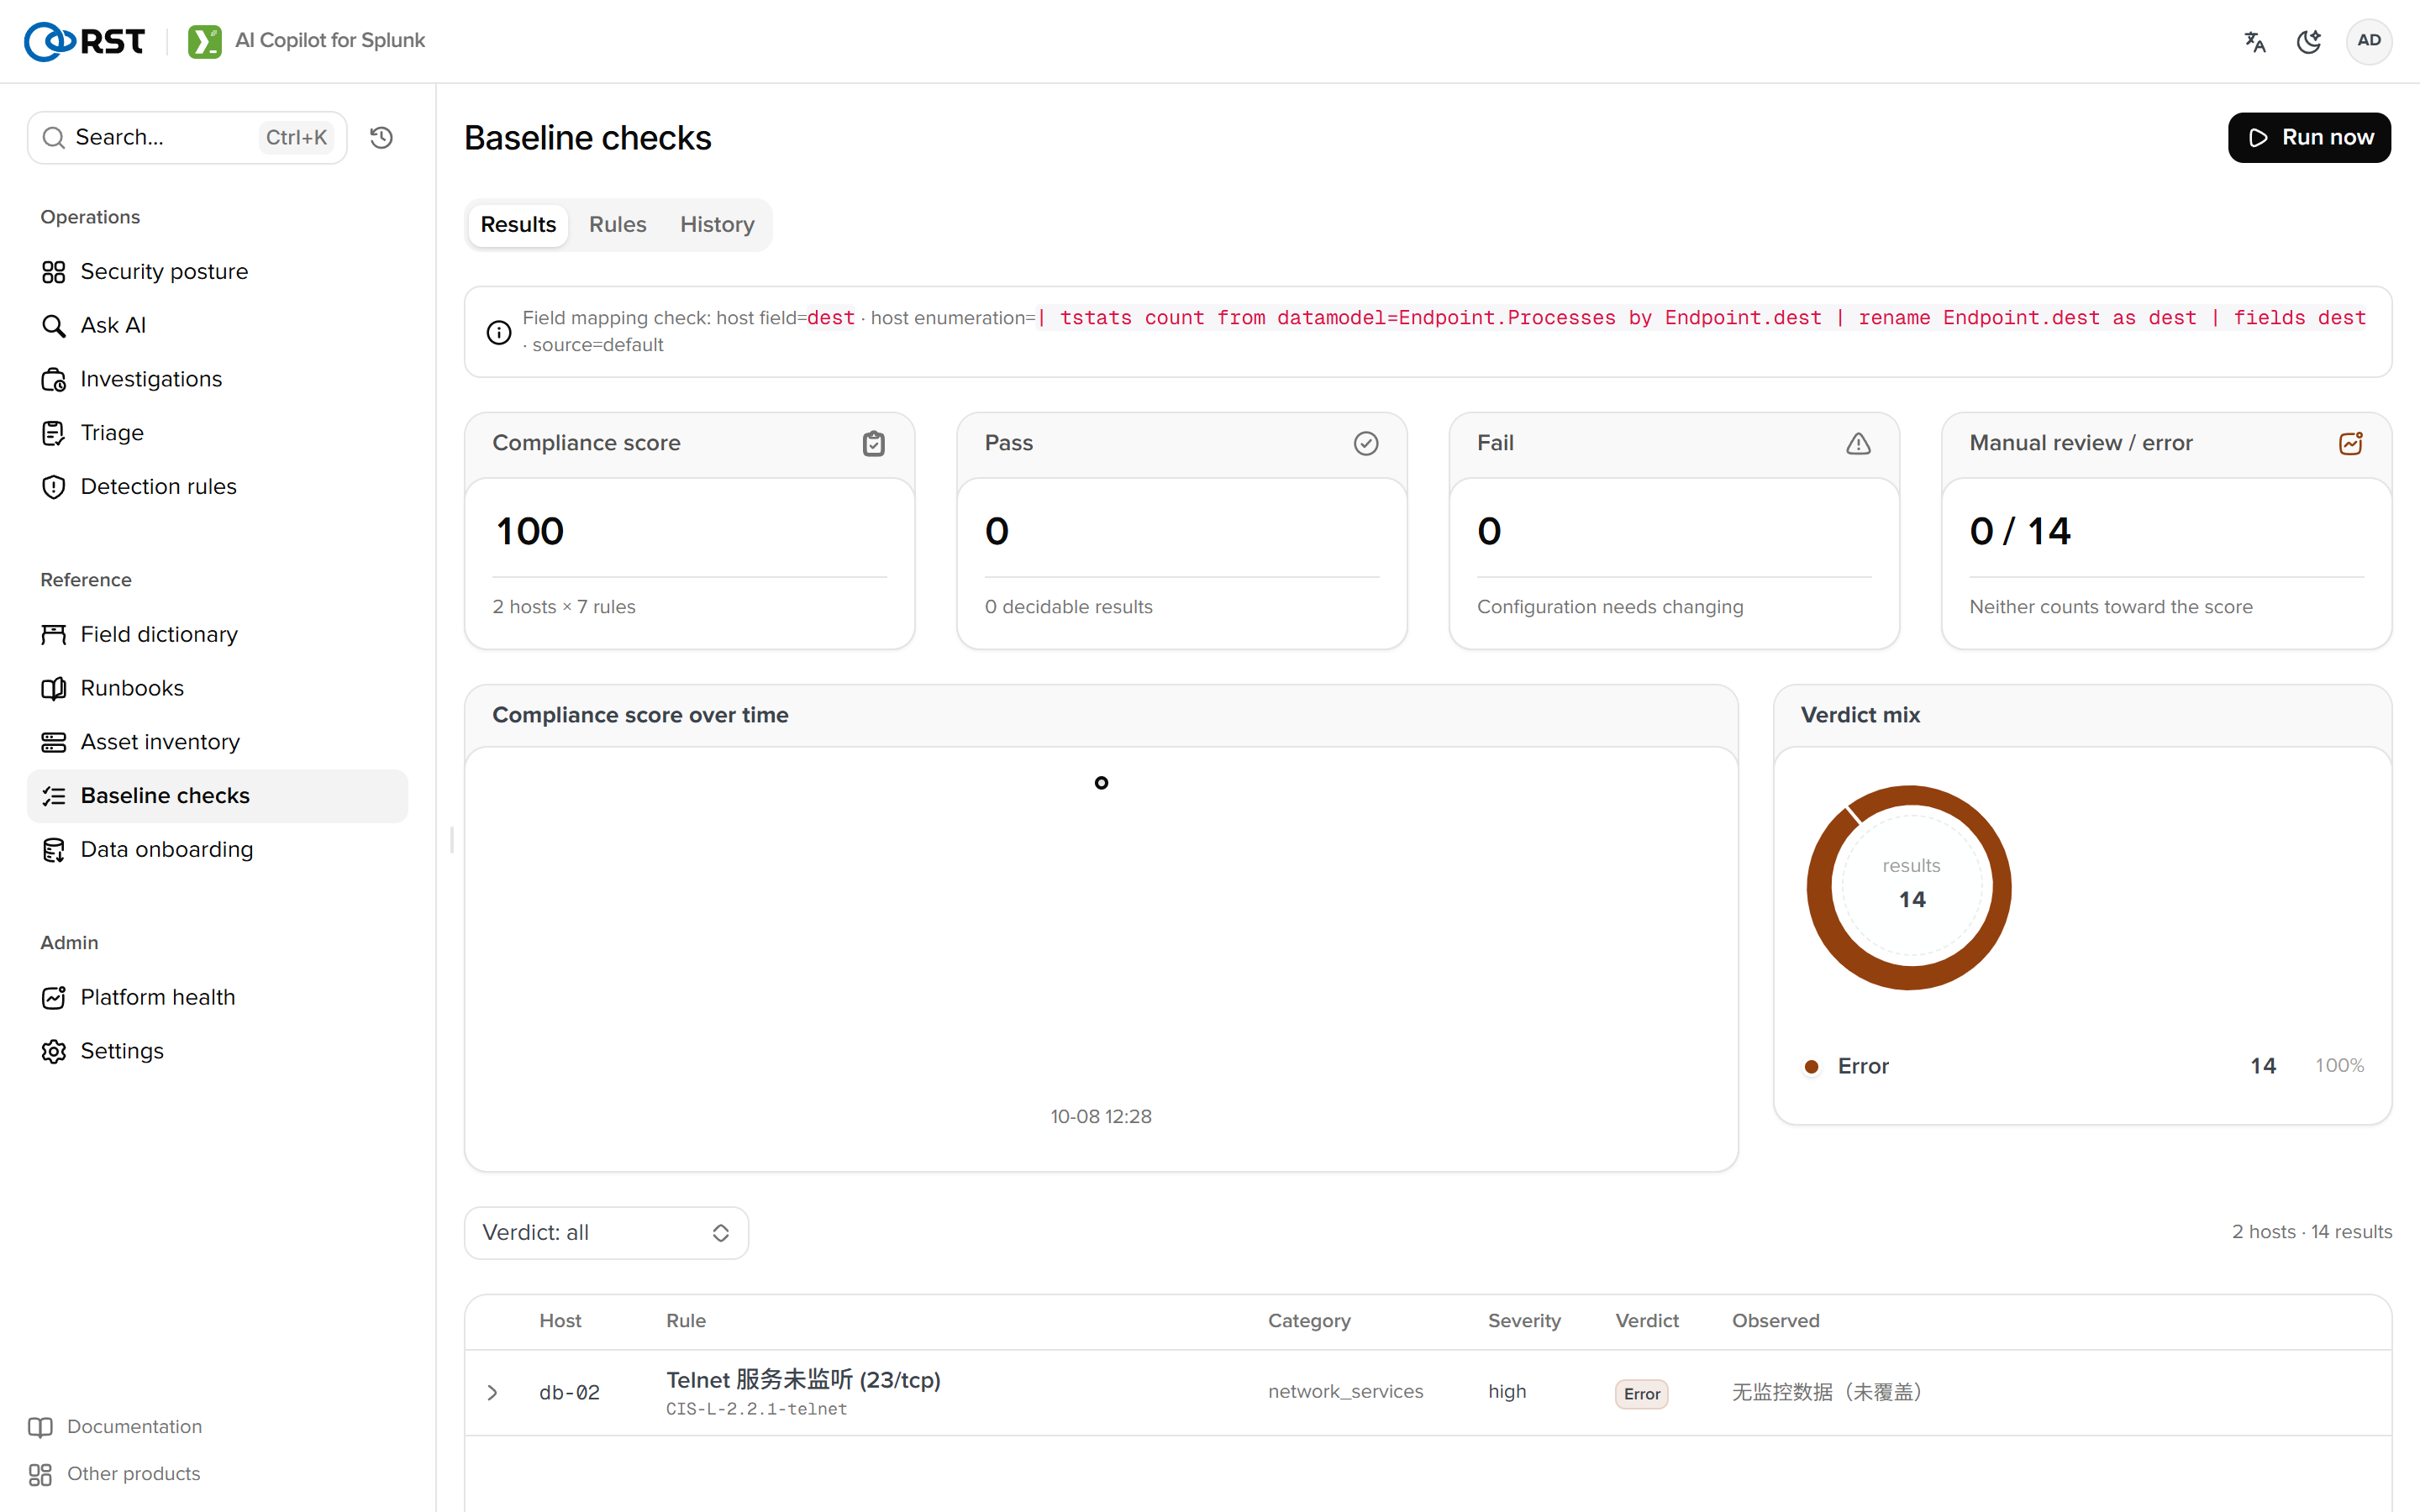
Data source
Judgements run over the CIM Endpoint (Processes, Services, Ports, Registry, Filesystem) and Change data models with tstats. An osquery TA's sourcetypes work directly. Hosts are enumerated from Endpoint.Processes by default; without CIM data a run can be given an explicit hosts=.
OS end-of-life dates come from a bundled catalogue (copilot_eol_catalog), refreshable with eol_sync.py.
Tabs
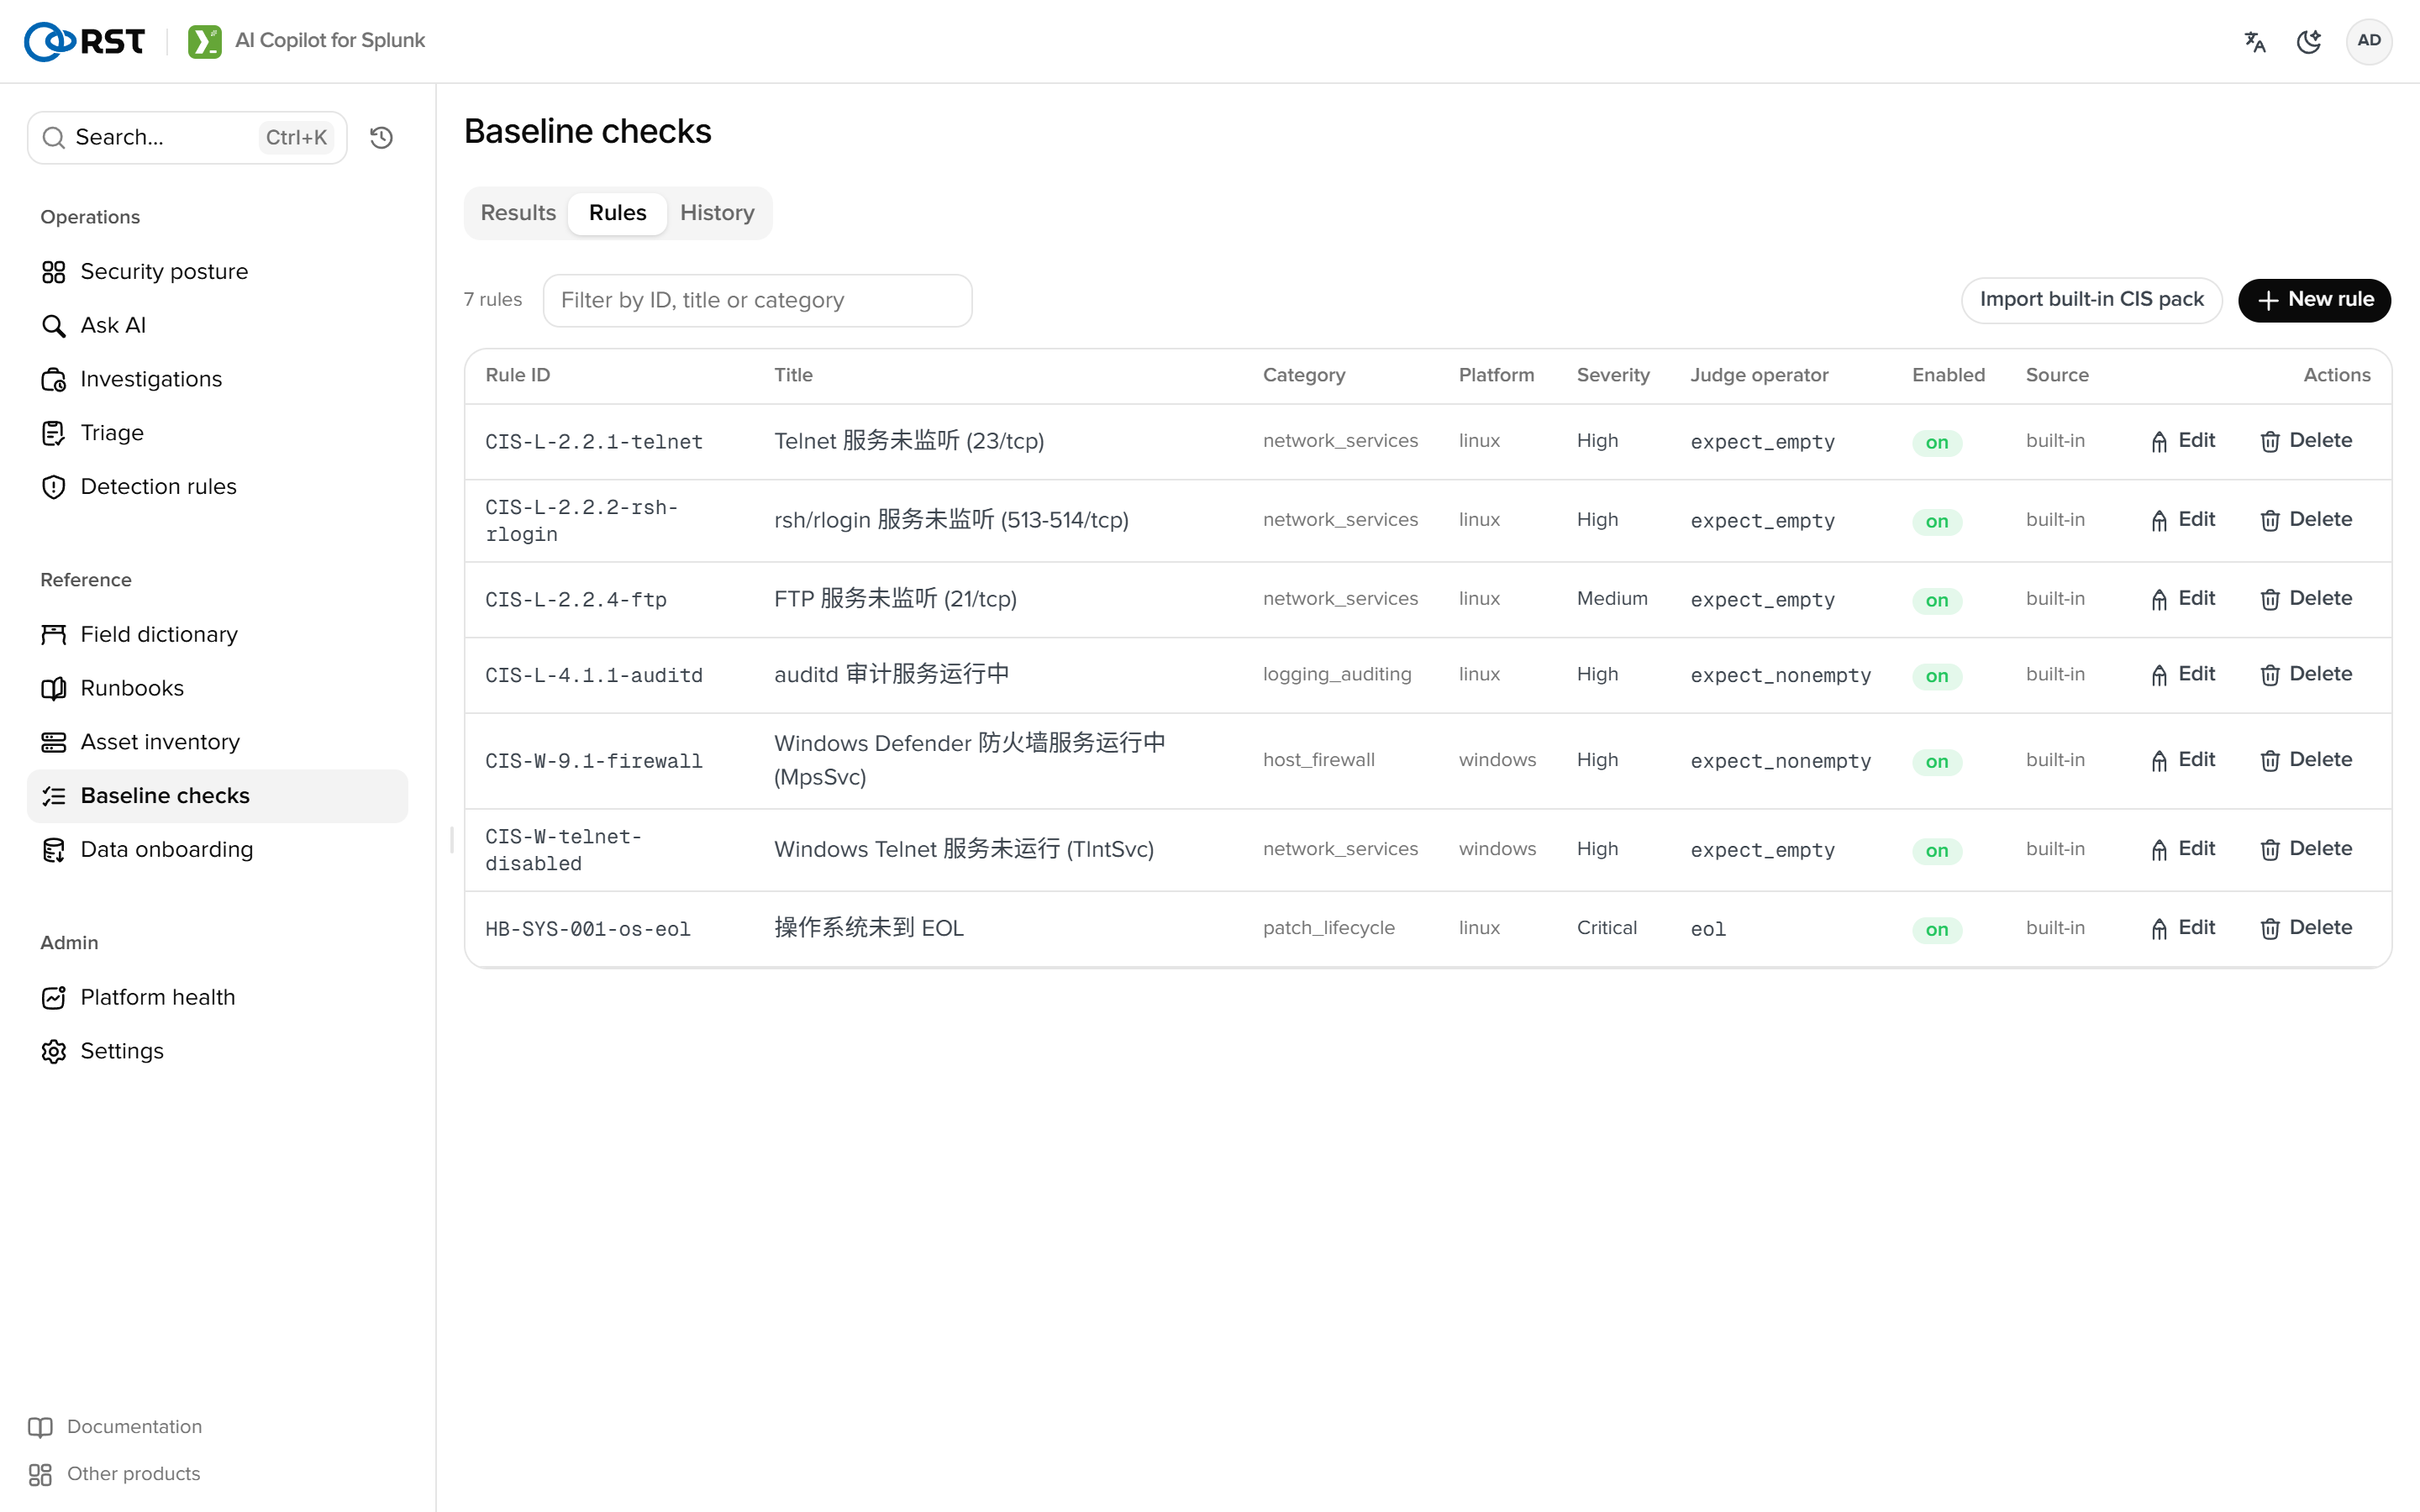
| Tab | Content |
|---|---|
| Rules | The library: id, platform (linux, windows), collection SPL fragment, judgement (equals, contains, threshold), severity, enabled. Import defaults loads a CIS starter pack; a rule can be dry-run to see what it collects |
| Runs | Each run's time, hosts, pass, fail, error and score. Run now runs manually; [baseline] schedule_enabled = 1 runs daily |
| Results | Host and rule judgements with evidence on failures; a score trend line |
Field map
Field map shows which data-model field each rule field resolves to on this instance. Without CIM a built-in minimal table applies.
Limits
| Item | Notes |
|---|---|
tstats | Covers index-time fields and accelerated data models only. Search-time extractions need | stats |
| No CIM Endpoint data | No hosts are enumerated and Run now reports 0. Pass hosts= or onboard endpoint data first |
Asset inventory
Business context for assets and identities. Sources are Enterprise Security's asset and identity lookups or CSV import; investigations, triage and reports pick up owner and criticality automatically.
Data onboarding
Paste raw log lines, detect the format, generate props.conf, transforms.conf, rex and a CIM mapping, dry-run coverage on real data, apply to local/ with rollback. Since 1.7.0.