

RST AI Copilot for Splunk
A security-analysis copilot that installs into Splunk as a native app. Natural-language log queries, alert triage and investigation, detection-rule drafting, and an operations layer for the SOC.
Overview
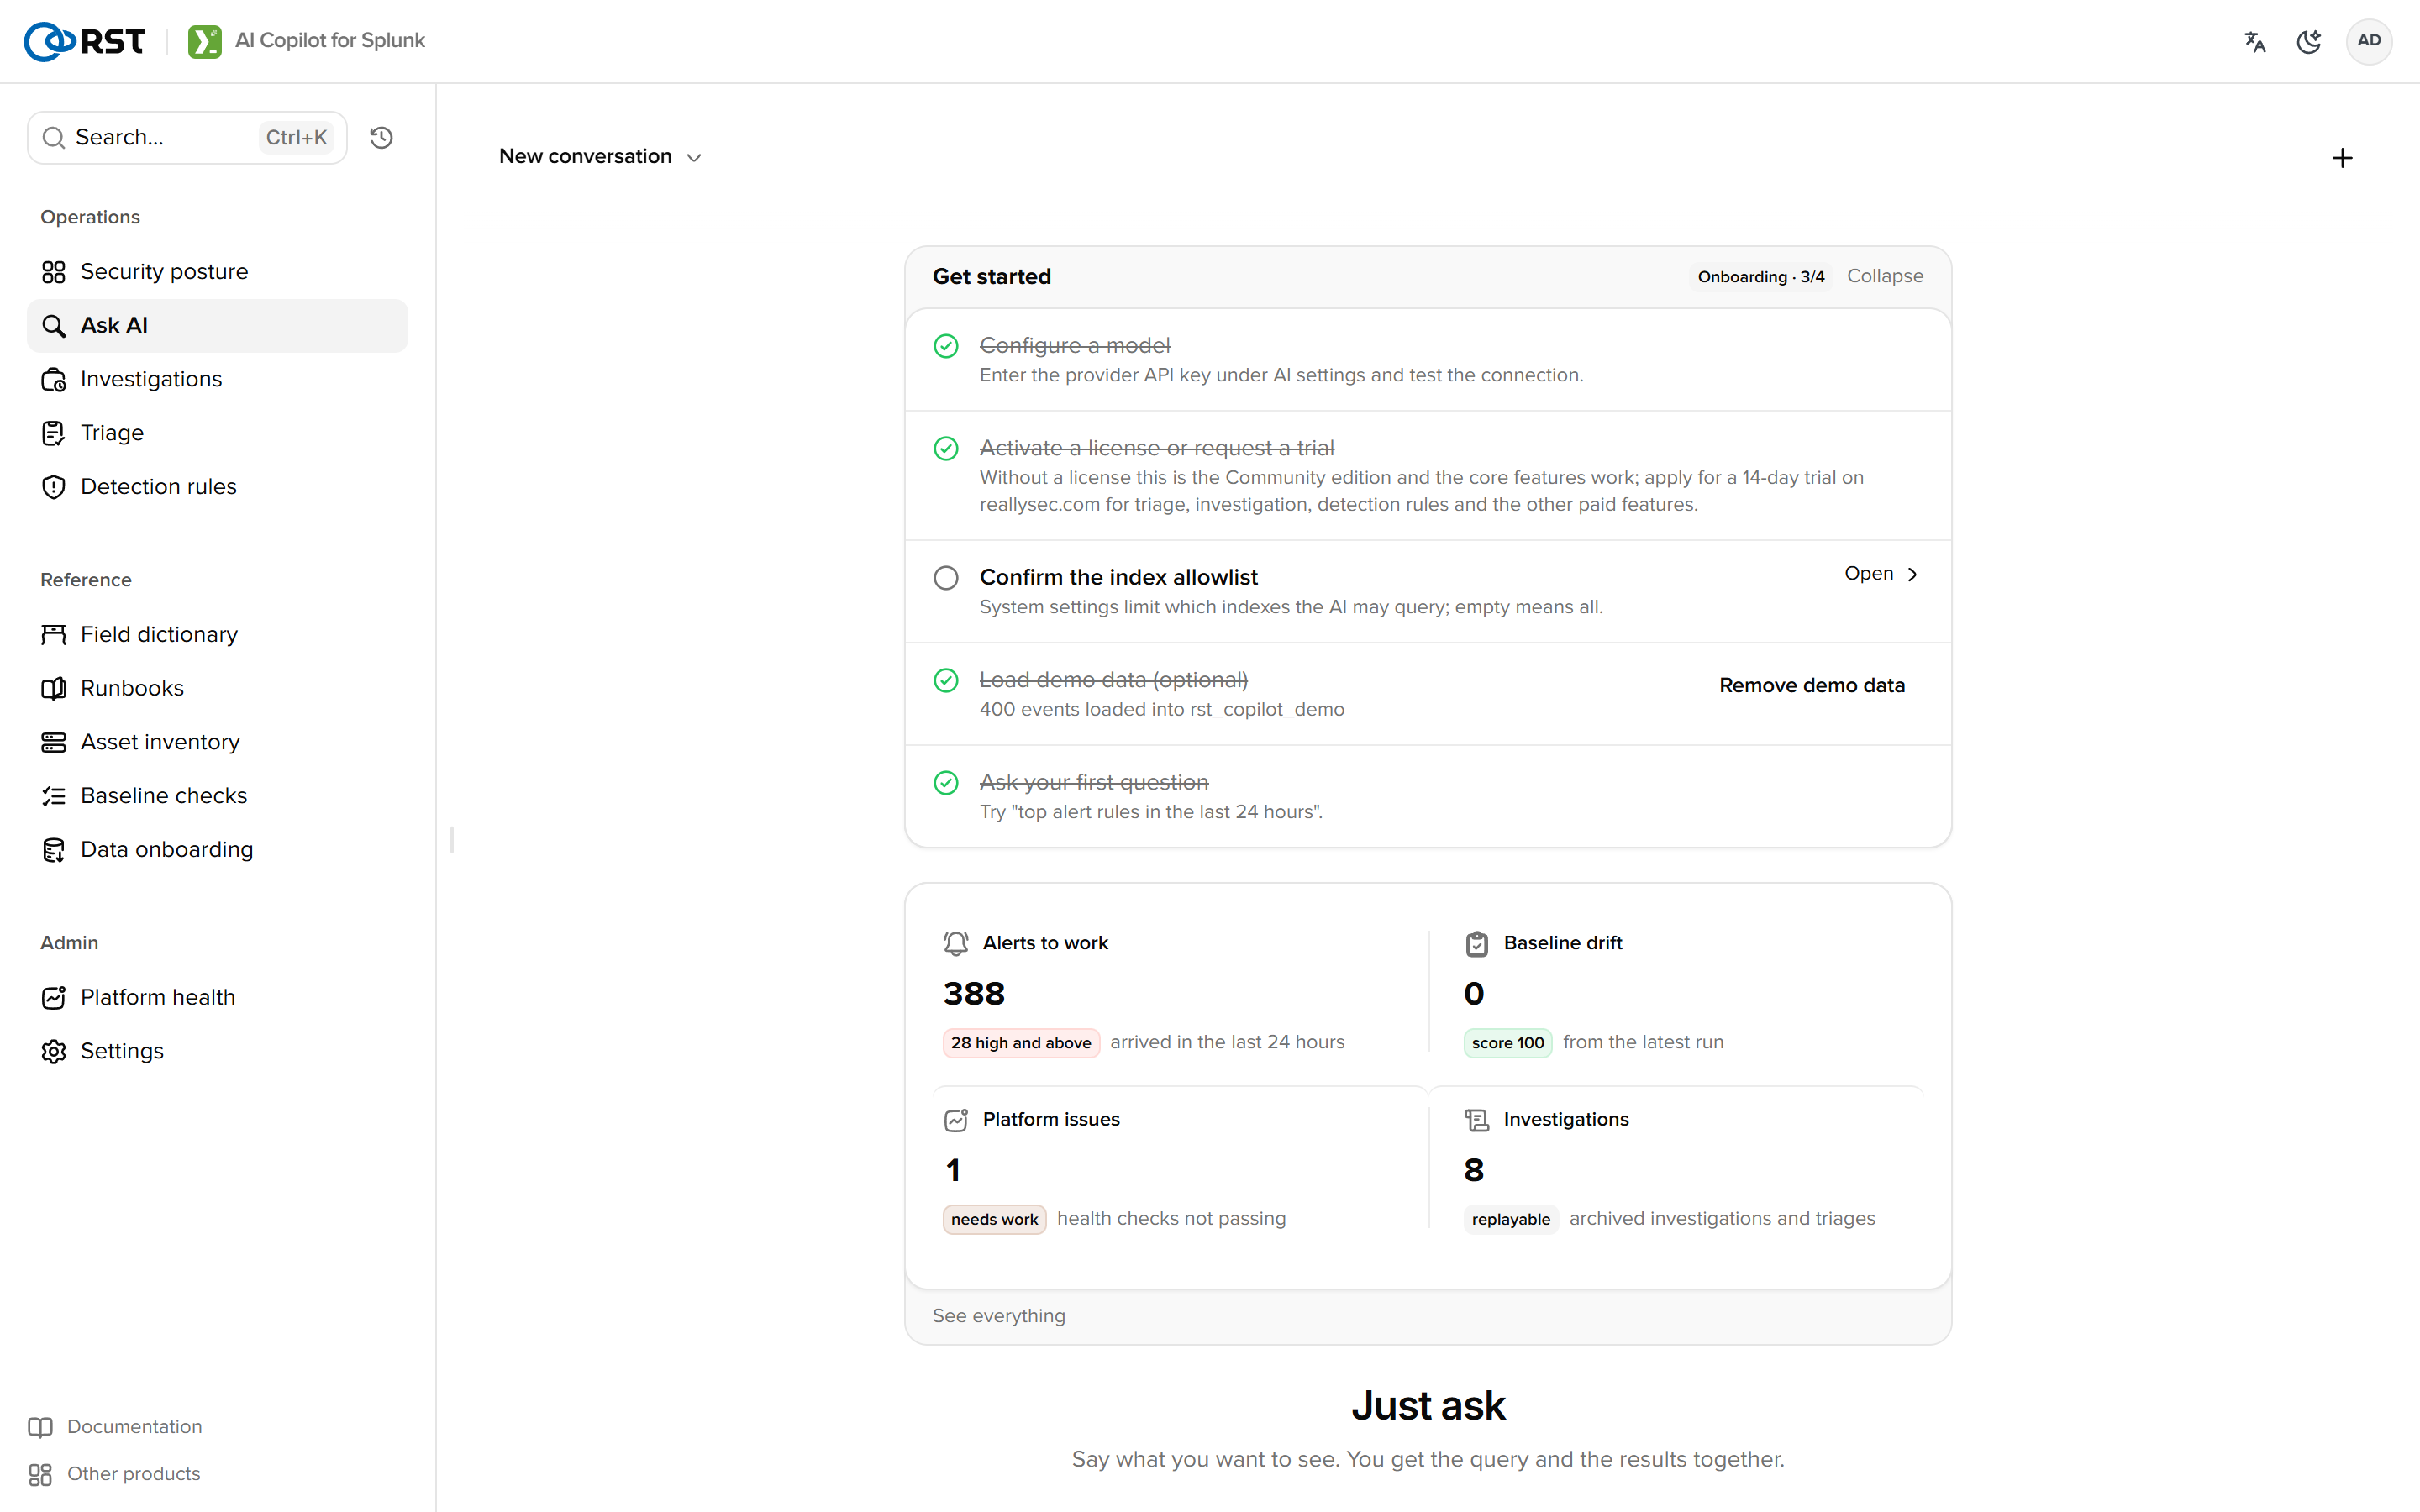
RST AI Copilot for Splunk is a Splunk app (.spl). It installs on the search head and runs there, with no separate service and no extra database. Queries run through Splunk search, state lives in the KV store, and login and roles are Splunk's own. Analysts ask in plain language; the app writes read-only SPL, runs it and explains the result. Given one alert, the app gathers its own evidence, draws the attack chain and gives a verdict, which can be written back to the Enterprise Security notable or opened as a ServiceNow or Jira ticket.
RST AI Copilot for Splunk is the same product line as RST AI Copilot for Elastic: same shell, pages and workflows. Only the query language, data sources and jump targets are Splunk's.
Capabilities
| Capability | Description | Licence |
|---|---|---|
| Smart query | Natural language to read-only SPL, dry-run repair, follow-up turns. A correction made in conversation becomes a knowledge-base rule | Free |
| Search-bar commands | | copilot "question" generates and runs SPL from the Splunk search bar; | splexplain explains and optimises a query | Free |
| Field masking | Cloud, private and air-gapped modes, applied before data leaves the instance | Free |
| Posture, live alerts, reports, audit, runbooks, assets, baseline, data onboarding | Operational data, summarised, archived and governed | Free |
| Batch triage | Cluster, score and rank a batch of alerts, with noise-reduction suggestions | Paid |
| Alert investigation | Autonomous evidence gathering around one alert: timeline, attack chain, blast radius, false-positive verdict; write back to ES or open a ticket | Paid |
| Detection-rule drafting | Description to a deployable scheduled saved search (SPL, schedule, trigger, MITRE), one-click deploy; ATT&CK coverage heatmap | Paid (sealed delivery) |
| Platform-health interpretation | Root cause and read-only SPL for the Splunk check-up findings | Paid |
Paid capabilities need an activated licence; the enterprise tier includes everything. A 14-day trial is requested on the reallysec.com trial page: confirm the email, copy the licence key from the console and paste it into the Online tab of the License page. The detection engine ships as ciphertext; its key comes with the licence, so an unlicensed instance cannot run it.
Documentation
Quick start
From the .spl to a first answered question, about ten minutes.
Installation
Version requirements, the two packages, configuration, roles and permissions, upgrade and backup.
User guide
What each page is for and where it stops: query, triage, investigation, rules, posture, onboarding, settings.
Troubleshooting
Causes by symptom; error-code lookup.