

Offenses
Sync offenses from QRadar with an AI summary for each. Filter and act on them in the alert feed, write notes, closes and assignments back to QRadar, and investigate a single offense.
Offenses is a tab of the Security posture page. QRadar rules create the offenses; the gateway syncs them on a schedule, writes a one-line AI summary for each new offense and pushes it live into the alert feed. Dispositions are stored in the gateway and shared by the team. Notes, closes and assignments are written back to QRadar. Sync and dispositions are available in every edition; investigation needs a paid license.
The gateway fetches new offenses by start_time and refreshes stored ones by last_updated_time, so closes, assignments and growing event counts in the Console come back too. The first sync looks back over RST_OFFENSE_INGEST_LOOKBACK (7 days by default) for OPEN offenses. Severity is derived from QRadar's magnitude. AI summaries follow the interface language, and background syncs use RST_OUTPUT_LANG.
The token's security profile decides which offenses the gateway can see. If the list stays empty, check QRadar token permissions first, then confirm that OPEN offenses exist within the lookback period.
Configure the sync
Prerequisites
- Administrator role.
- QRadar is connected in Settings.
Steps
- Under Sync settings on the page, turn on Polling on.
- Enter the Poll interval (seconds); the default is 30.
- (Optional) Enter a Minimum magnitude. Offenses below it are neither stored nor pushed; 0 means all.
- Select Sync now to run one sync cycle.
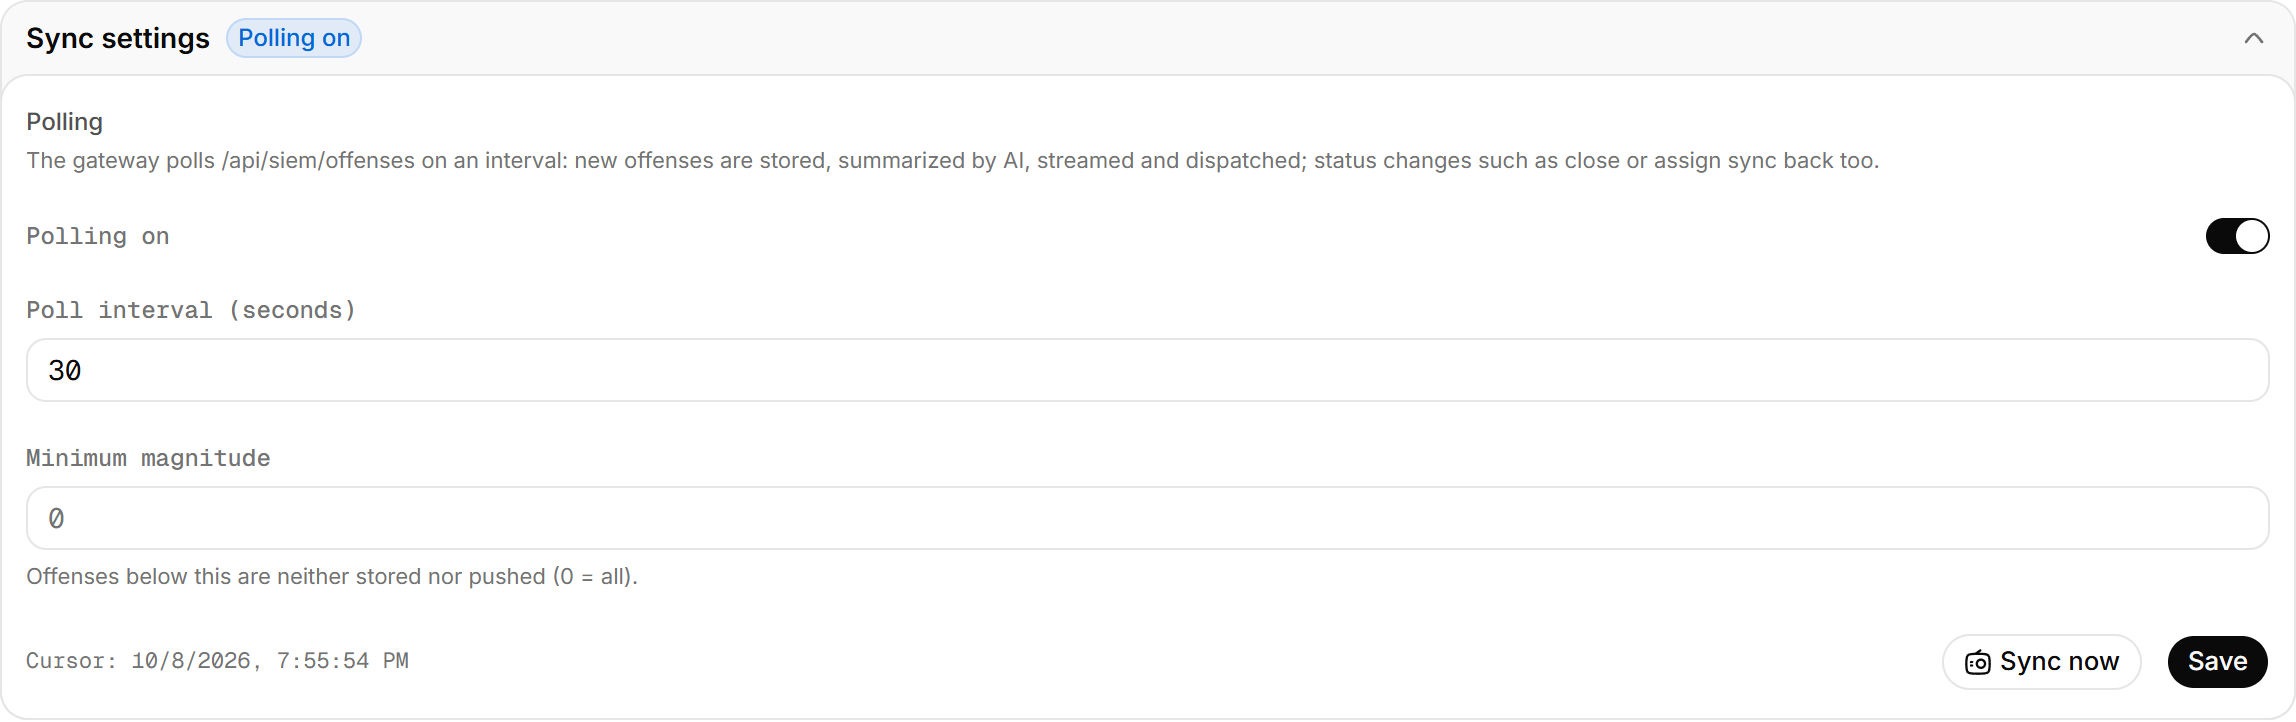
When the sync finishes, a message gives the number of new offenses, and Cursor shows how far the last sync reached. Offenses whose summary ran past the time budget show not generated (past the summary time budget).
View the alert overview
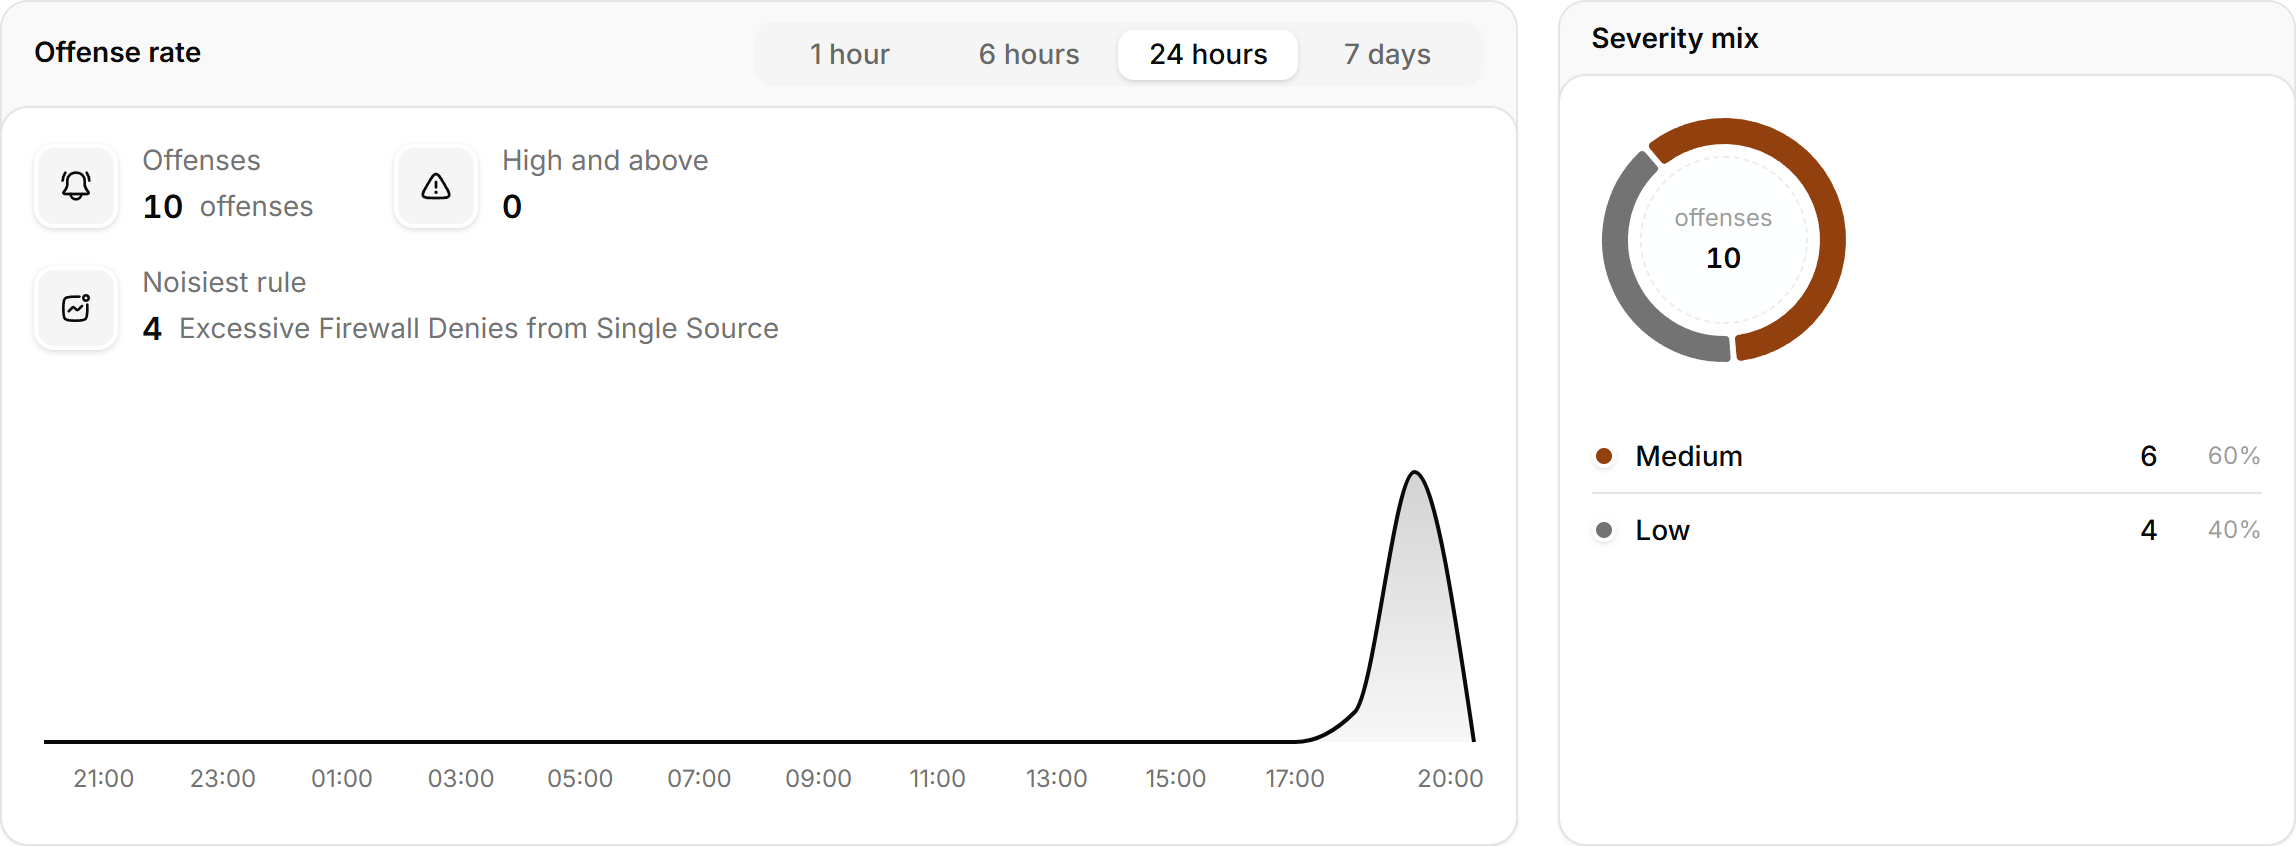
Alert overview shows the alerts, critical and high alerts, and handled and false-positive alerts in the selected window, with the Alert rate chart and the Severity mix. The window can be 1 hour, 6 hours, 24 hours or 7 days.
Act on offenses in the alert feed
Steps
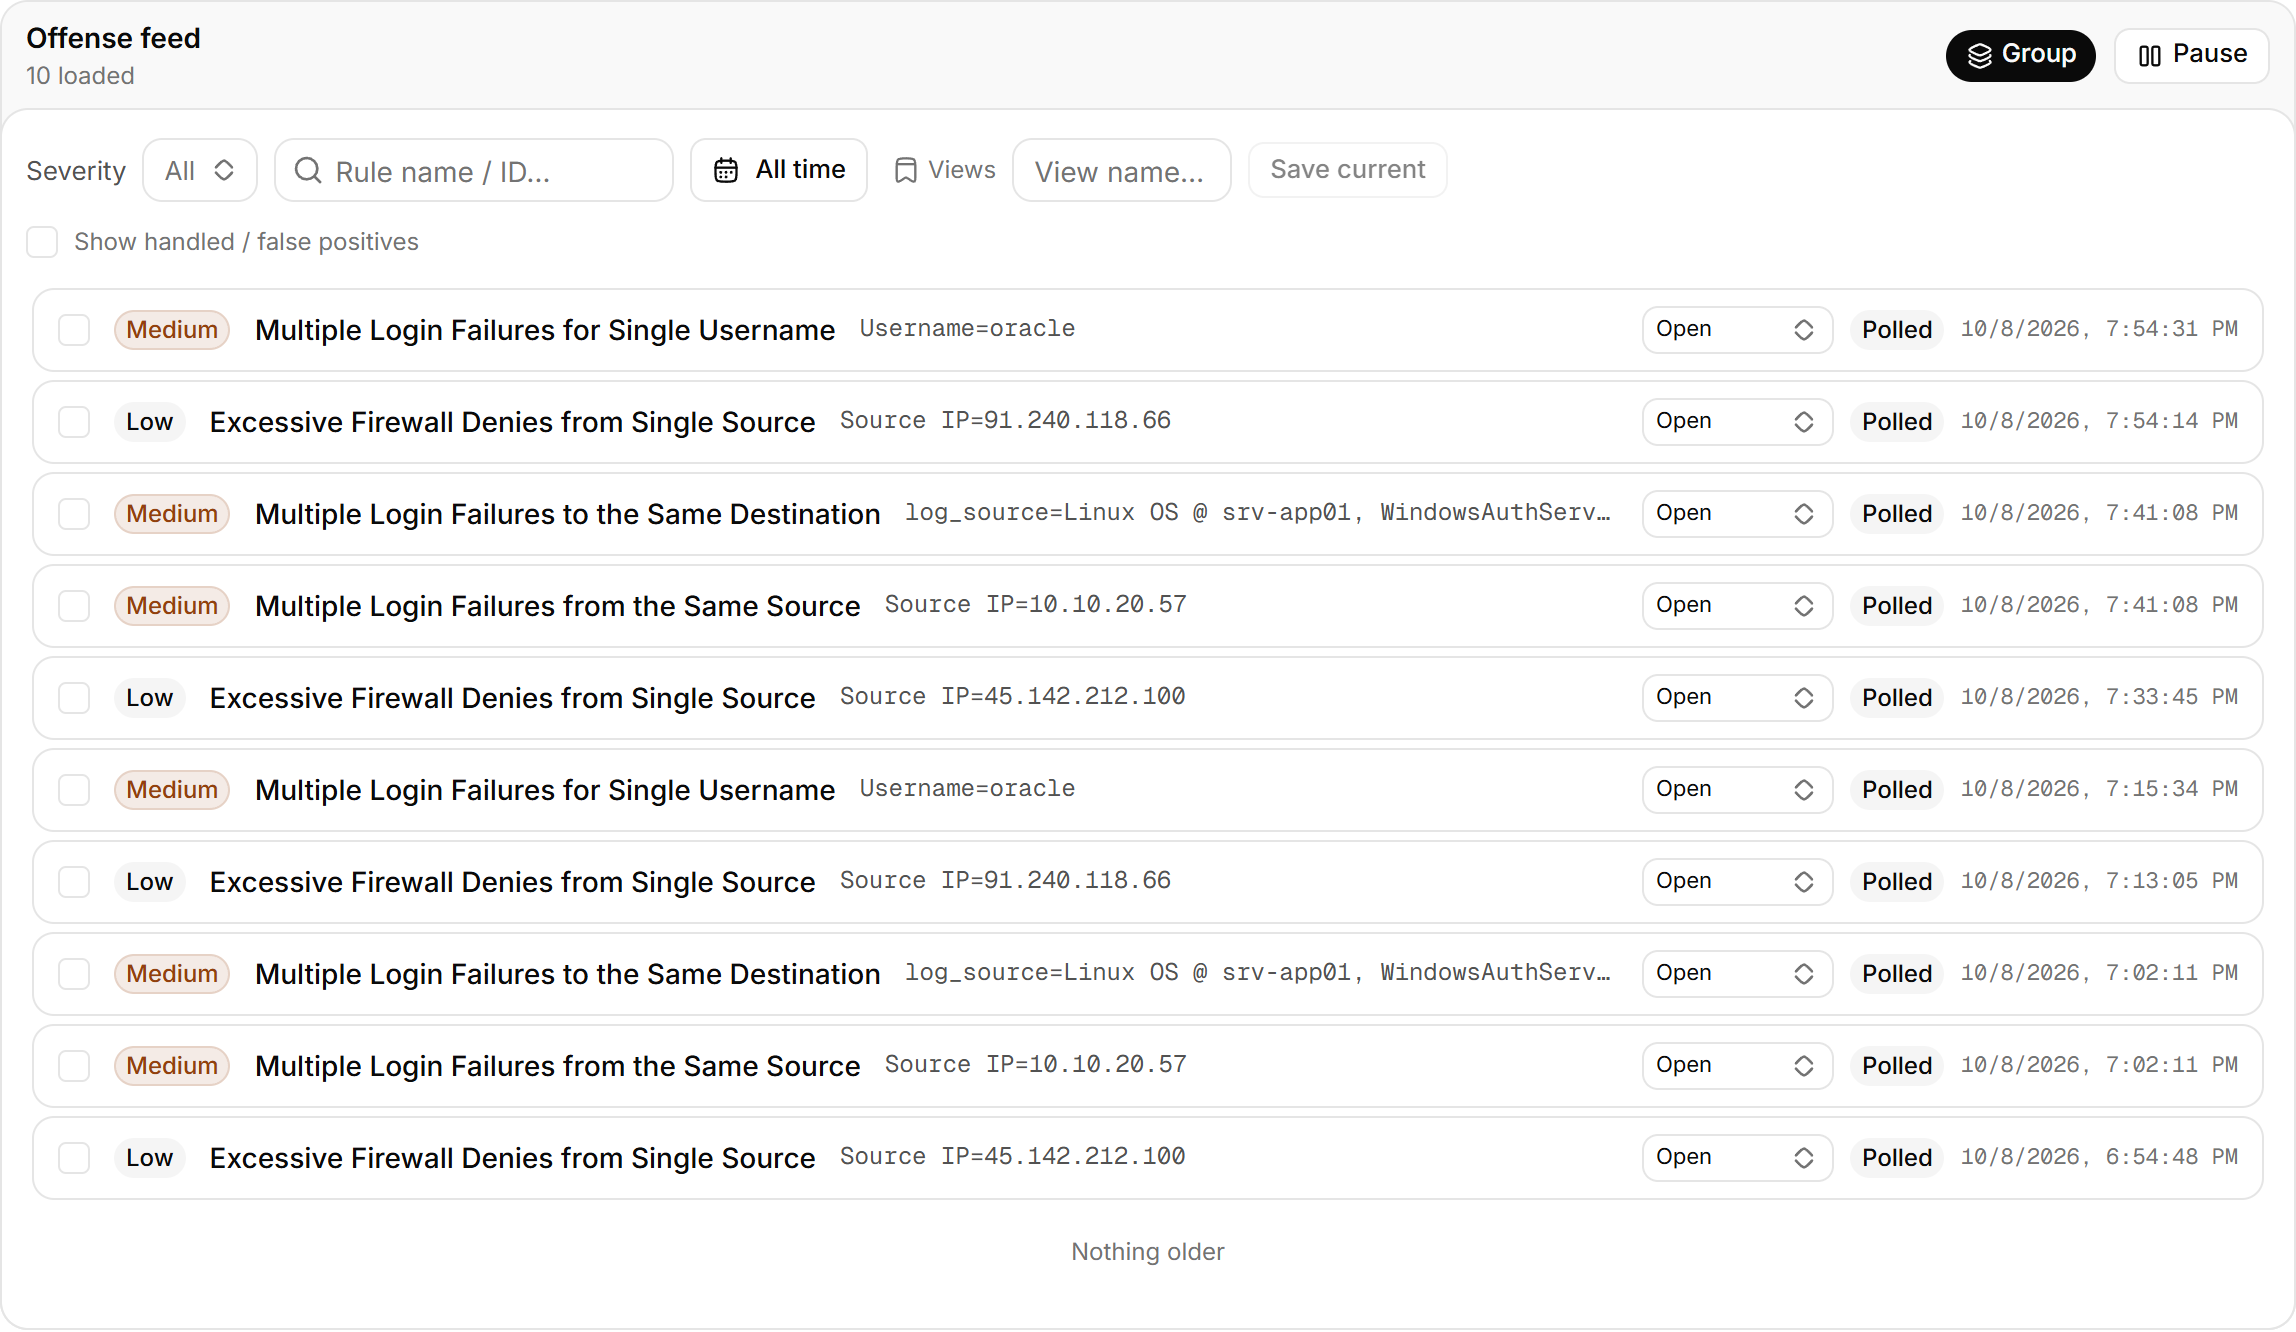
- (Optional) Filter by Severity or Rule name / ID…. To keep a filter combination, select Save current under Views.
- Select the check boxes of one or more offenses.
- Select Mark handled or Mark false positive.
A message offers Undo. Handled and false-positive offenses are hidden until you turn on Show handled / false positives. Dispositions stay in the gateway and are not written back to QRadar.
New offenses appear live at the top of the feed. Updates pause while you scroll down and resume at the top. With Group on, offenses with the same rule and source collapse into one row.
Write back to QRadar
Prerequisites
- Analyst or administrator role.
- The token's user role has the close, assign and note permissions for Offenses.
Steps
- Select an offense to open its details.
- Under Write back to QRadar, do one of the following:
- Enter a note and select Add note.
- Select a Closing reason…, optionally add a note, and select Close offense.
- Enter a QRadar username and select Assign.
- Select Flag for follow-up or Clear follow-up.
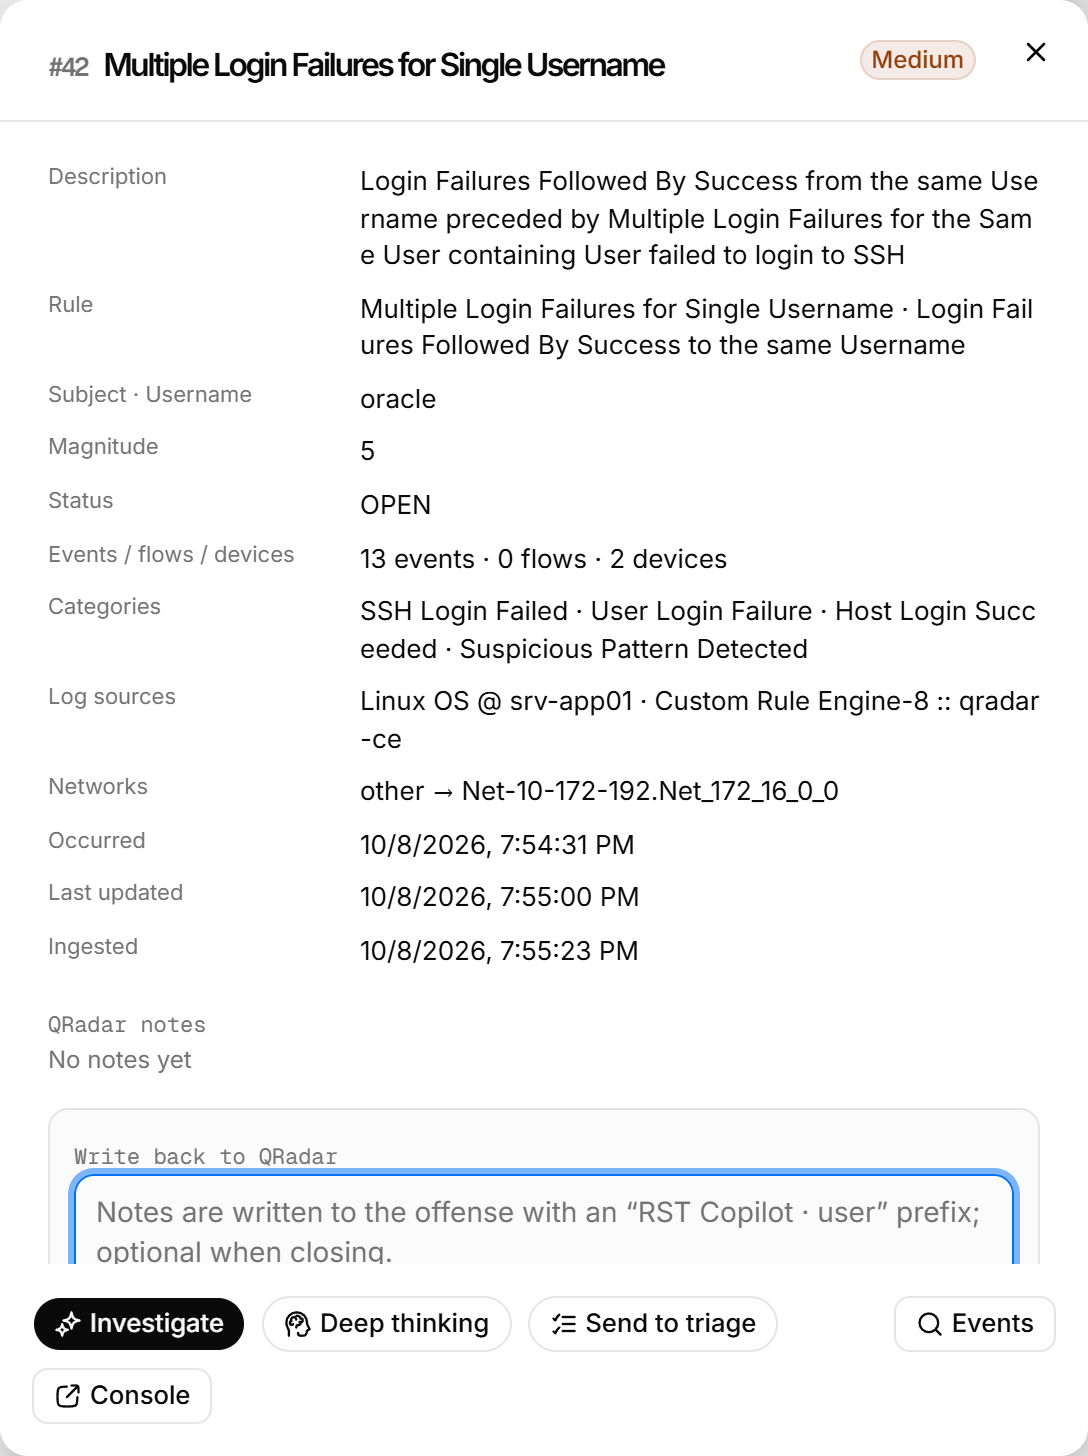
Notes are written to the offense with an "RST Copilot · user" prefix, and the closing reasons come from QRadar. In QRadar these actions are recorded under the gateway's authorized service; the Audit log records who did it.
Other actions in the details: Events queries the events behind the offense with INOFFENSE() in Ask AI, and Send to triage hands the offense to Triage.
Investigate an offense
The gateway first pulls the events behind the offense with INOFFENSE(), then runs AQL over several rounds around its subjects (source IP, destination host, account), and finally gives a verdict. Every AQL step passes the read-only check and the log-source whitelist. One investigation has a total time budget of RST_AGENTIC_DEADLINE_S (180 seconds by default). If the model does not support function calling, the investigation runs as a single step.
Prerequisites
- A Professional or Enterprise license, including a trial.
Steps
- Select an offense to open its details.
- Select Investigate.
When it finishes, the report opens and is archived in Investigations. The header shows severity, Confidence, whether it is a Likely false positive, the number of Agentic rounds and how many context records were pulled.
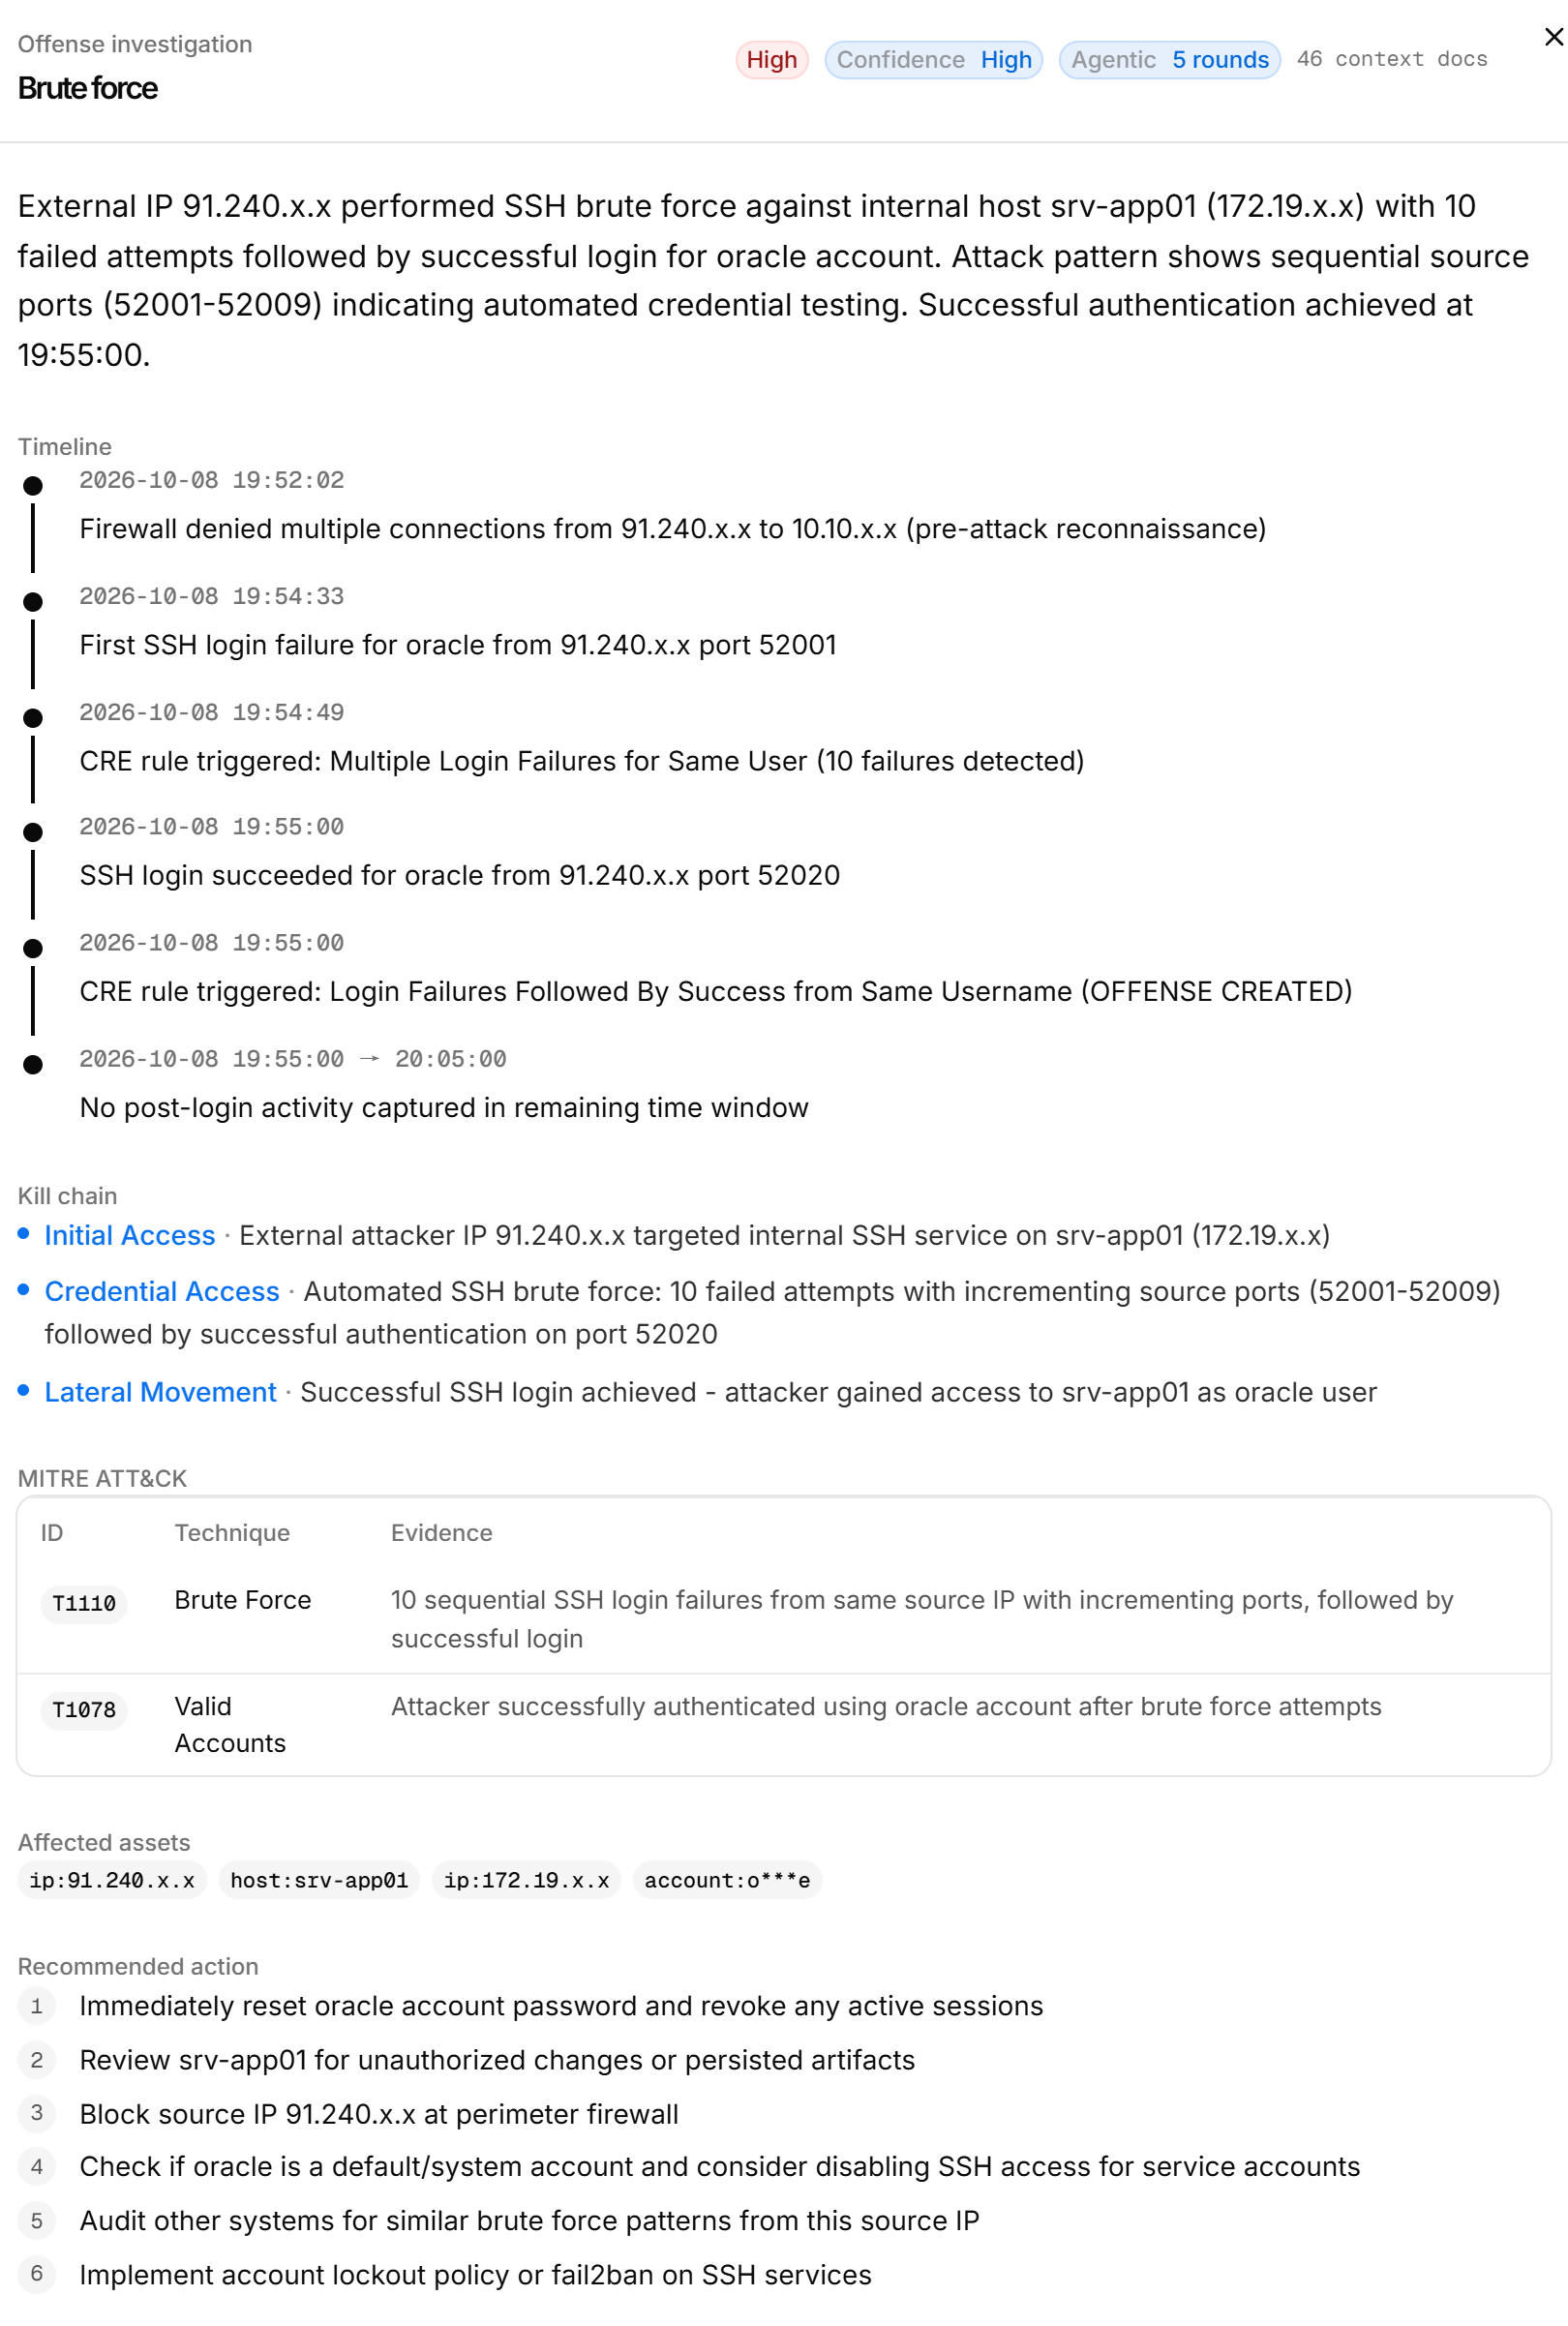
IP addresses shown as 10.30.x.x were replaced by the cloud masking mode before they reached the model. Private and air-gapped modes show the original values.
At the bottom of the report you can change the Disposition, select Make a detection rule to hand it to the Rule copilot, select Push the conclusion to send it to the destinations in Outbound channels whose alert threshold the severity meets, or select Export the incident report (Markdown).
Investigation report contents
| Section | Content |
|---|---|
| Verdict | What happened and whether it needs action |
| False-positive assessment | Why it is or is not a false positive |
| Timeline | Related events in time order |
| Kill chain | Key steps grouped by tactic |
| MITRE ATT&CK | Technique IDs, technique names and evidence |
| Affected assets | Hosts, IPs and accounts involved |
| Recommended action | Numbered response steps |
| Retrieval trace (agentic) | The AQL run at each step, hits and call arguments. Failed steps, such as a log source outside the whitelist, are listed too |
Push alerts
New offenses above a threshold are pushed to Feishu, DingTalk, WeCom, Teams, Slack or email. Set the threshold and destinations in Outbound channels.
Investigations
Automatic archive of offense investigations, batch triage runs and query result readouts, kept per account, with follow-up queries on a record's subject.
Triage
Clusters a batch of offenses by rule and source; the model rates each cluster, judges false positives and recommends an action, and the clusters are queued by priority. A paid feature.