

Services
How service principals are named, when one is needed, how certificates and keytabs reach it, and what the PAC type and pre-authentication options mean.
This page covers the Services page under Identity. A service principal is the Kerberos identity of a service on a host, such as HTTP/web01.linux.ipa.test@LINUX.IPA.TEST. Only services that authenticate clients with Kerberos or need a certificate from the IPA CA need one: HTTP (SSO, SPNEGO), nfs, cifs, ldap, postgres. Plain ssh logins do not; the host/ principal covers them.
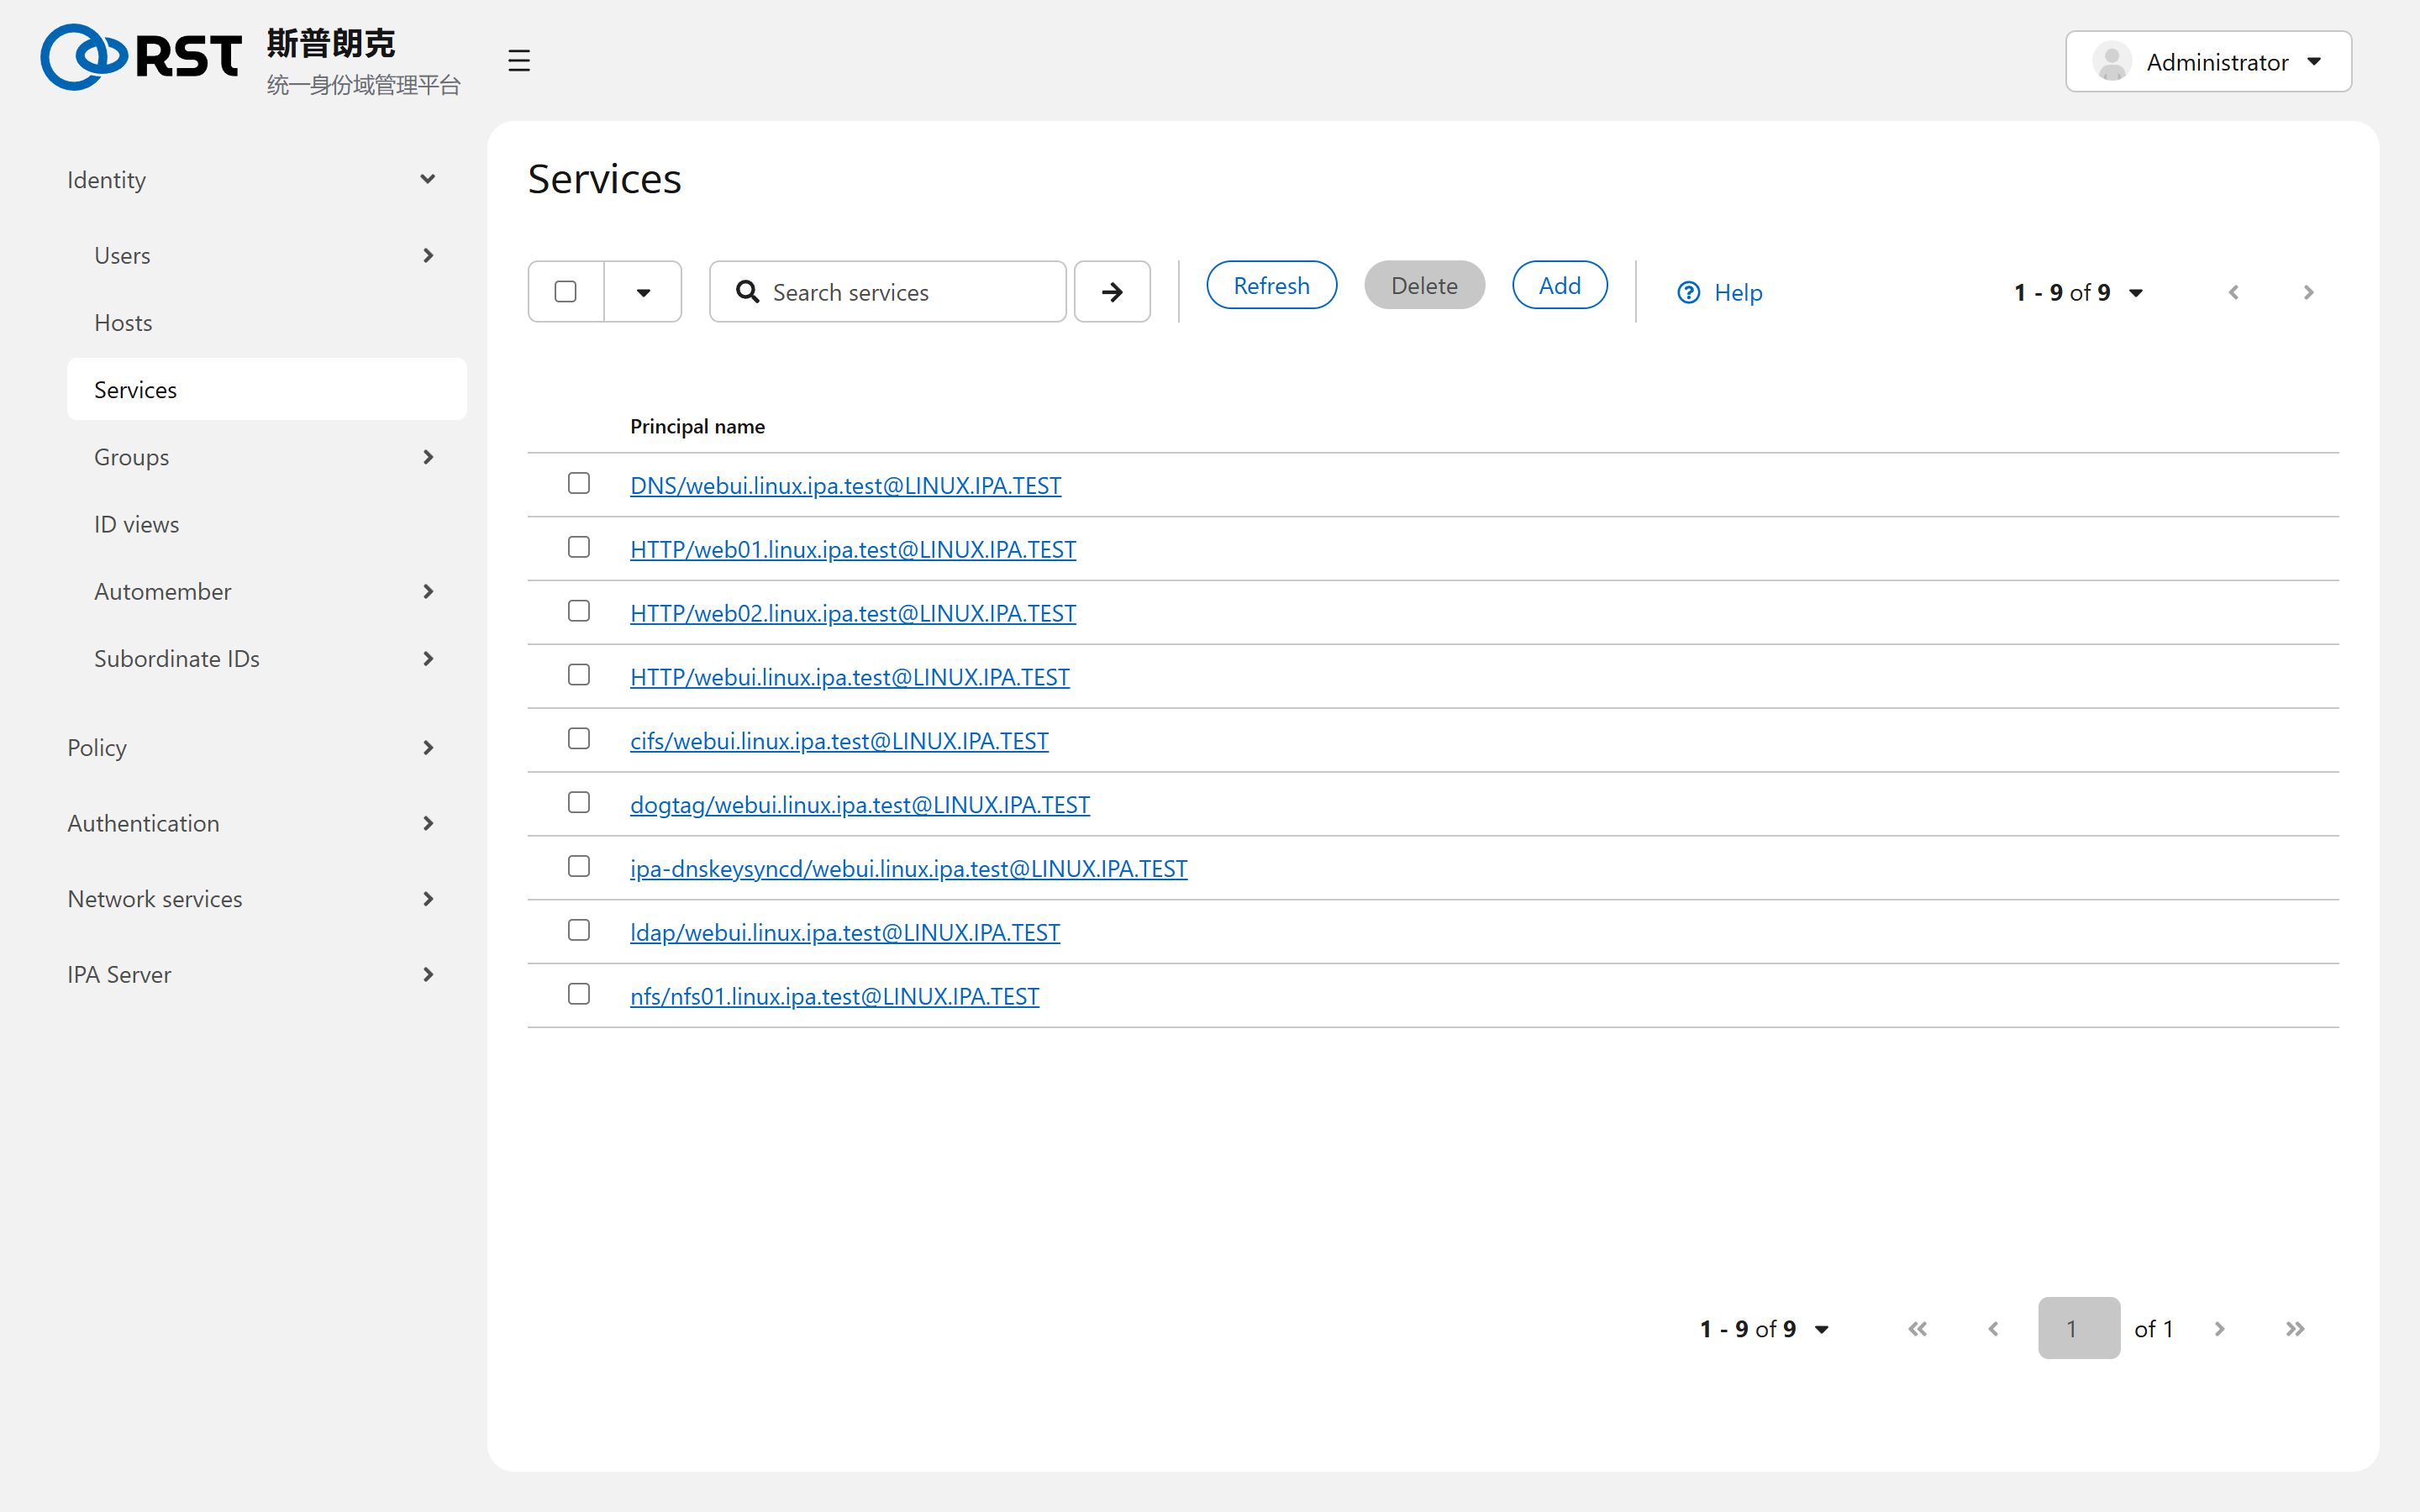
The IPA server's own DNS/, HTTP/, ldap/, cifs/, dogtag/ and ipa-dnskeysyncd/ principals are created by the installer. Do not delete them.
Adding
A service is a service name plus a host. The host must already be a host object. The service name is case-sensitive and must match what the client software expects (HTTP for Apache mod_auth_gssapi, nfs for nfs-utils). Then fetch the keytab on the host:
ipa-getkeytab -p HTTP/web01.linux.ipa.test -k /etc/httpd/http.keytabAlternatively, grant the host the right to fetch it itself with ipa service-add-host.
Detail page
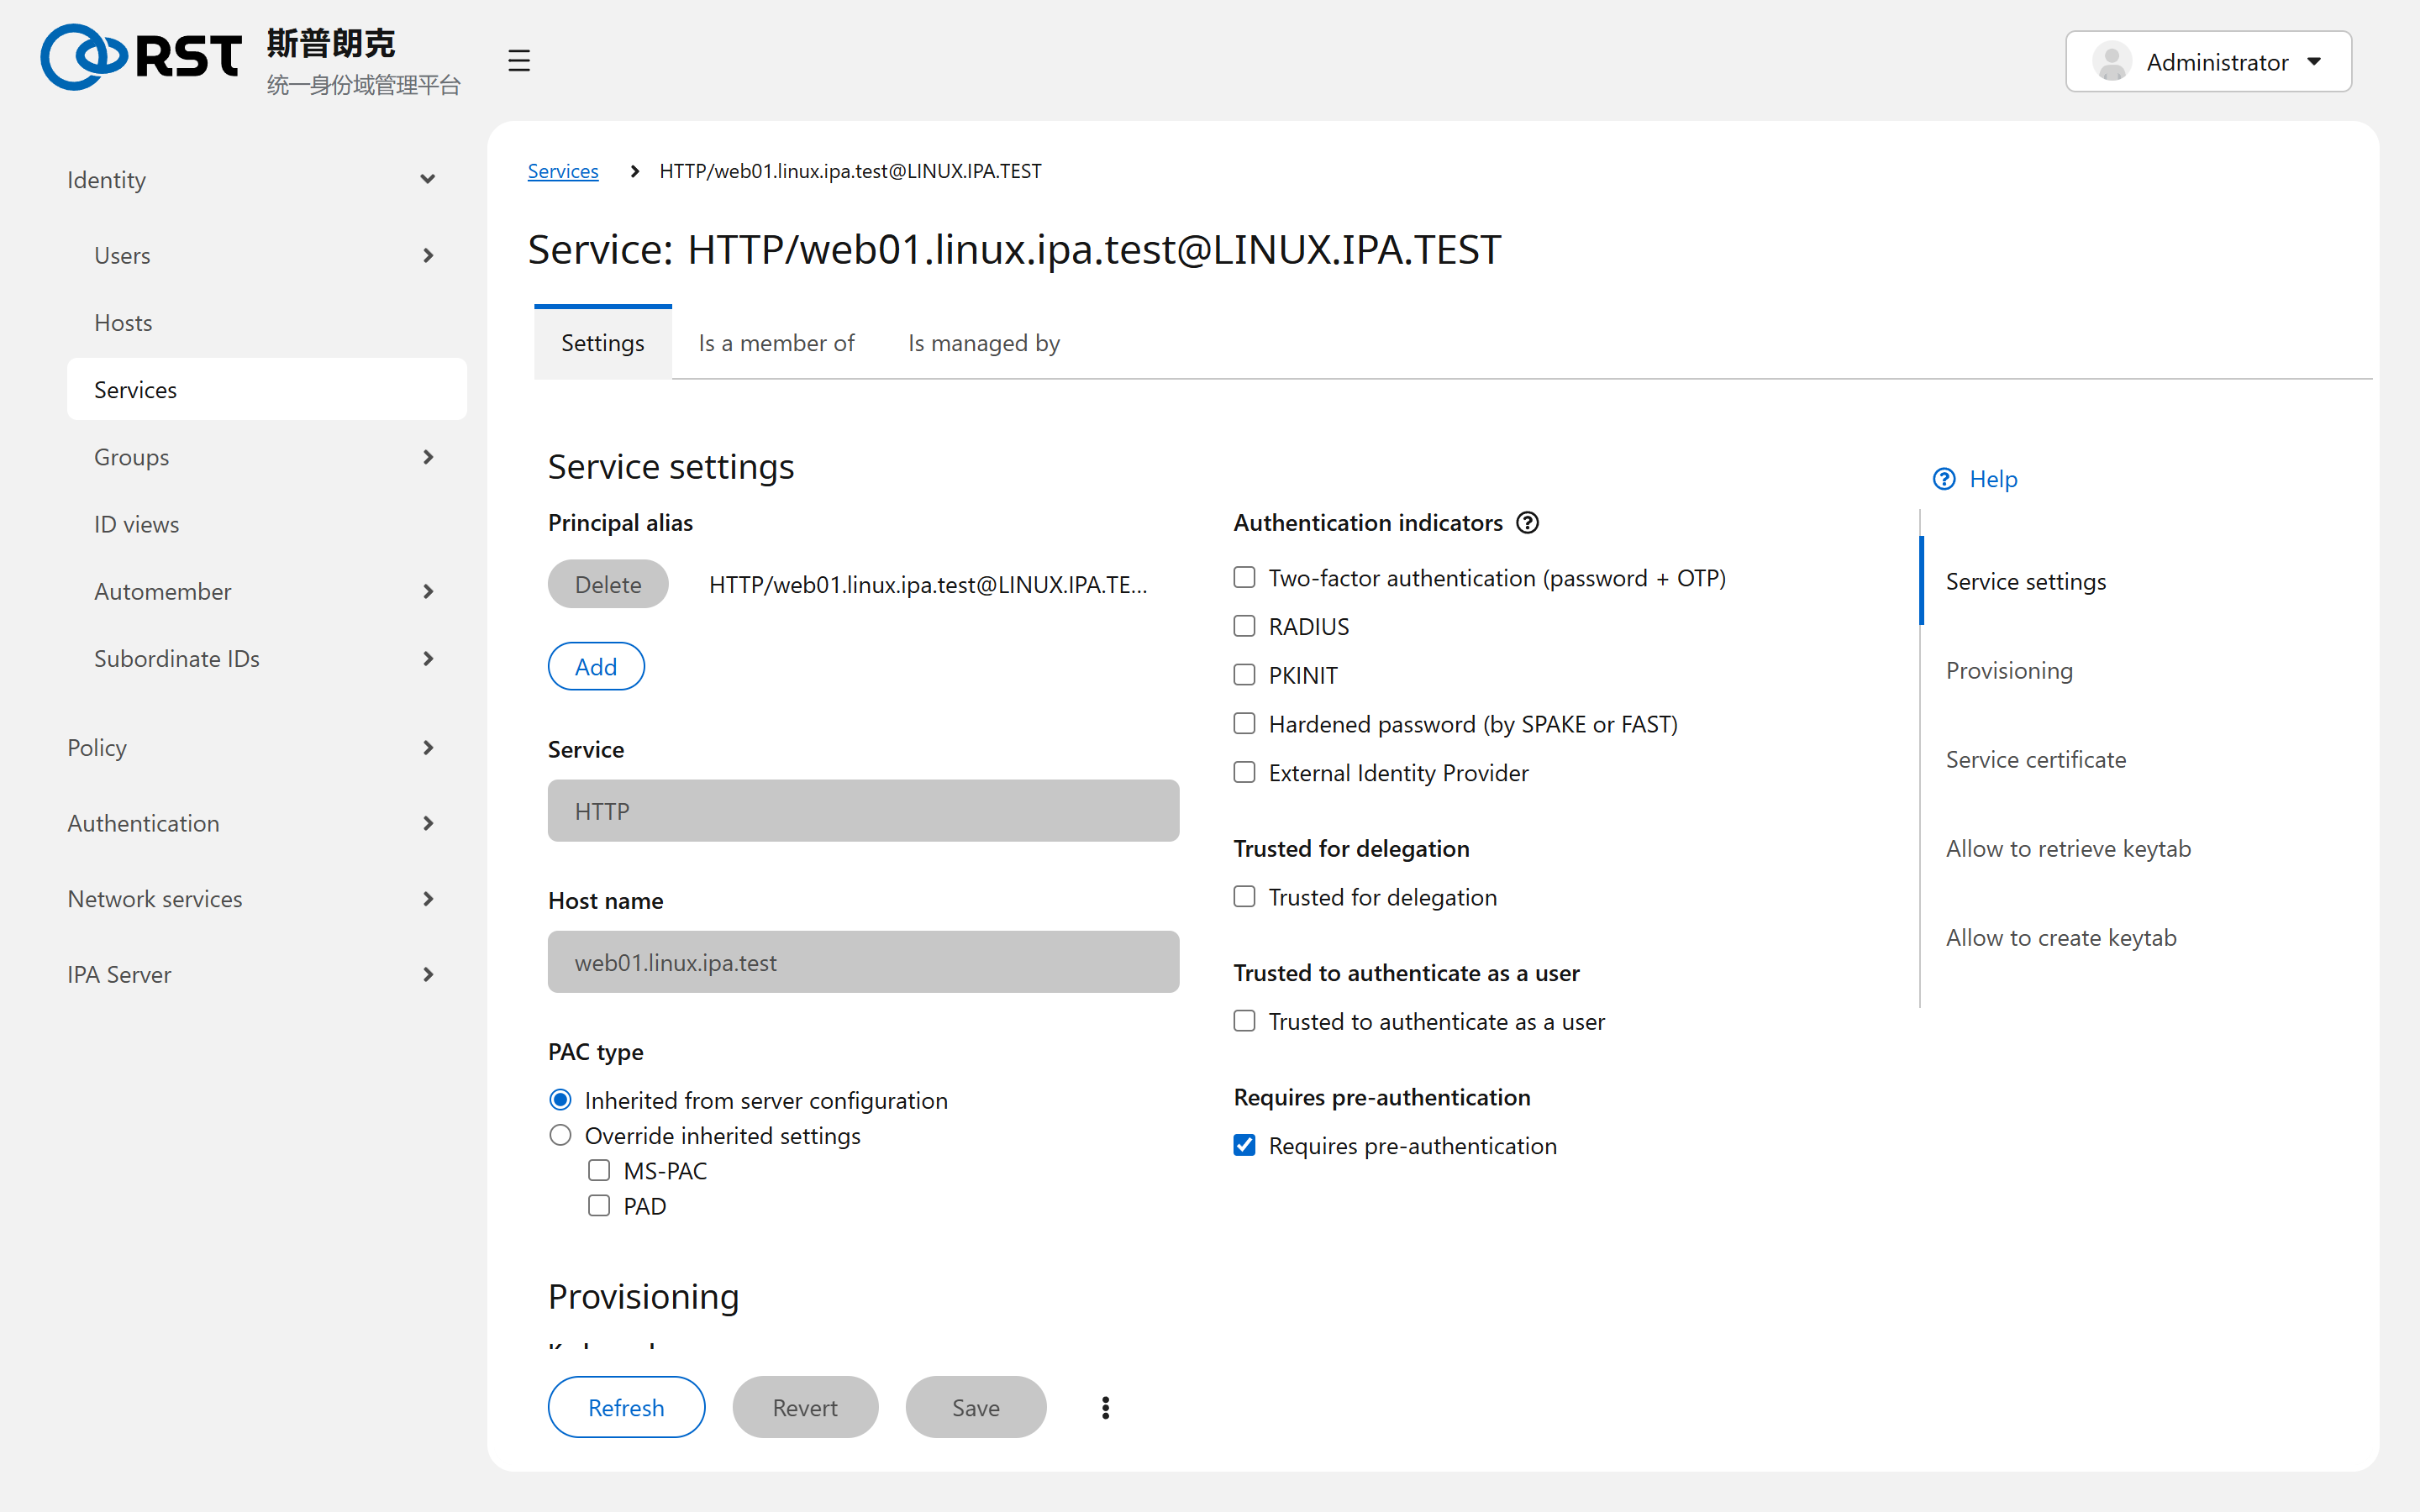
| Block | Meaning |
|---|---|
| Principal alias | Other names for the same service, such as a load-balancer VIP. The ticket must match the name the client connects to |
| PAC type | Whether tickets carry an MS-PAC or PAD. Inherited from server configuration is the default; only Samba-style services need MS-PAC |
| Authentication indicators | As on the host page: require tickets for this service to have been obtained by a specific method |
| Trusted for delegation, Trusted to authenticate as user | Let this service act on the user's behalf towards other services (S4U2Proxy). Reverse proxies and gateways only |
| Requires pre-authentication | On by default. Off lets anyone request a TGS for this service; only for rare legacy clients |
| Service certificate | Certificate from the IPA CA; issue, revoke and renew here |
| Allow to retrieve keytab, Allow to create keytab | Principals allowed to fetch or regenerate this service's keytab |
Is a member of lists roles. Is managed by lists the hosts that may obtain certificates and keytabs on its behalf.
Boundaries
| Topic | Notes |
|---|---|
| Host deletion | Service principals are deleted with their host |
| Keytab files | The UI never hands out keytab files. A keytab is generated on the target host with ipa-getkeytab; regenerating one invalidates the old one at once |
| Certificate profile | Chosen on the CLI with ipa cert-request --profile-id=; the UI uses the default profile |