

DNS
Requires the dns module. IPA's own DNS with zones, records, forward zones and forward policy, per-server forwarders and global config; how host records are maintained automatically, and why this group does not apply with IPA_SETUP_DNS=false.
This page covers the DNS pages under Network services. It requires the dns module and IPA_SETUP_DNS=true at install time (see Configuration). IPA's bundled BIND reads zone data from LDAP; these pages edit the LDAP records and BIND follows without a reload. On a deployment without DNS the pages address no service: the navigation still shows them and changes do nothing.
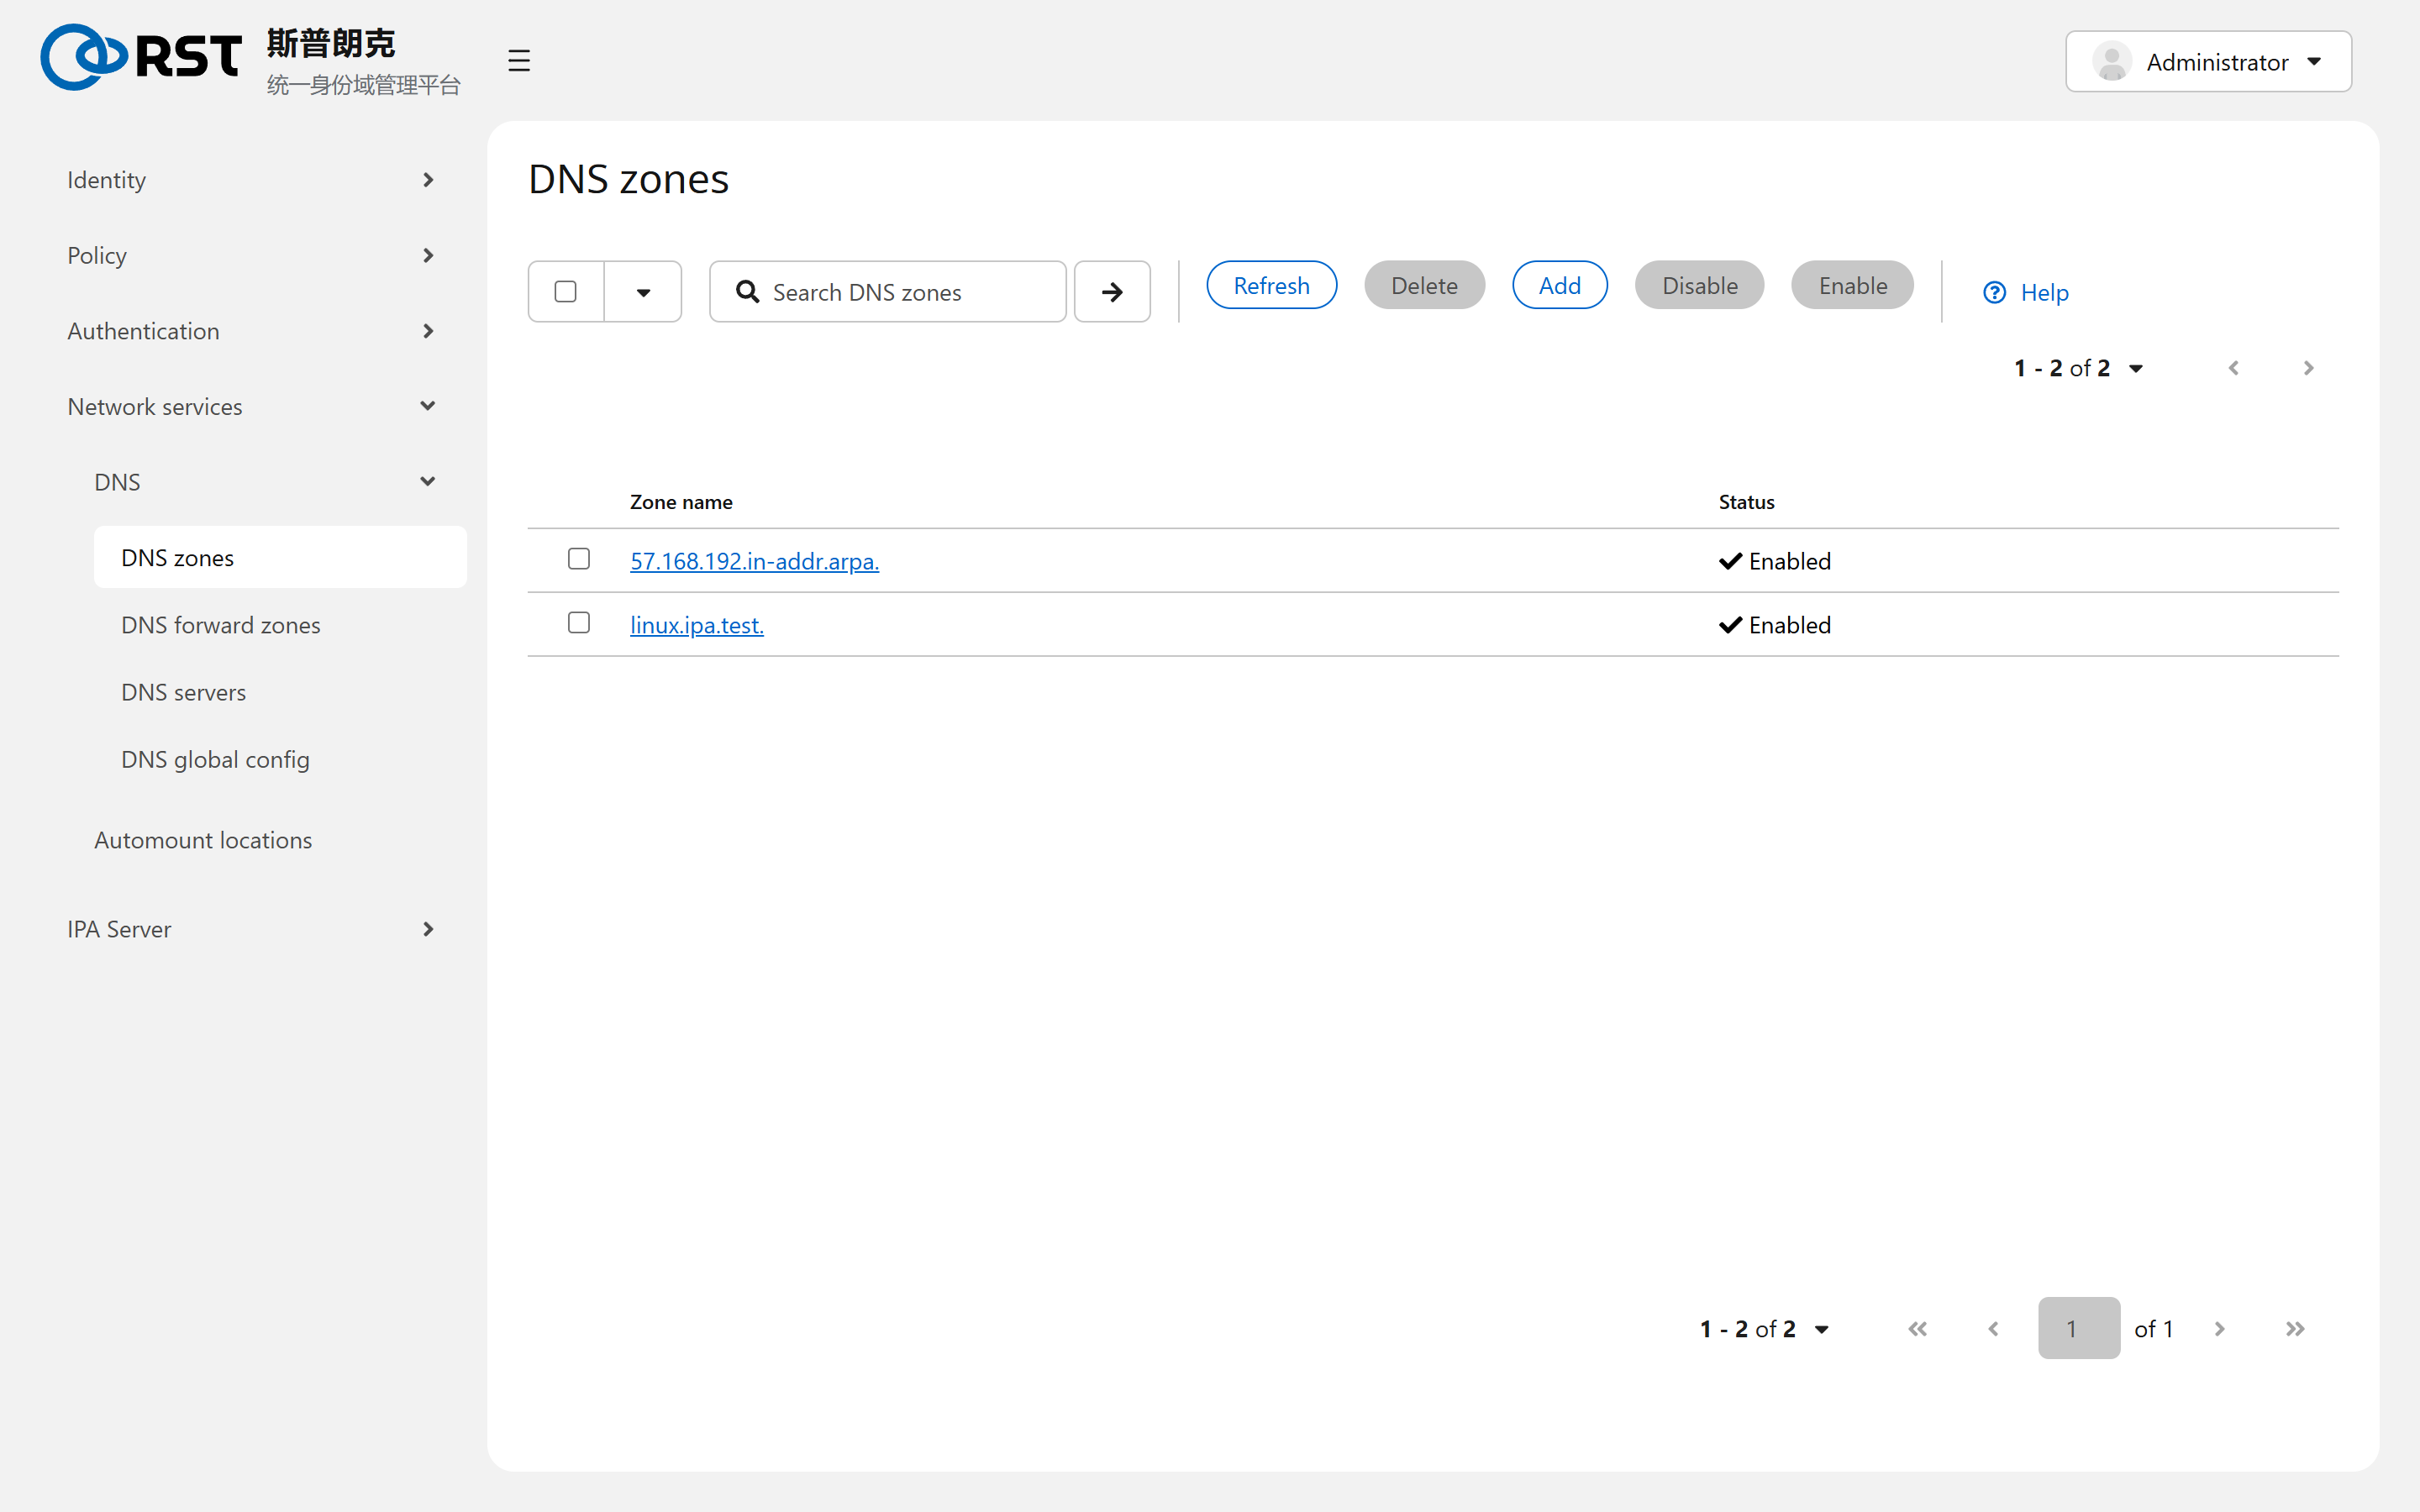
Zones
The installer creates the forward zone (the domain itself, such as linux.ipa.test.); a reverse zone is optional at install time. Zone names carry the trailing dot.
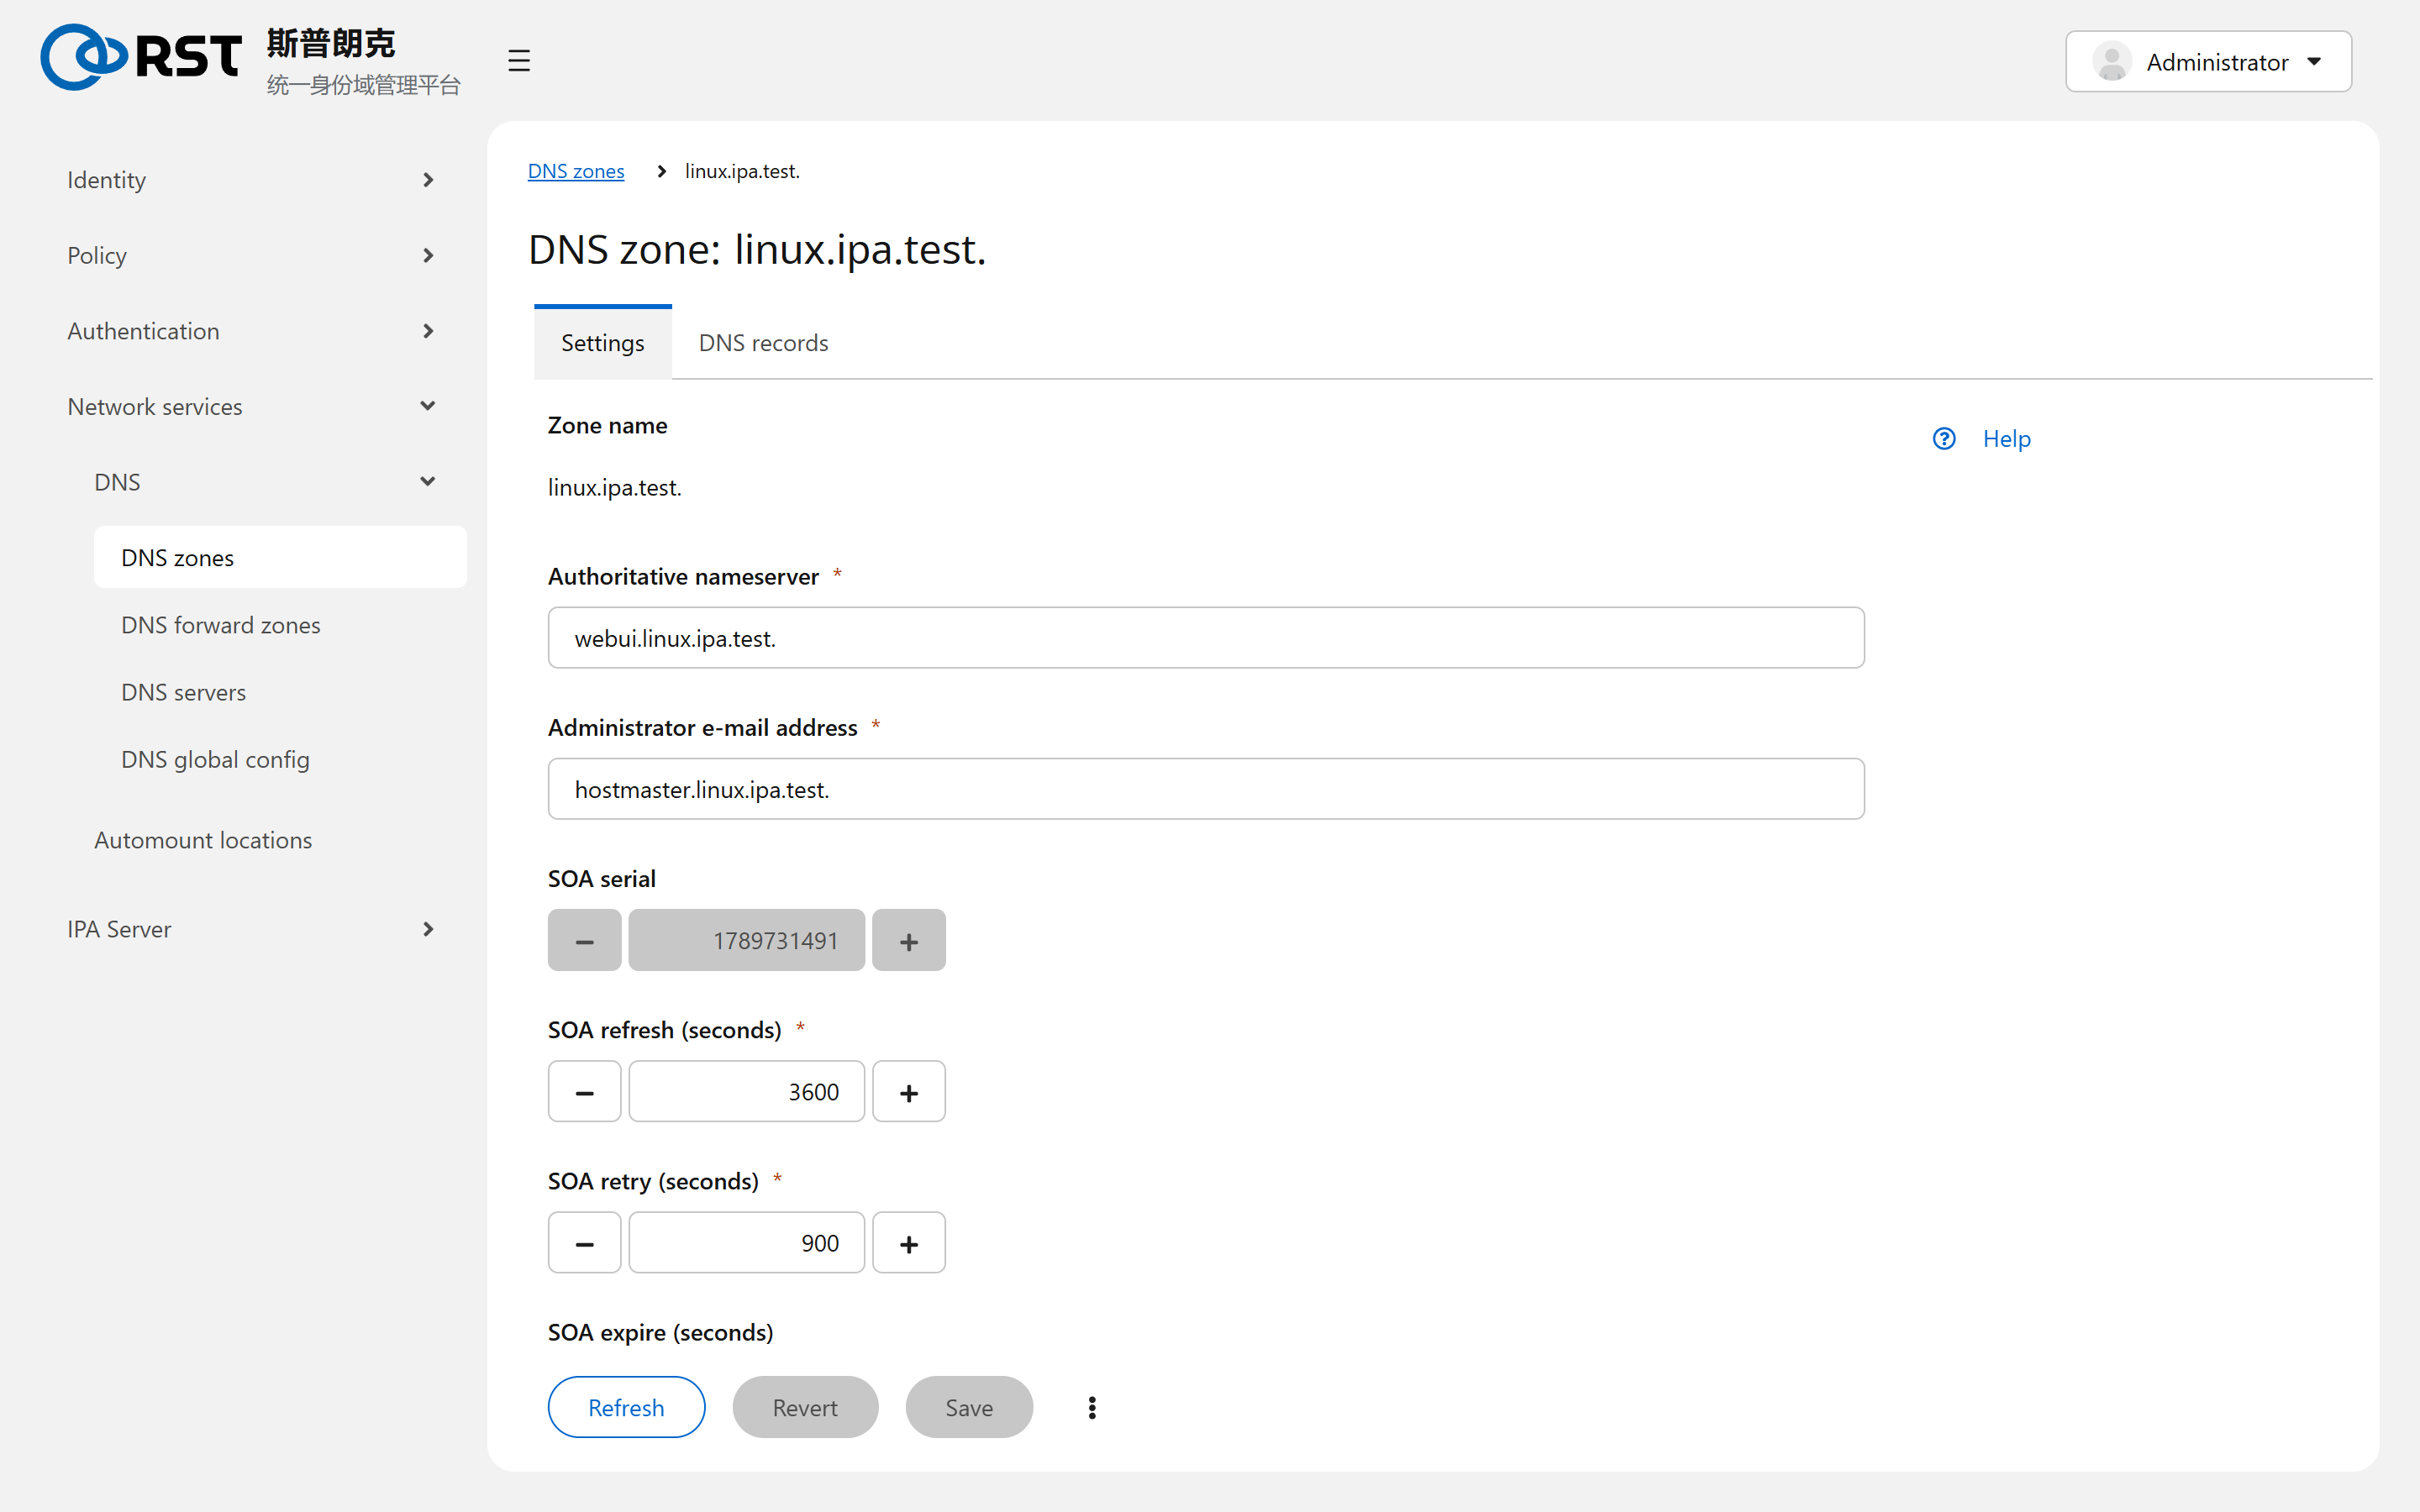
| Field | Meaning |
|---|---|
| Authoritative nameserver, Administrator e-mail | SOA MNAME and RNAME |
| SOA serial | Bumped automatically on every record change |
| SOA refresh, retry, expire, minimum | Timers for secondaries, if any. IPA replicas share data through LDAP replication, not AXFR |
| Dynamic update, BIND update policy | Let clients update their own records with GSS-TSIG. ipa-client-install enables nsupdate and relies on the policy grant LINUX.IPA.TEST krb5-self * A; ... |
| Allow query, Allow transfer | ACLs. Transfer defaults to none |
| Allow PTR sync | Changing an A record also changes the PTR, provided the reverse zone is in IPA |
| DNSSEC | Sign the zone. Enable the key master on the DNS servers page first |
Records
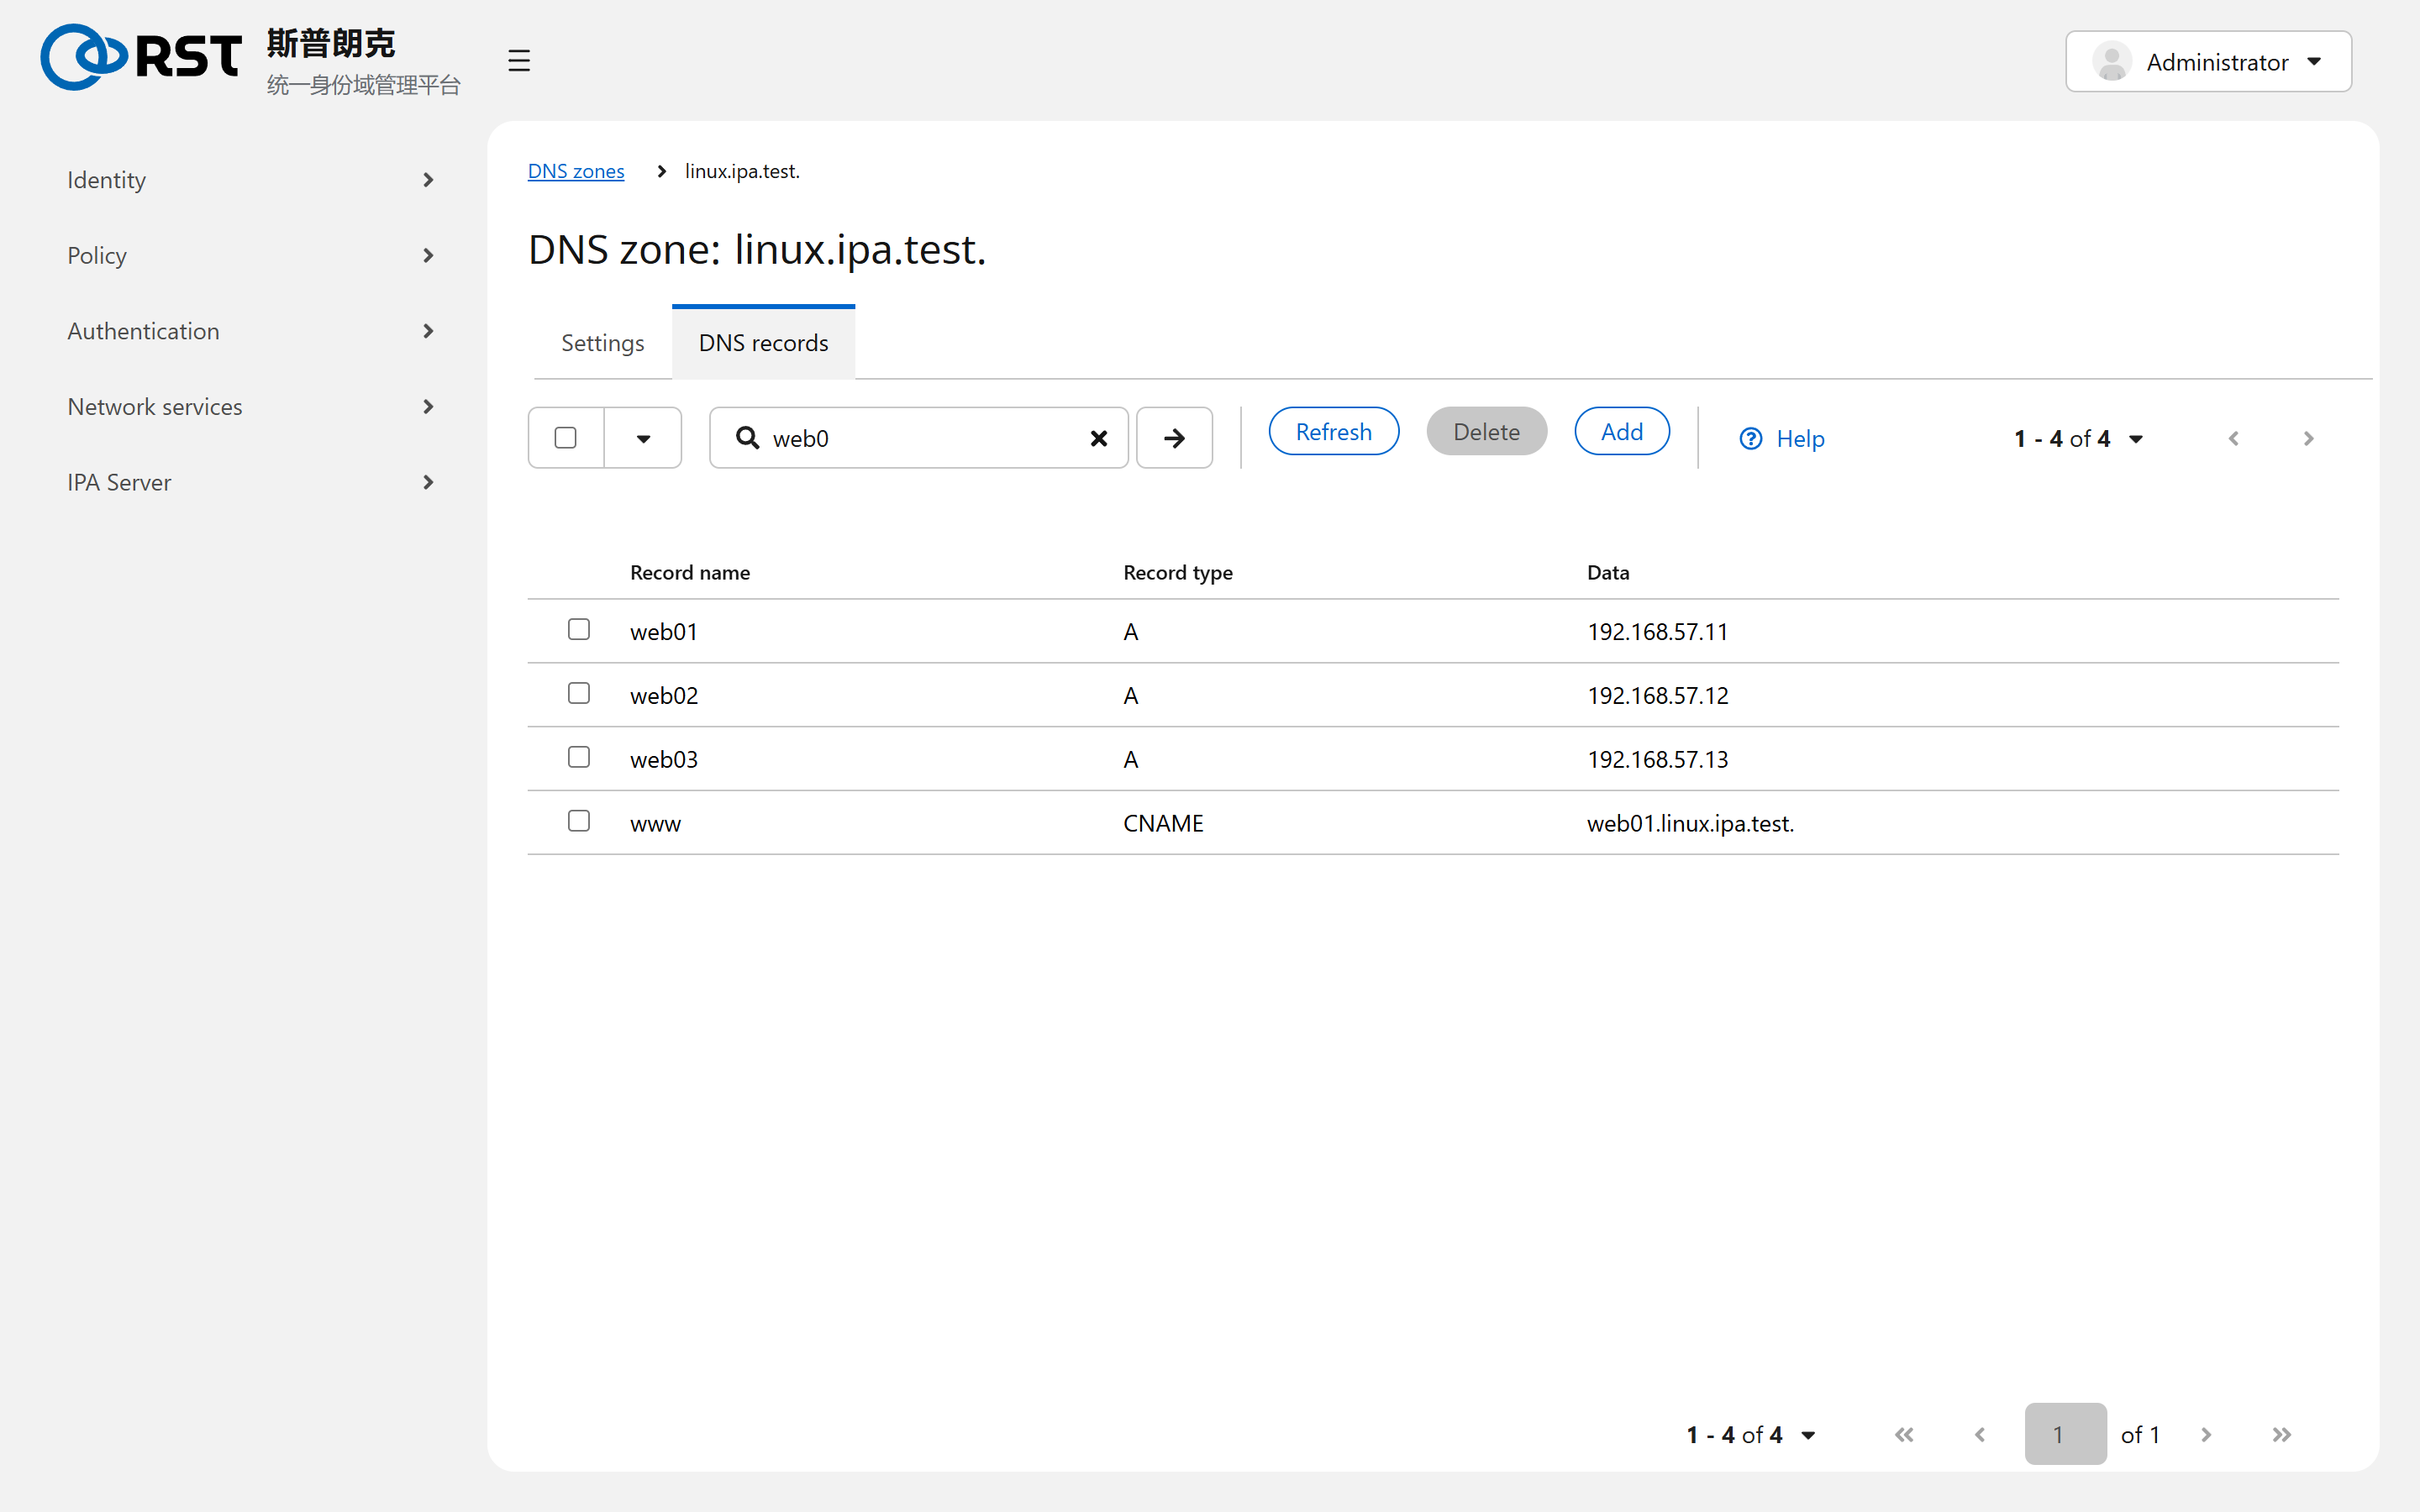
One record name may hold several types (@ has NS, A and SOA). _kerberos, _ldap._tcp and the other SRV, URI and TXT records are maintained by the installer. Clients discover servers through them; do not edit them.
Host records maintain themselves:
| Action | Effect |
|---|---|
ipa host-add --ip-address= | Creates the A record, and the PTR if the reverse zone exists |
ipa-client-install | The client writes its own A and AAAA records through nsupdate; later IP changes are pushed by sssd's dyndns_update |
ipa host-del | Keeps the records. --updatedns removes them |
Forward zones and forward policy
A forward zone (DNS forward zones) hands queries for a name to a given server. Forwarding ad.ipa.test. to the AD DC is a prerequisite of the AD trust (AD trust prerequisites).
The global config and every DNS server carry forwarders and a forward policy:
| Policy | Meaning |
|---|---|
| Forward first | Ask the forwarders, recurse on failure |
| Forward only | Ask the forwarders only, fail otherwise |
| Forwarding disabled | Recurse |
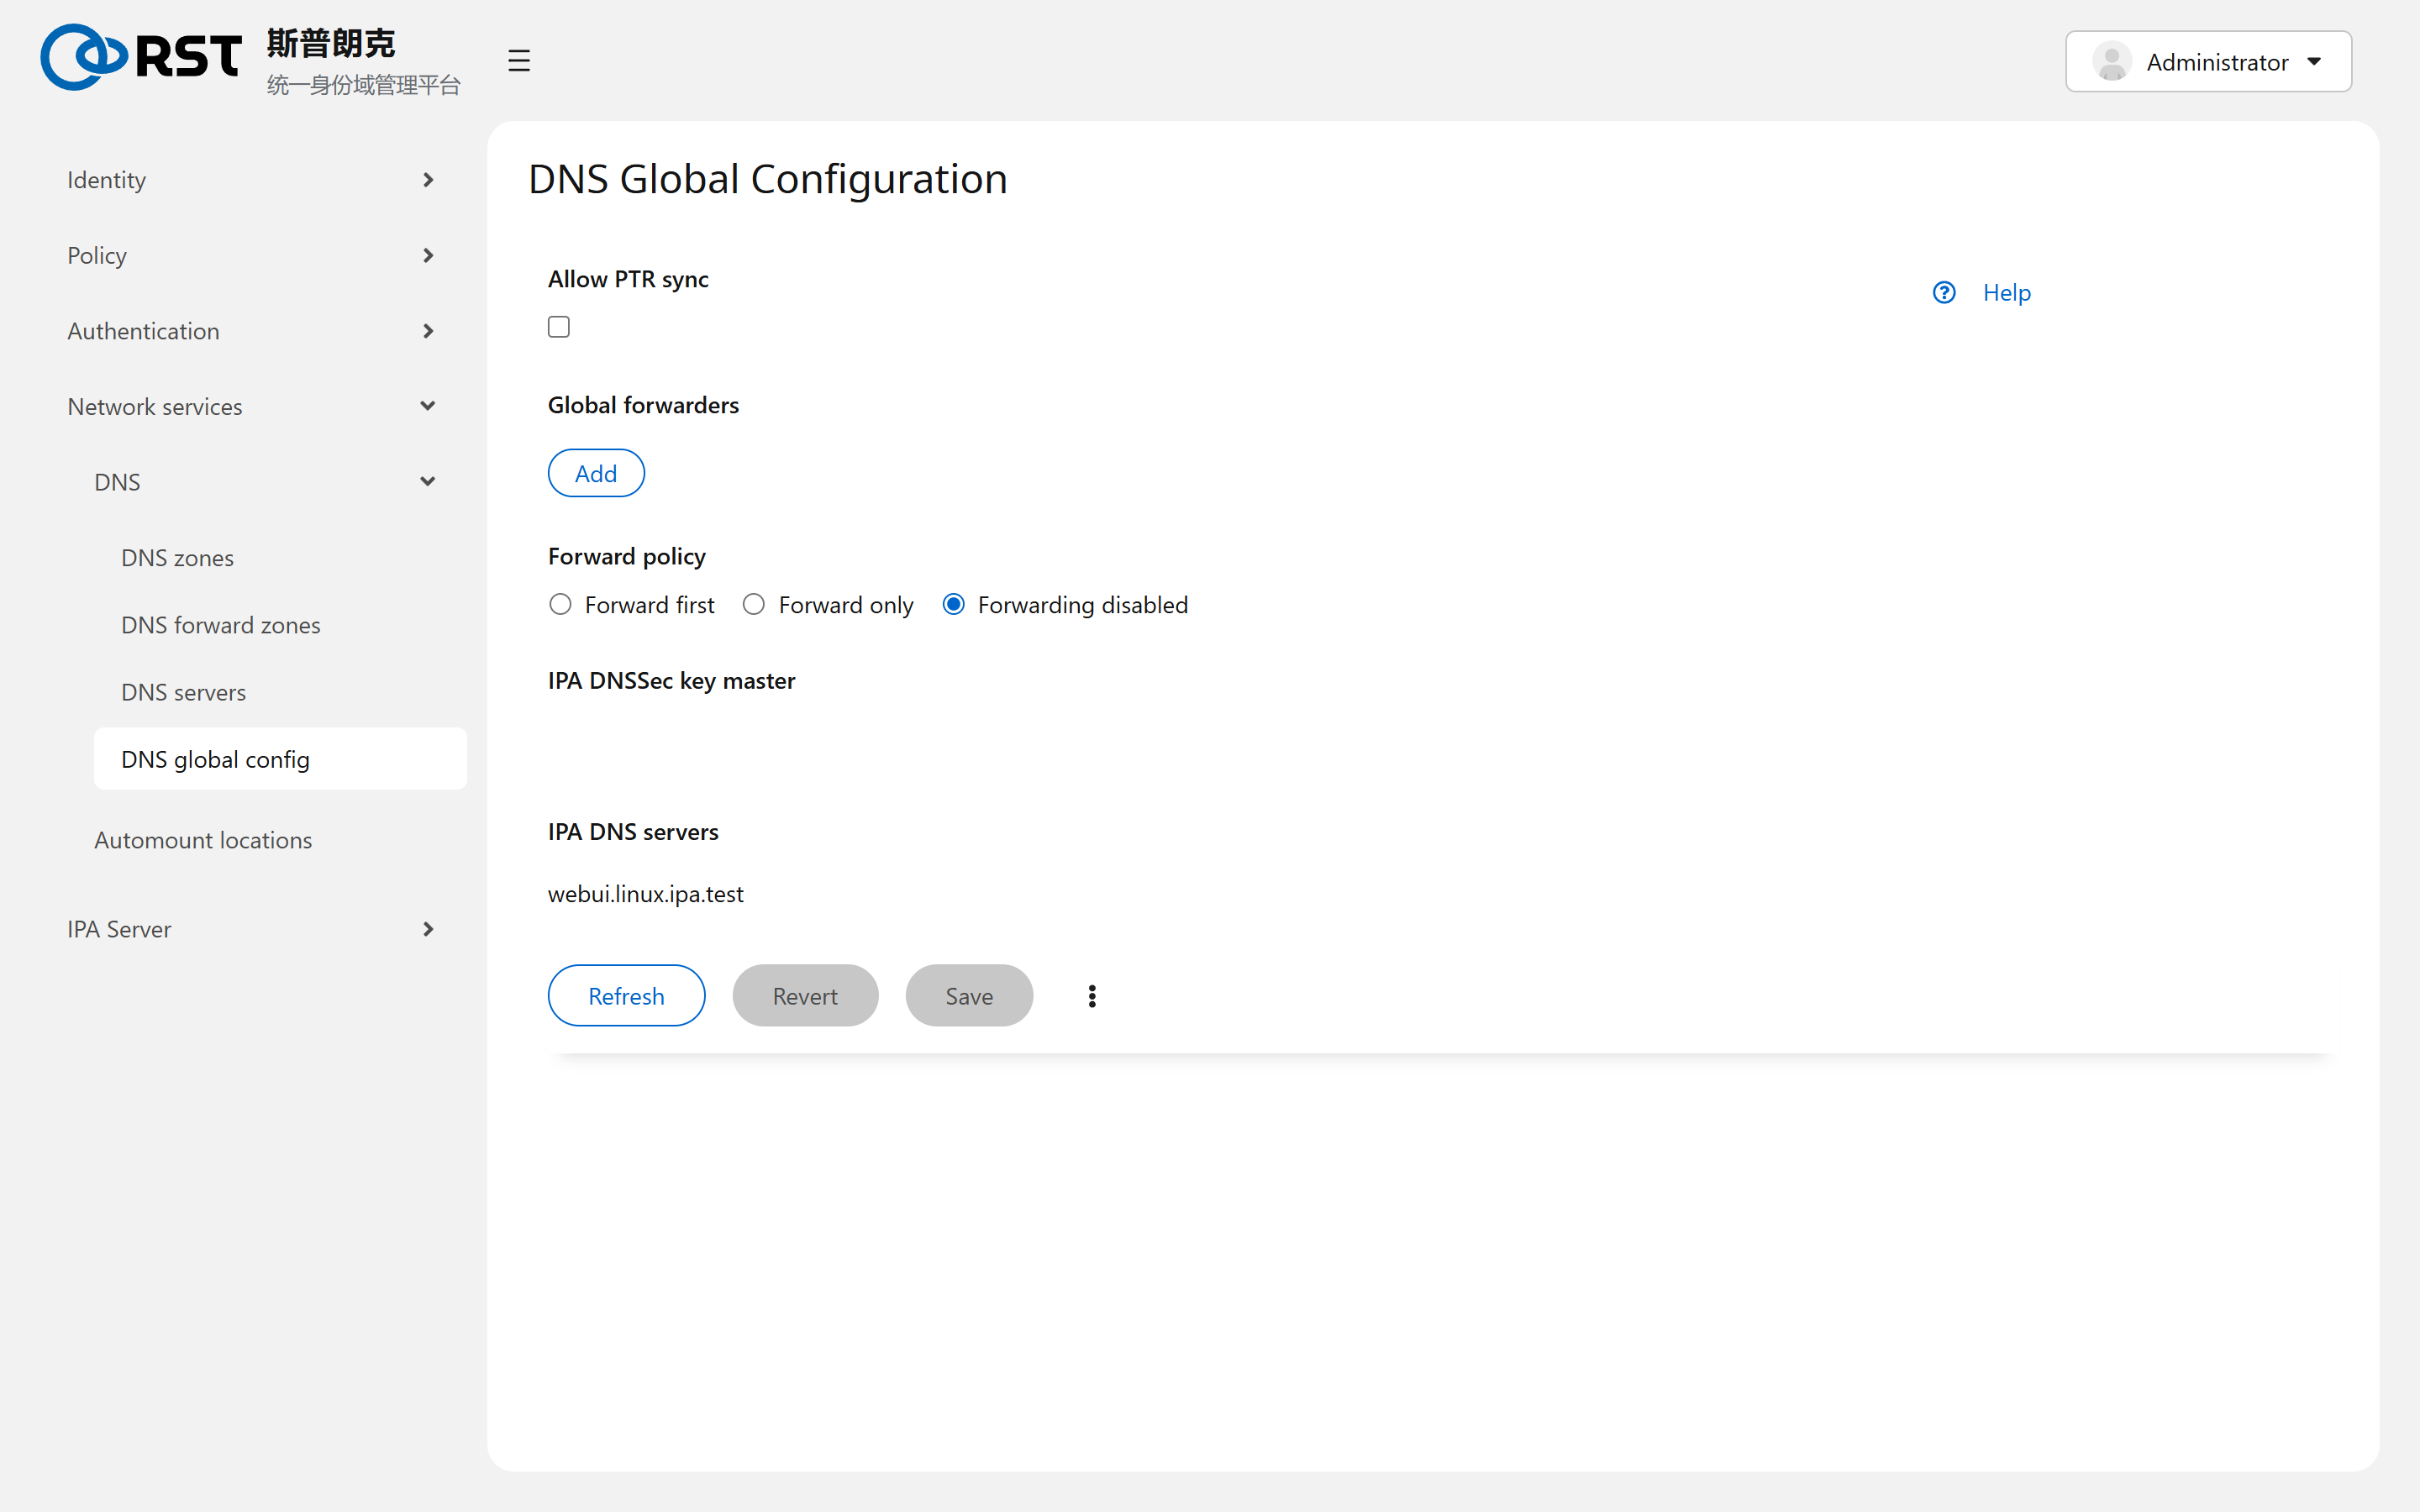
Per-server settings override the global ones. The IPA server's own /etc/resolv.conf points at 127.0.0.1, with the forwarders here handing external queries on.
Boundaries
| Topic | Notes |
|---|---|
| Role | IPA DNS is not a general-purpose authoritative server: no views, no geo answers. Business domains stay on the corporate DNS, which delegates the IPA domain |
| Backup | Zone data lives in LDAP and ipa-backup covers it. named zone files do not exist |
| Deleting a zone | Irreversible, and breaks SRV discovery for clients joining afterwards |
Certificate mapping
Requires the ca module. How a client certificate or smart card is matched to a user, the matching and mapping rule syntax, priority, the global Prompt for username switch, and checking a rule on the match page.
Automount locations
Requires the automount module. The location, map and key structure, the standard on-demand home directory setup, enabling clients, and why the UI stops at locations.