

Password policies
Requires the pwpolicy module. Global versus per-group policies, how priority picks the one a user gets, field defaults and meanings, lockout and unlock.
Requires the pwpolicy module. Policies are defined per group; a user gets the highest-priority policy among the groups they belong to, or global_policy when no such group applies. The KDC enforces it: length / history / character classes on password change, failure counting and lockout on authentication.
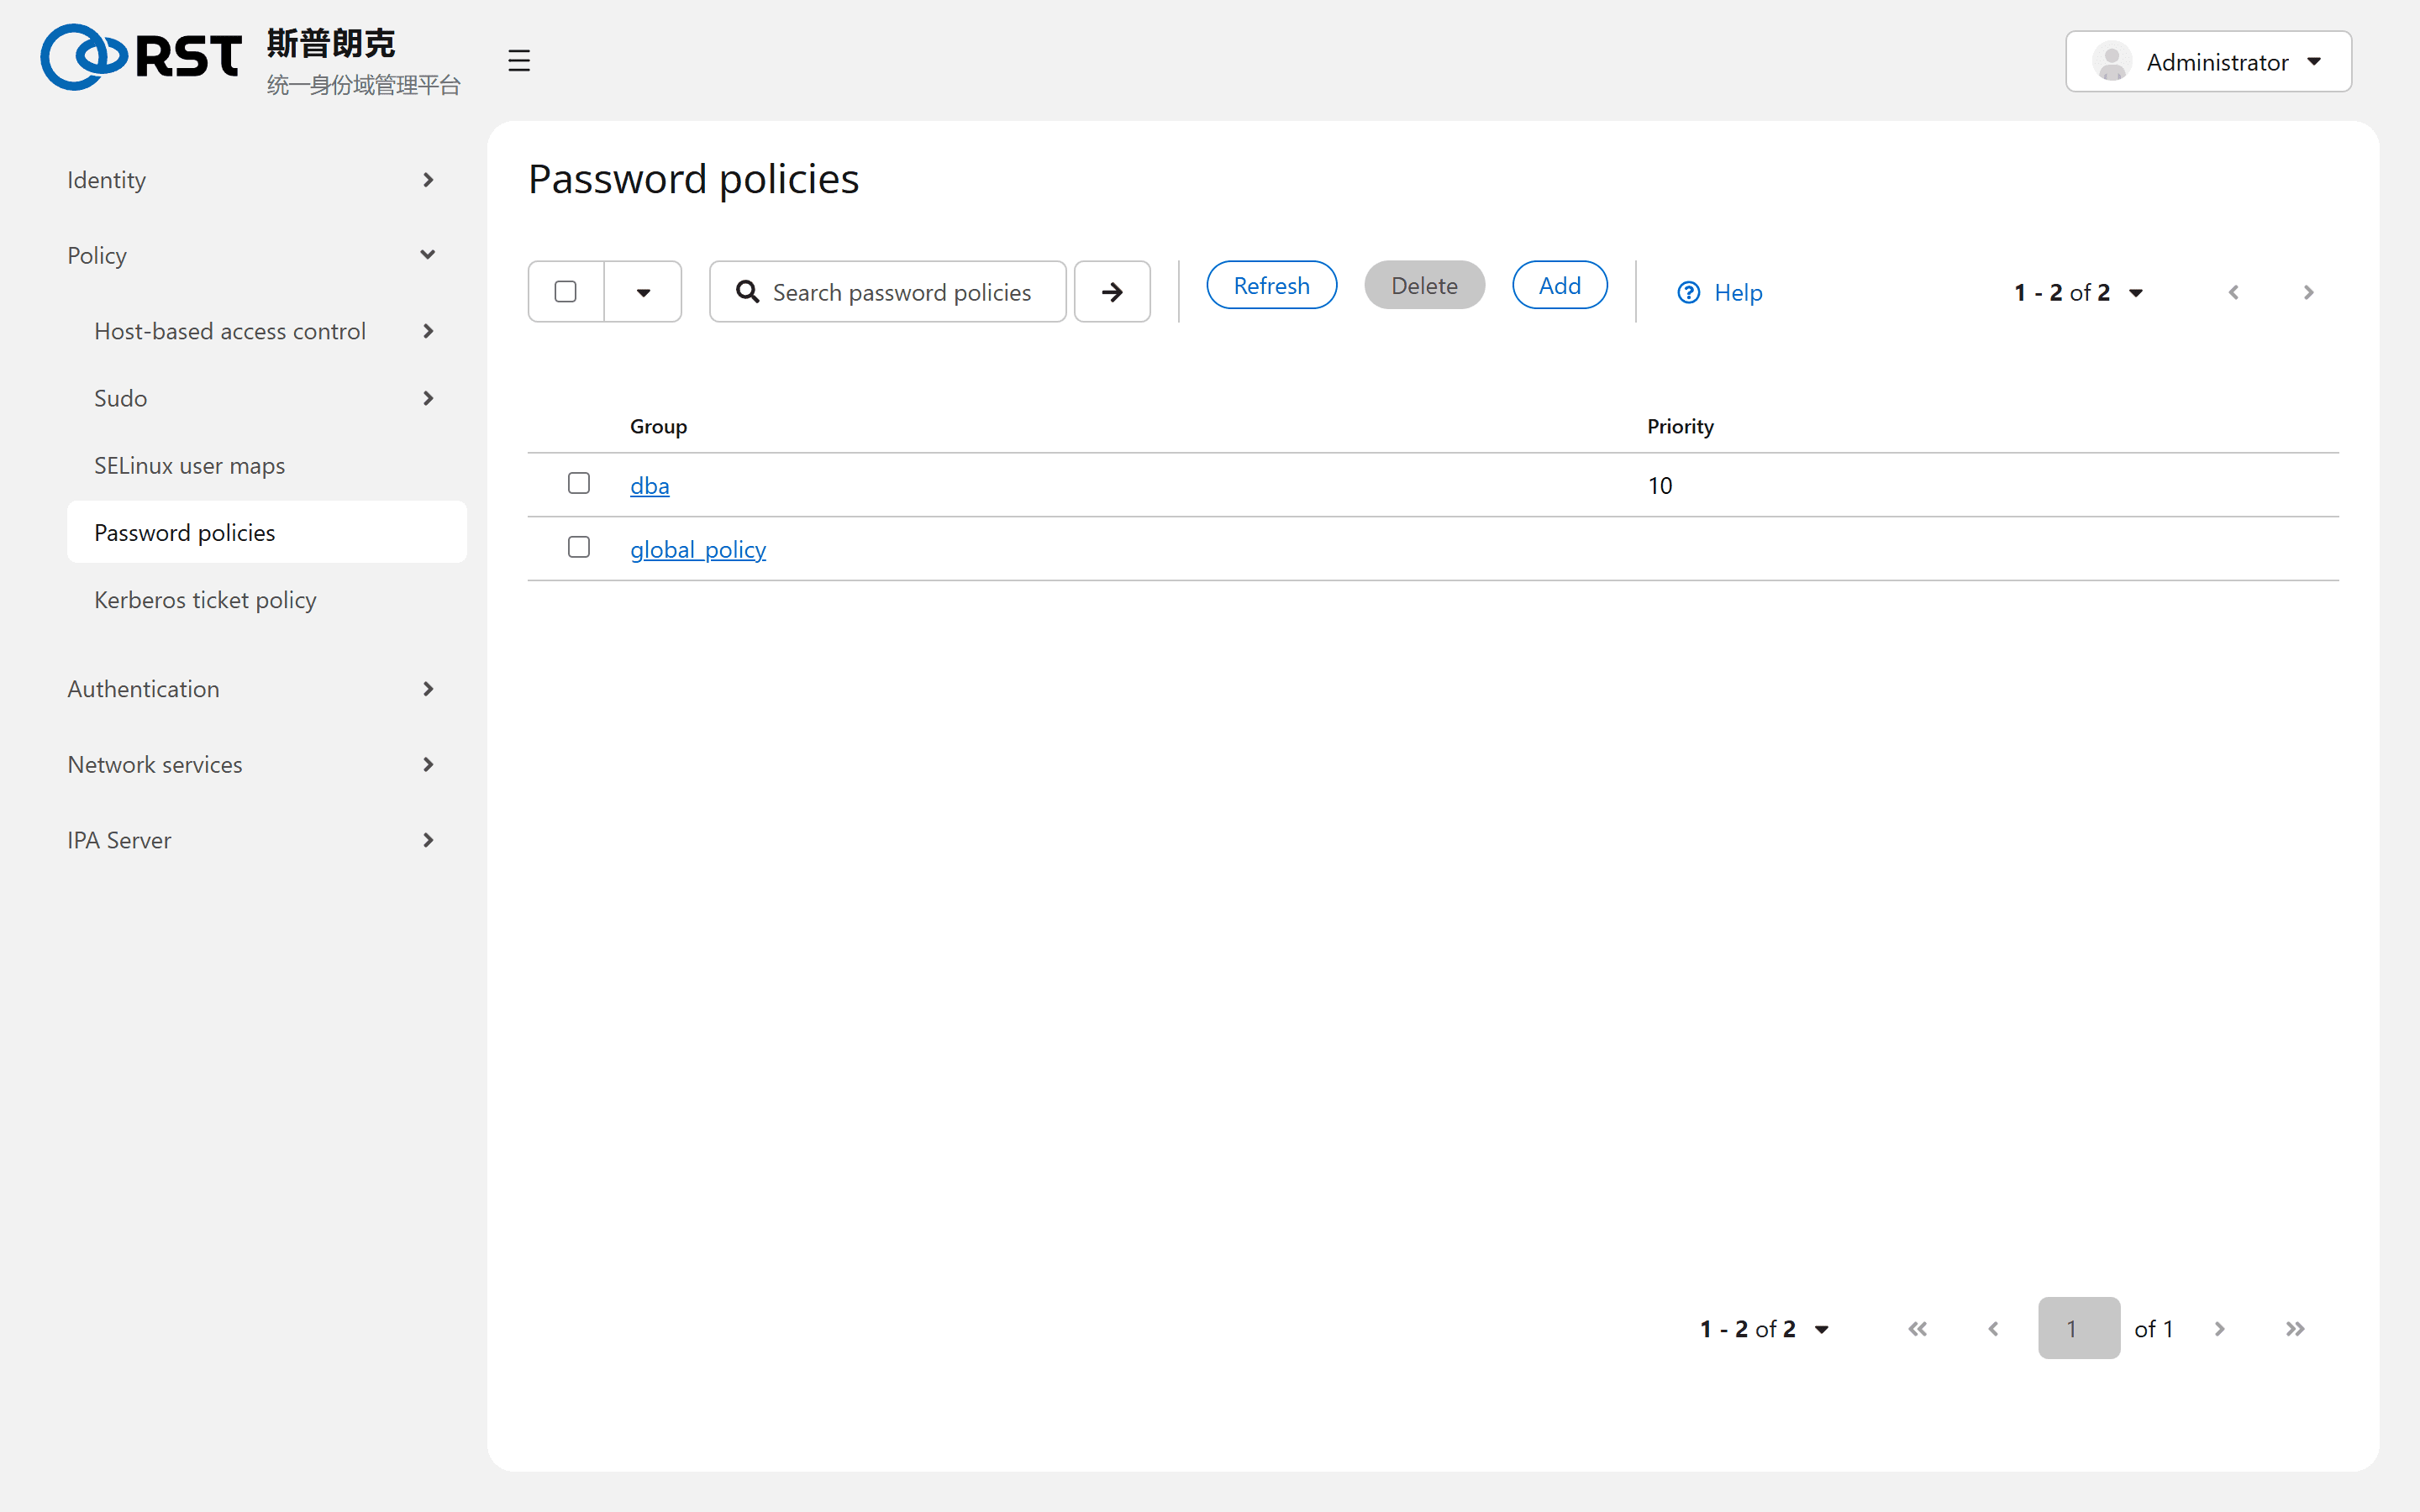
Which policy applies
| Column | Meaning |
|---|---|
| Group | the user group the policy is bound to, one policy per group |
| Priority | lower number wins. global_policy has none and always comes last |
A user in both dba (priority 10) and devops (priority 20) gets dba's. The user's detail page shows the effective policy under "Password policy"; ipa pwpolicy-show --user=<uid> does the same.
Fields
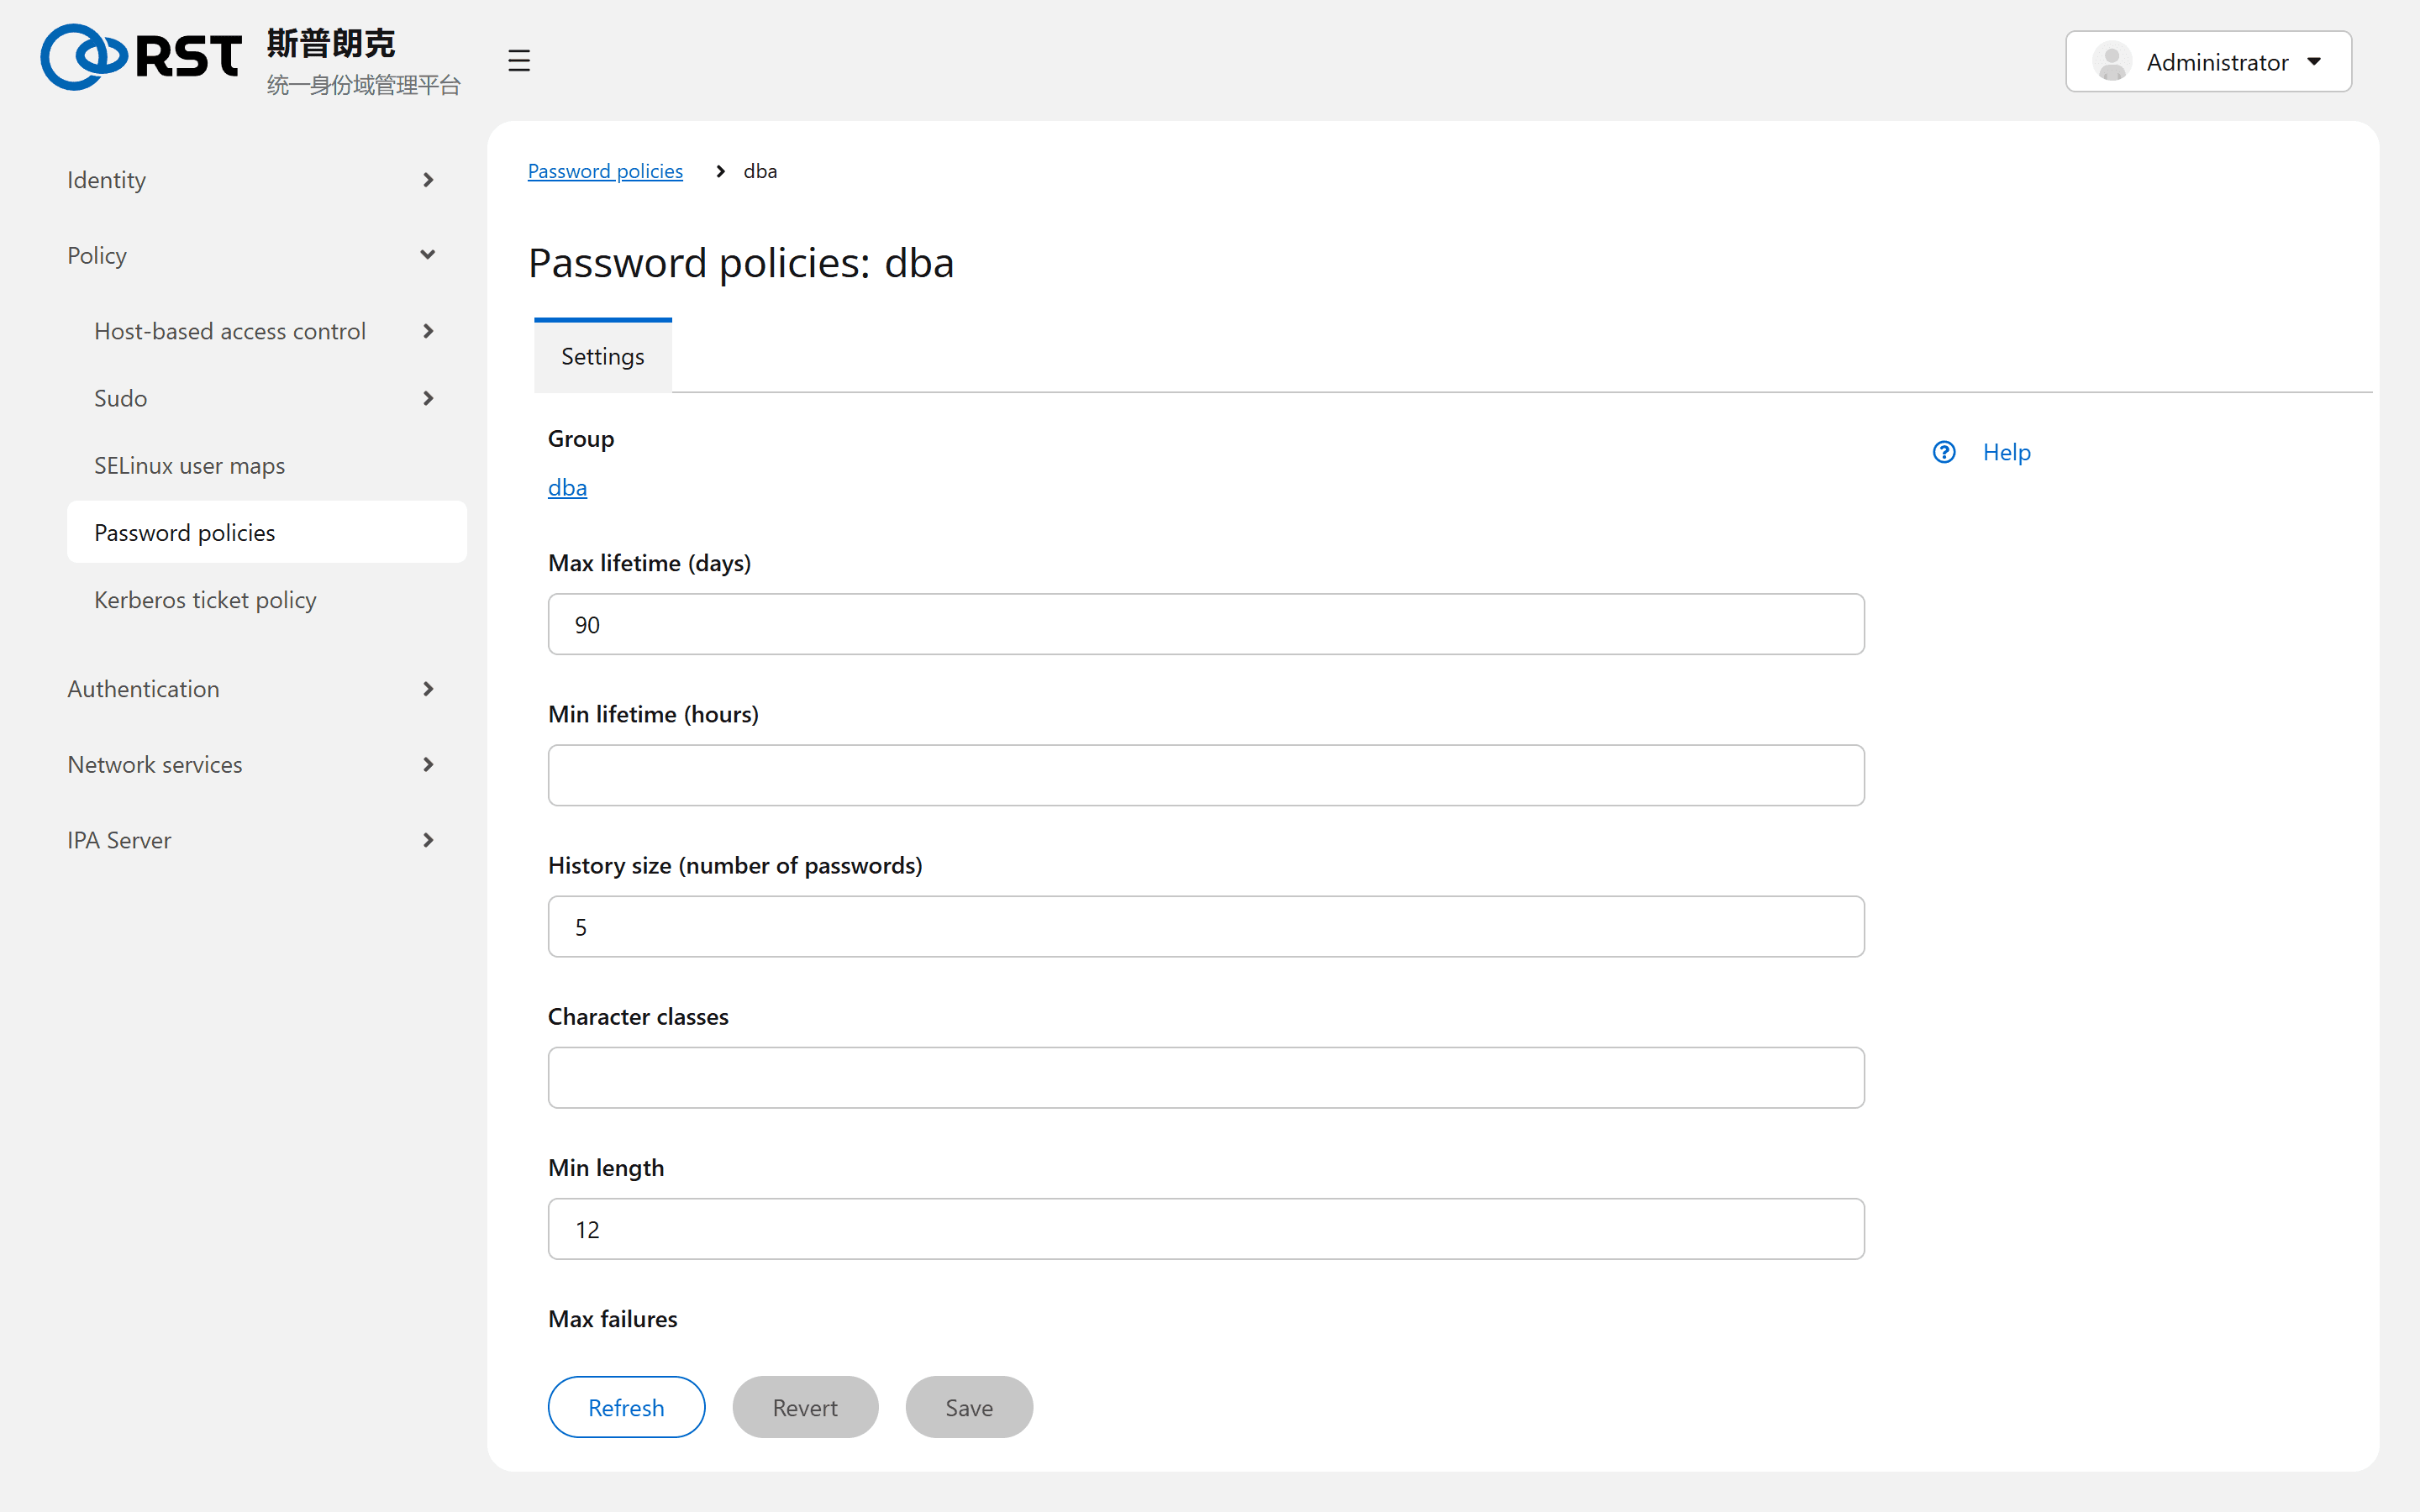
| Field | Global default | Meaning |
|---|---|---|
| Max lifetime (days) | 90 | must change by then; 0 never expires |
| Min lifetime (hours) | 1 | no second change within this window, so history cannot be cycled through |
| History size | 0 | last N passwords cannot be reused |
| Character classes | 0 | at least this many of upper, lower, digit, symbol, other |
| Min length | 0 | characters |
| Max failures | 6 | consecutive failures before lockout; 0 never locks |
| Failure reset interval (seconds) | 60 | failures further apart than this reset the counter |
| Lockout duration (seconds) | 600 | automatic unlock after this; 0 locks until an administrator unlocks |
| Grace login limit | -1 | logins still allowed after expiry so the password can be changed; -1 unlimited |
| Priority | – | see above |
Finer complexity checks (max repeated characters, dictionary, username substring) are CLI only: ipa pwpolicy-mod <group> --maxrepeat= --maxsequence= --dictcheck= --usercheck=.
An admins member setting someone else's password bypasses history and min lifetime, but the new password expires immediately and must be reset at first login.
Lockout and unlock
Failure counts are kept per IPA server and not replicated; with two masters a user effectively has twice the attempts. Inspect and unlock:
ipa user-status zhangwei        # failures and last failure per server
ipa user-unlock zhangwei
Boundaries
- Policies apply to IPA users only; AD users are governed by AD's policy.
- The group must be a POSIX or non-POSIX user group; an External group cannot carry a policy.
- Deleting a group deletes its policy.
SELinux user maps
Change the SELinux user an IPA login runs as from the default unconfined_u to a confined one; how maps match, the list of available SELinux users and its order.
Kerberos ticket policy
Requires the krb-sso module. Global ticket life and renewal caps, separate caps per authentication method (OTP / RADIUS / PKINIT / IdP / passkey), and when a change takes effect.