

Console overview
What each of the five navigation groups manages, which pages are controlled by licence modules, and which tasks require the CLI.
This page is for administrators using the IDMatrix console. It covers the navigation layout and how the licence shapes the interface. Fields and actions of each page are covered on the corresponding guide page.
The console is at https://<FQDN>/ipa/modern-ui/, user admin. It is a derivative of the FreeIPA web UI: same objects, same API, plus localisation, licence gating and an activation page. The classic UI at https://<FQDN>/ipa/ui remains available for cross-checking.
Pages
The left navigation has five groups. Pages with a module in the last column appear only when the licence includes that module; unlicensed pages are hidden as a group, not greyed out.
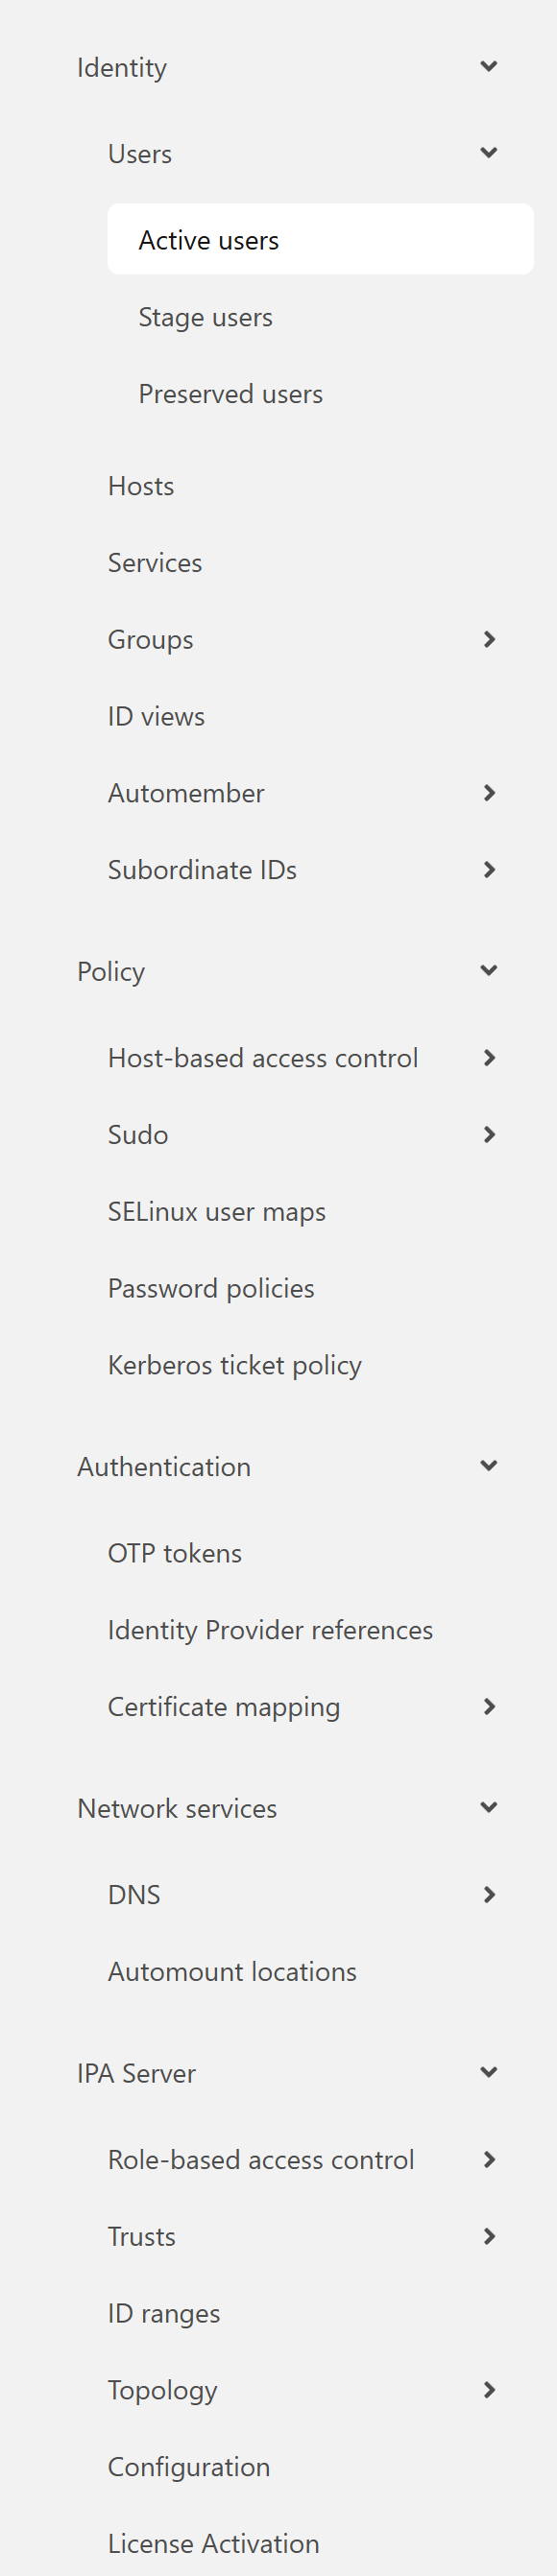
Identity
| Page | Manages | Module |
|---|---|---|
| Users (Active, Stage, Preserved) | Three user states. Stage is pre-created and inactive; Preserved is an archive of deleted users that can be restored | None |
| Hosts | Hosts joined to the domain. Capped by the licence; host-add is refused beyond the cap | None |
| Services | Service principals on hosts (HTTP/, ldap/, nfs/ and so on); certificates and keytabs are issued to them | None |
| Groups (User groups, Host groups, Netgroups) | Groups. A user group created as External maps an AD group | None |
| ID views | Override a user's uid, shell or home on selected hosts without changing the global value | None |
| Automember (User Group Rules, Host Group Rules) | Automatic group membership by attribute | None |
| Subordinate IDs | subuid and subgid allocation for rootless containers | None |
Policy
| Page | Manages | Module |
|---|---|---|
| Host-based access control (rules, services, service groups, test) | Who may log in from where to which service on which host. The HBAC test page is available from 1.0.3; ipa hbactest is the CLI equivalent | hbac |
| Sudo (rules, commands, command groups) | Central sudo rules, fetched by client sssd | None |
| SELinux user maps | SELinux user by user and host group | None |
| Password policies | Length, history, lockout threshold, per group, with the global policy as fallback | pwpolicy |
| Kerberos ticket policy | Maximum ticket life and renewable life | krb-sso |
Authentication
| Page | Manages | Module |
|---|---|---|
| OTP tokens | Users' TOTP and HOTP tokens | None |
| Identity Provider references | External OIDC identity sources | None |
| Certificate mapping (rules, global config, match) | How a client certificate or smart card maps to a user | ca |
Network services
| Page | Manages | Module |
|---|---|---|
| DNS (zones, forward zones, servers, global config) | Zones, forward zones and per-server forwarders of the built-in DNS. Not applicable with IPA_SETUP_DNS=false | dns |
| Automount locations | NFS automount locations, maps and keys | automount |
IPA Server
| Page | Manages | Module |
|---|---|---|
| Role-based access control (Roles, Privileges) | Delegated administration: who may edit users, who may edit DNS | None |
| Trusts, Trusts global config | AD trust status and ID range type | ad-trust |
| ID ranges | uid and gid ranges for local users and each trusted domain | None |
| Topology, Topology graph | Replication topology between IPA servers | None |
| Configuration | Global defaults: shell, home directory, default group, search limits | None |
| License Activation | Host fingerprint, .lic upload, current licence state | None |
Licence effects on the console
| Licence state | Console |
|---|---|
| Not activated or expired | Red banner at the top; every page read-only |
| Activated | Navigation groups whose module is not in mods are hidden |
| Expiring within 30 days | Yellow banner |
On the user detail page, the SSH public keys block appears only with the ssh-keys module. The Certificates block always appears; certificate issuance is in every tier.
Whether a page is visible is decided by mods in /var/lib/idmatrix-license/status.json, never by the browser cache.
CLI tasks
The console covers day-to-day create, read, update and delete. The following tasks go through the CLI (ipa commands after kinit admin):
| Task | Command |
|---|---|
| Create the AD trust | ipa trust-add; see AD trust |
| Bulk import | Loop over ipa user-add, or ipa migrate-ds from an existing LDAP |
| Count managed hosts | ipa host-find --sizelimit=0 | tail -1 |
| Add a replica, inspect replication | ipa-replica-install, ipa topologysegment-find |
| Backup and restore | ipa-backup, ipa-restore |
| Full self-check | ipa-healthcheck |
| Simulate an access decision | ipa hbactest --user u --host h --service sshd; the HBAC test page is available from 1.0.3 |
Routine checks
| Frequency | Task |
|---|---|
| Daily | No red banner in the console; idmatrix-backup.timer ran the previous night |
| Weekly | Full ipa-backup, copied off-host |
| Monthly | Run ipa-healthcheck; check the licence expiry date |
| Before changes | Full backup before trust setup, bulk policy edits or upgrades |
Upgrade and backup
Which layers upgrade in place, the upgrade and rollback steps, what the daily backup produces, when to take a full backup, and the difference between restoring to the same machine and a new one.
Users
The three user states, why delete means move to Preserved, what each block of the detail page holds, and which fields depend on licence modules.