Back to products
Subscription

RST AI Copilot for Splunk

Ask Splunk in plain language. Turns a question into SPL, explains what an existing search does, and shows what a query will return before it runs.

A 14-day trial licence, issued as soon as you sign in.

Read the hands-on evaluation
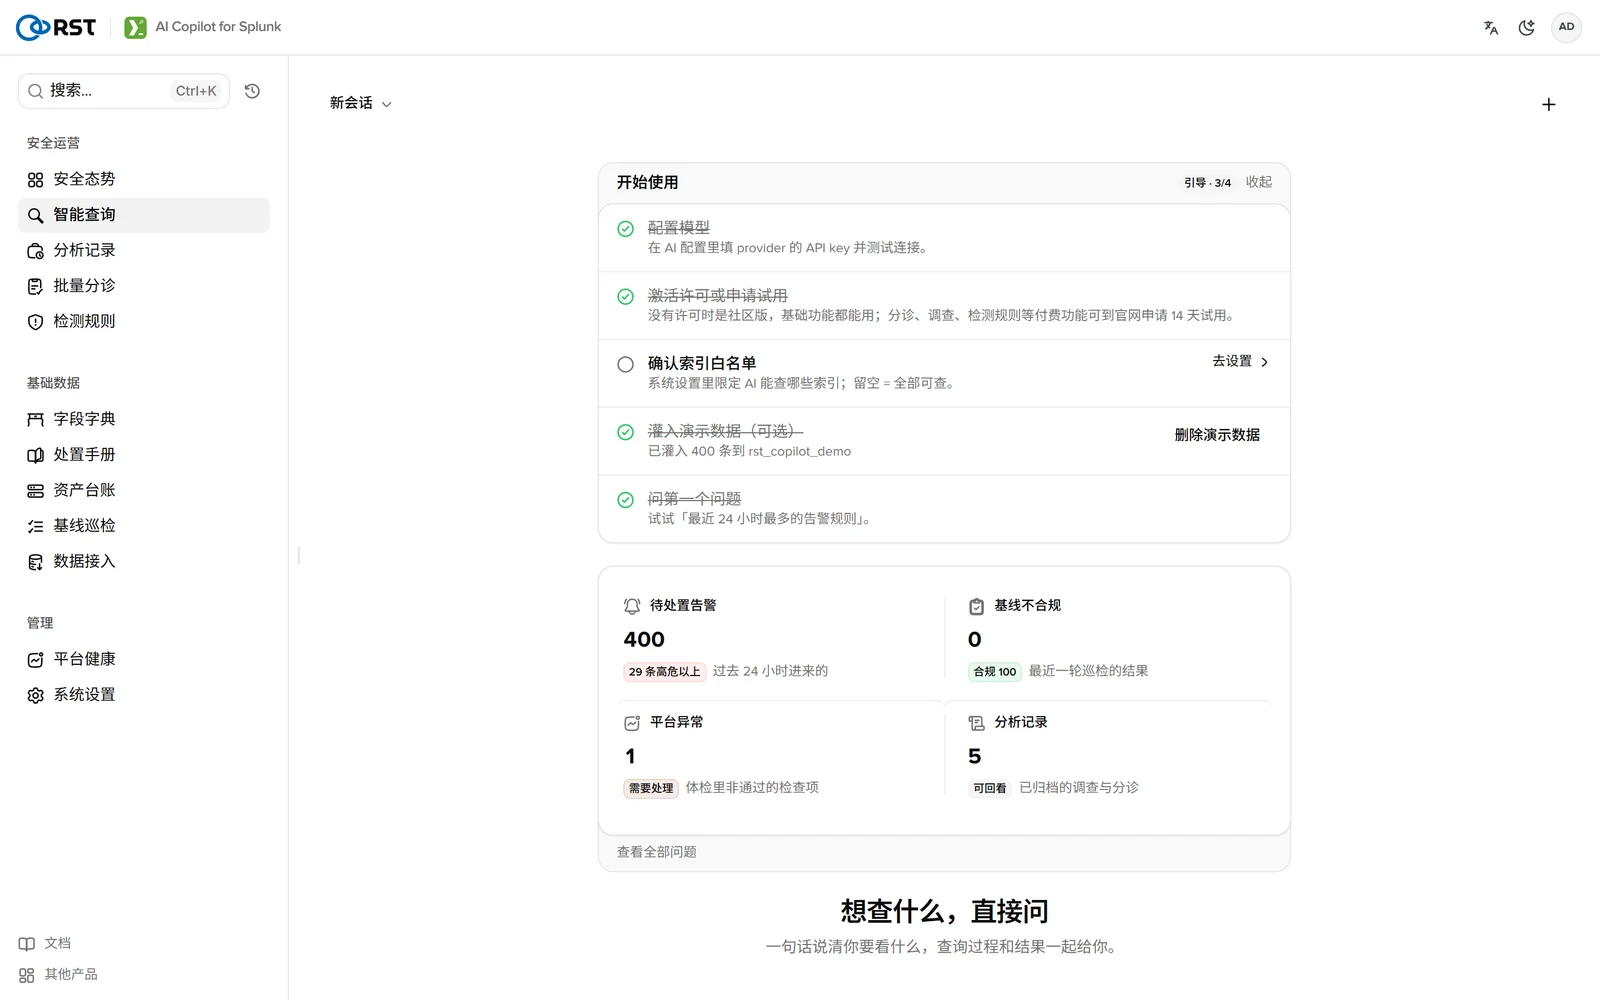
RST AI Copilot for Splunk interface

Overview

Most people who need an answer out of Splunk cannot write SPL, and the people who can spend their day writing it for everyone else.

RST AI Copilot for Splunk sits beside Splunk rather than in front of it. It translates a question into SPL, explains a search someone else wrote, and previews the fields a query will return before it touches an index. Higher editions add a knowledge base of your own searches, saved conversations, and alert triage and investigation.

Licences are issued per Splunk instance and can be moved between hosts from the console. Nothing about your data leaves the instance unless you configure it to.


Capabilities

01

Natural language to SPL

Describe the question; get the search. The generated SPL is shown in full and stays editable, so it can be read, corrected and kept rather than trusted blindly.

02

Explain an existing search

Paste a search nobody remembers writing and get a plain-language account of what it does, which indexes it touches and what it will return.

03

Field preview before you run

See which fields a query will produce before it executes. Catches the empty result set and the mistyped field name while they are still cheap.

04

Alert triage and investigation

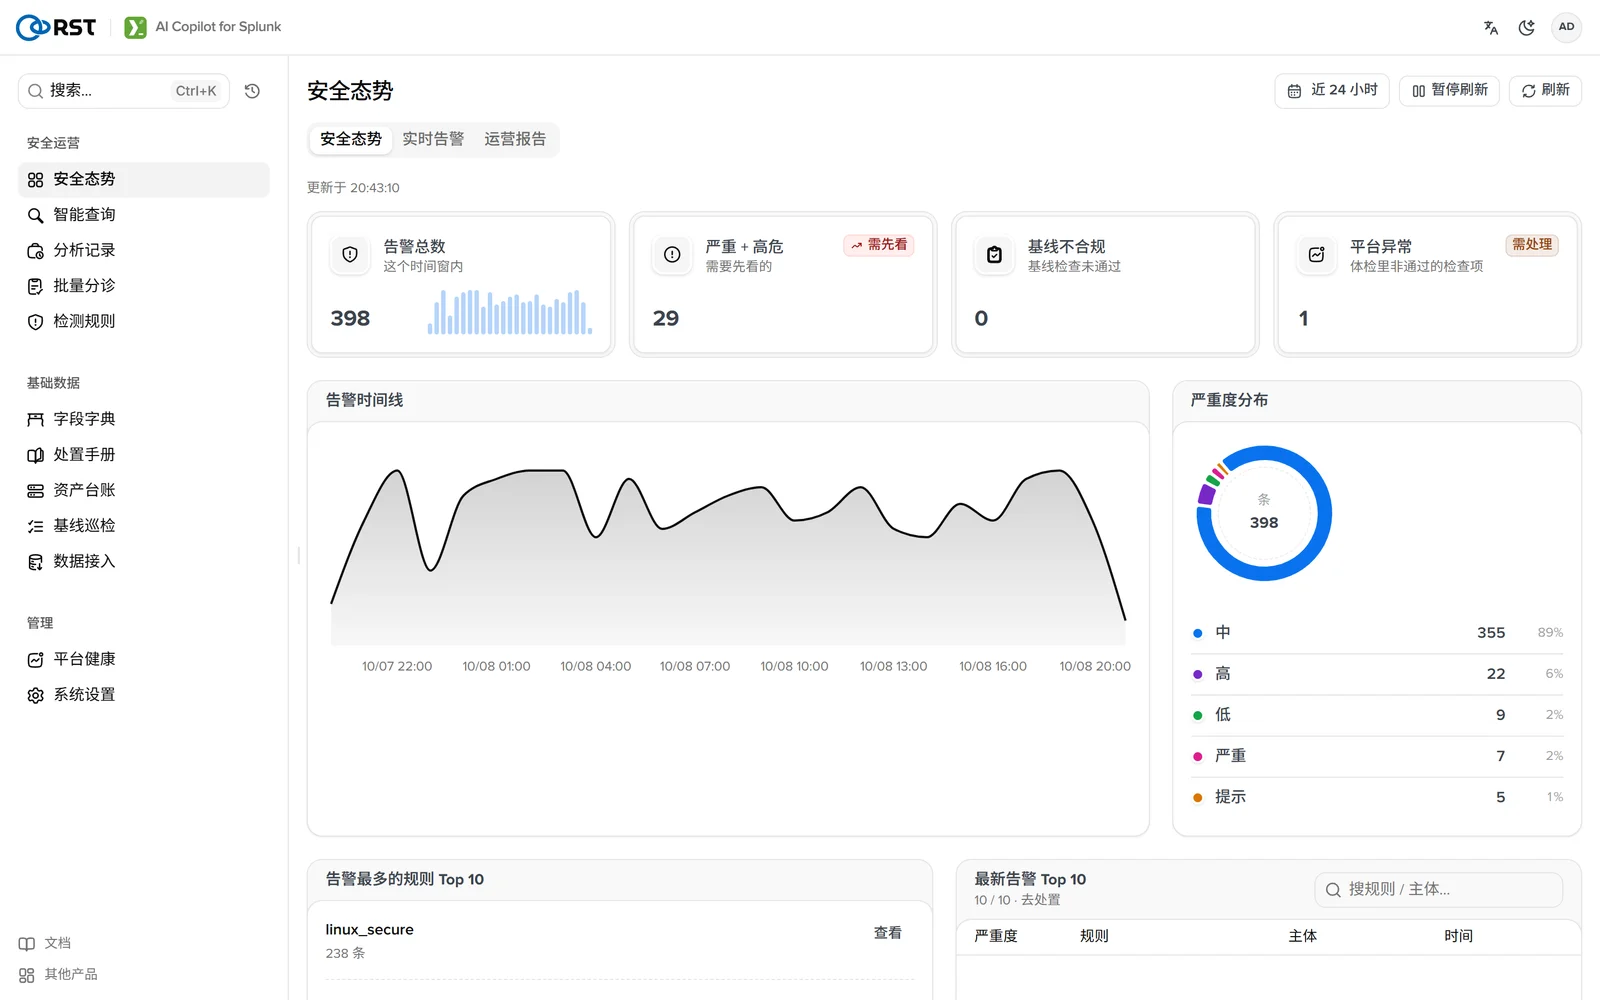
Takes a firing alert and assembles the related events, affected hosts and prior occurrences an analyst would gather by hand, so the first ten minutes are already done. Professional and above.

05

Knowledge base and saved conversations

Your own searches, runbooks and past investigations become material the copilot draws on, so answers reflect how your estate is actually indexed. Available in every edition, no licence required.

Editions

Community

Free

Includes

  • Natural language to SPL with follow-ups
  • Search-bar commands | copilot and | splexplain
  • Log explainer and field dictionary
  • Knowledge base and solutions library
  • ATT&CK coverage heatmap
  • Data onboarding assistant
  • Field masking (cloud, private, offline)
  • RBAC and local audit log

Professional

Recommended
Limited-time offer

$99/user/yr

$9.9/user/mo

Includes

  • Batch alert triage with recommended action
  • Investigation context assembled automatically
  • Detection-rule drafting with ATT&CK mapping
  • Platform ops copilot
  • Alert noise reduction
  • Solutions library
  • Scheduled operations reports

Enterprise

Pricing on request

Unlimited search heads · 12-month term

End User License Agreement

What each edition includes

Capability
CapabilityCommunityNo licence · Free for goodProfessionalRecommended1 search head · 12-month termEnterpriseUnlimited search heads · 12-month term
PriceFree$99/user/yrPricing on request
Batch alert triage with recommended actionNot includedIncludedIncluded
Investigation context assembled automaticallyNot includedIncludedIncluded
Detection-rule drafting with ATT&CK mappingNot includedIncludedIncluded
Platform ops copilotNot includedIncludedIncluded
Alert noise reductionNot includedIncludedIncluded
Solutions libraryNot includedIncludedIncluded
Scheduled operations reportsNot includedIncludedIncluded
Verdicts written back to Enterprise SecurityNot includedNot includedIncluded
ServiceNow / Jira ticket creationNot includedNot includedIncluded
MCP server for external AI assistantsNot includedNot includedIncluded
Audit forwarding to an external SIEMNot includedNot includedIncluded
Multi-provider LLM failover / high availabilityNot includedNot includedIncluded
Offline / air-gapped licence issuanceNot includedNot includedIncluded

Included in every edition

The free Community Edition includes all of the following, and so do Professional and Enterprise. No licence needed.

  • Smart query: natural language to read-only SPL, dry-run repair, follow-up turns with saved conversations
  • Search-bar commands: `| copilot "question"` generates and runs SPL; `| splexplain` explains and optimises a query
  • Field masking, all three modes: cloud, private model, fully air-gapped, applied before data leaves the instance
  • Knowledge base: existing Splunk objects and runbooks as reference material; corrections made in conversation become rules
  • Security posture overview and live alert intake
  • ATT&CK coverage heatmap
  • Asset ledger, baseline checks, field dictionary, data onboarding
  • Call audit: every model call and settings change is recorded
  • Sign-in and roles come from Splunk's own user model

Need Enterprise, or a deployment shape not in the table? Contact sales